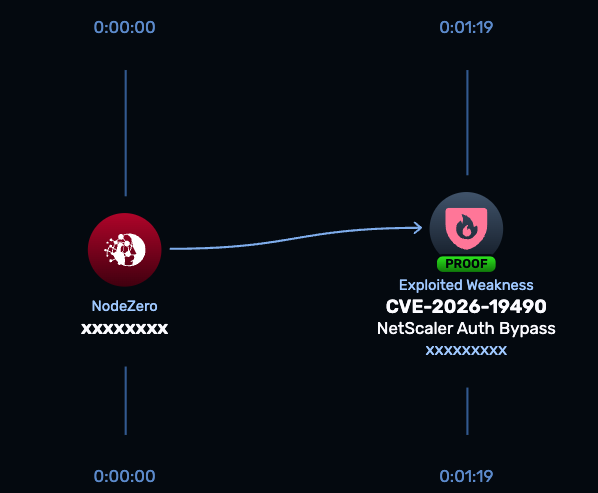
CVE-2026-19490 is an authentication bypass vulnerability affecting certain customer-managed NetScaler ADC and NetScaler Gateway appliances. An unauthenticated remote attacker may be able to bypass authentication when an affected appliance is configured as a Gateway or AAA virtual server and meets the applicable build-specific conditions. The vulnerability is rated Critical (CVSS 3.x score of 9.8). CISA added it to its Known Exploited Vulnerabilities catalog on September 9, 2026.
Citrix classifies the flaw as an authentication bypass using an alternate path or channel (CWE-288). The affected appliance must be configured as a Gateway supporting SSL VPN, ICA Proxy, CVPN, or RDP Proxy, or as an AAA virtual server. The additional SAML requirement varies by build:
14.1-43.55 and earlier: A Gateway or AAA virtual server configuration meets Citrix’s stated precondition.
14.1-43.56 and later: A SAML action must also be configured.
14.1-66.68-FIPS and later: A SAML action must also be configured.
13.1-61.27 and earlier: A Gateway or AAA virtual server configuration meets Citrix’s stated precondition.
13.1-61.28 and later: A SAML action must also be configured.
13.1 FIPS: Citrix specifies a Gateway or AAA virtual server configuration as the precondition.
These conditions apply to builds below the fixed versions listed below. The vulnerability can be reached over a network without prior privileges or user interaction. Citrix’s bulletin does not describe the exploit mechanism beyond its authentication bypass classification, so teams should not assume a particular request path or post-bypass level of access.
Stop Guessing, Start Proving
NodeZero® Proactive Security Platform — Rapid Response
A NodeZero Rapid Response test has been developed to safely validate whether this authentication bypass can be exploited in your environment. The test uses real attack techniques to give teams evidence of exposure.
Run the Rapid Response test: Determine whether the affected Gateway or AAA service is exploitable.
Patch immediately: Upgrade affected appliances to the appropriate Citrix fixed build.
Re-run the test: Confirm the vulnerability is no longer exploitable after remediation.
CISA also calls for forensic triage for this KEV entry. Retesting a patched appliance verifies the fix; it does not determine whether the appliance was compromised before patching.
Affected versions & patch
Citrix identifies the following customer-managed builds as affected, subject to the applicable configuration preconditions:
NetScaler ADC and NetScaler Gateway 14.1 before 14.1-73.32
NetScaler ADC and NetScaler Gateway 13.1 before 13.1-63.21
NetScaler ADC 14.1 FIPS before 14.1-73.32 FIPS
NetScaler ADC 13.1 FIPS and 13.1 NDcPP before 13.1-37.277
Secure Private Access Hybrid deployments using customer-managed NetScaler instances are also in scope.
Upgrade to the fixed build for the appliance’s release train:
14.1: 14.1-73.32 or later
13.1: 13.1-63.21 or later
14.1 FIPS: 14.1-73.32 FIPS or later
13.1 FIPS and 13.1 NDcPP: 13.1-37.277 or later
Citrix lists no workaround in its bulletin. The bulletin applies to customer-managed appliances; Cloud Software Group states that it updates Citrix-managed cloud services and Citrix-managed Adaptive Authentication.
August 19, 2026: Citrix published its security bulletin and fixed-build guidance.
September 9, 2026: CISA added CVE-2026-19490 to its Known Exploited Vulnerabilities catalog and marked forensic triage as required.
September 28, 2026: Horizon3.ai releases a NodeZero Rapid Response test for CVE-2026-19490, enabling customers to validate exposure and verify remediation.
Citrix NetScaler ADC and NetScaler Gateway Security Bulletin
NIST NVD Record: CVE-2026-19490
CISA Known Exploited Vulnerabilities Catalog
Read other CVEs
Implement a continuous find, fix, and verify loop with NodeZero
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
