Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
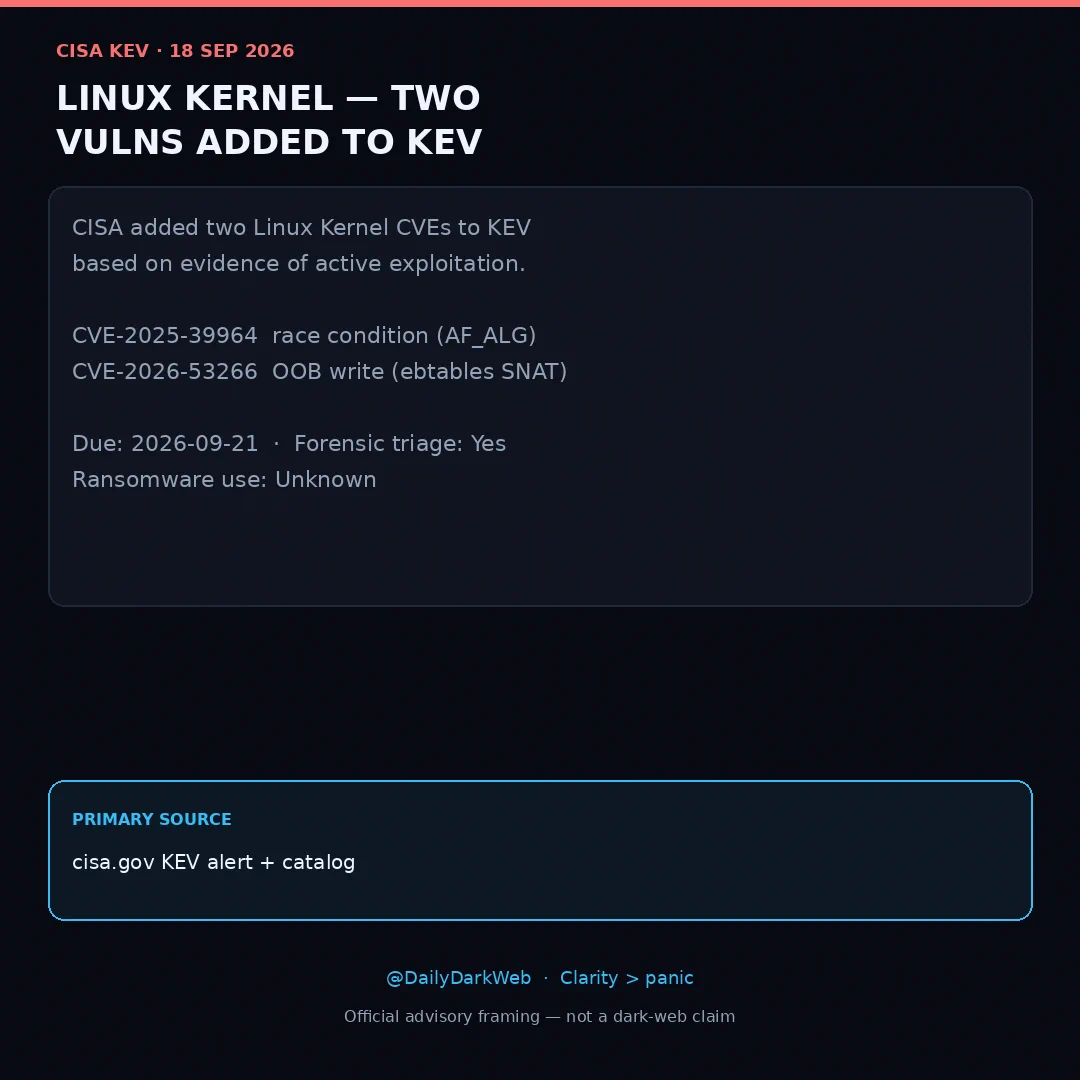
CVE-2026-53266 is a critical vulnerability in the Linux kernel's netfilter bridge ebtables SNAT module, allowing local attackers to modify memory during ARP address rewrites. This flaw can lead to privilege escalation, memory corruption, or denial of service, particularly affecting systems with spec...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added three Linux kernel vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including CVE-2025-39964, which allows local attackers to exploit a race condition in AF_ALG sockets. This vulnerability, along with CVE...
On September 29, 2026, multiple vulnerabilities were disclosed in the Linux kernel, specifically affecting Ubuntu 24.04 and other distributions. These vulnerabilities include CVE-2025-10263, which allows local attackers to bypass memory protections on Arm processors, and CVE-2025-54518, which affect...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has flagged three Linux kernel vulnerabilities as actively exploited, requiring federal agencies to patch them by September 21, 2026. The vulnerabilities, CVE-2025-39682, CVE-2026-53266, and CVE-2025-39964, were added to CISA's Known E...