Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
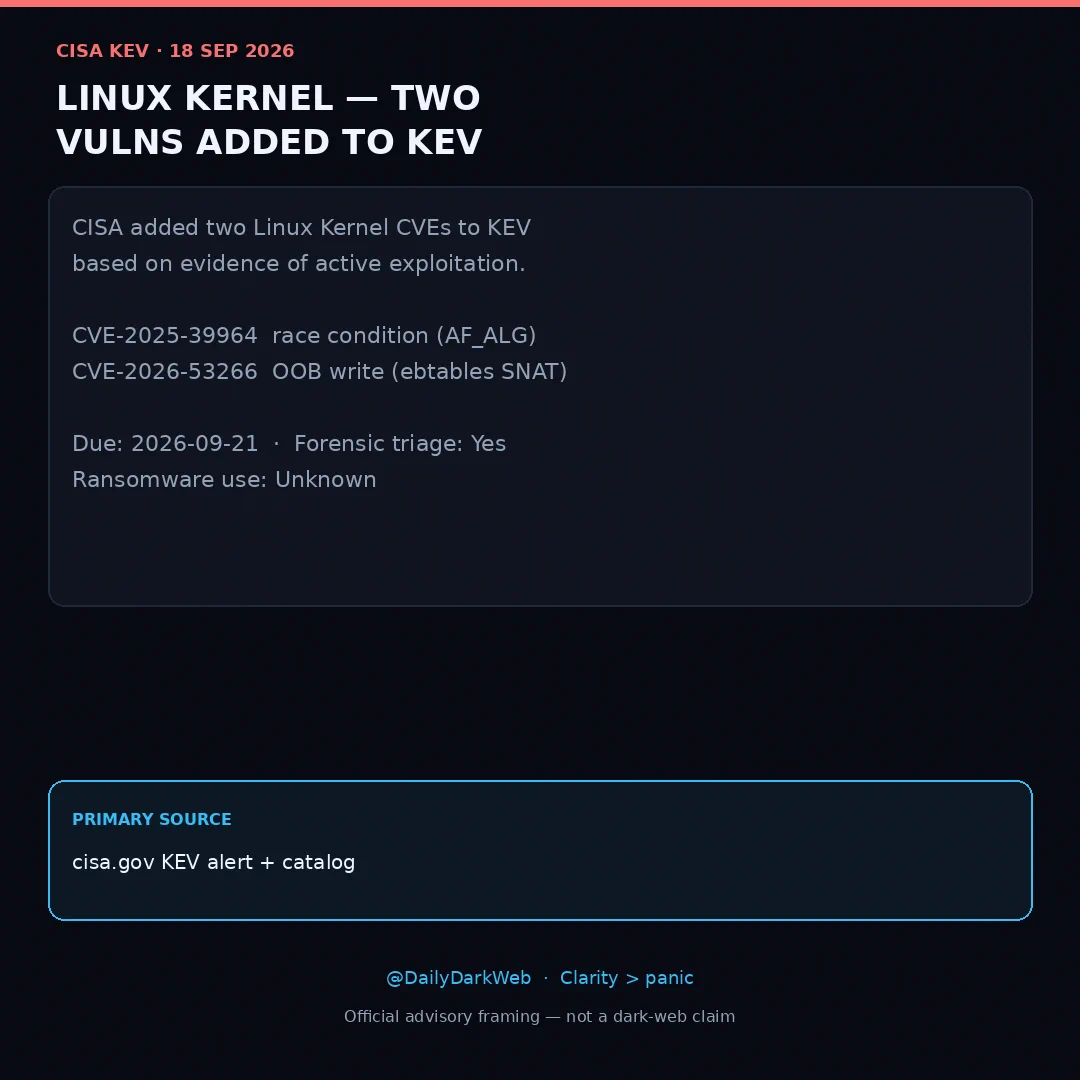
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added three Linux kernel vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including CVE-2025-39964, which allows local attackers to exploit a race condition in AF_ALG sockets. This vulnerability, along with CVE...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has flagged three Linux kernel vulnerabilities as actively exploited, requiring federal agencies to patch them by September 21, 2026. The vulnerabilities, CVE-2025-39682, CVE-2026-53266, and CVE-2025-39964, were added to CISA's Known E...
Red Hat has released two security advisories for vulnerabilities in kernel packages for Red Hat Enterprise Linux for NVIDIA. The first advisory, RHSA-2026:73187, addresses multiple critical vulnerabilities, including CVE-2026-74480 and CVE-2026-74581, both rated with a CVSS score of 9.8. These vulne...
Several security issues were identified in the Linux kernel, potentially allowing attackers to compromise systems. The vulnerabilities affect various subsystems, including the Cryptographic API, ACPI drivers, and Netfilter. Updates have been issued to address these flaws.