Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
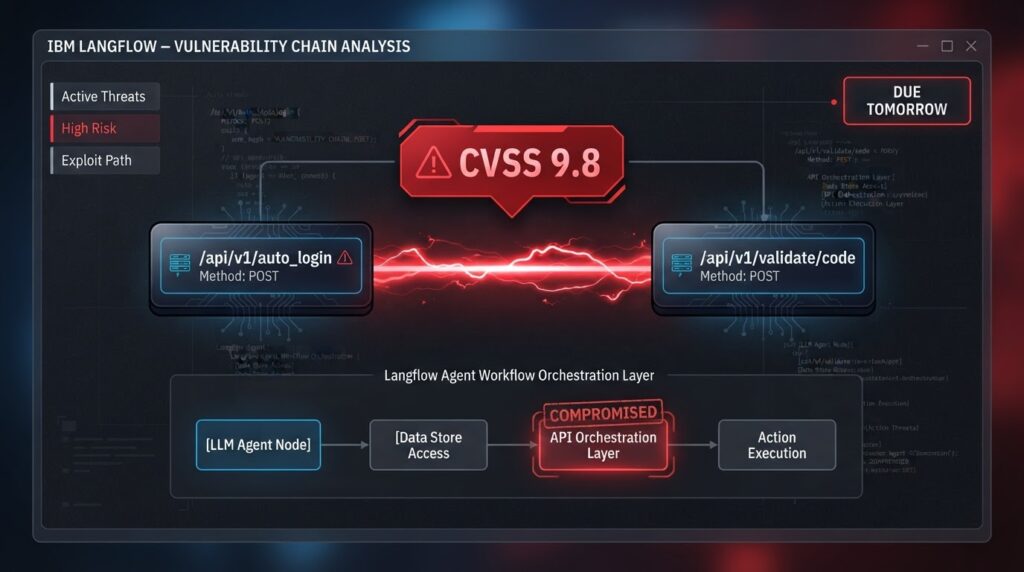
IBM Langflow OSS is facing a critical remote code execution (RCE) vulnerability, tracked as CVE-2026-9198, which allows unauthenticated attackers to execute arbitrary code on default deployments. The vulnerability combines an authentication bypass with a code execution flaw, enabling attackers to ga...
Hackers are actively exploiting a critical vulnerability in Langflow, tracked as CVE-2026-0768, which allows unauthenticated remote code execution. The flaw affects all versions up to 1.4.2 of the AI-focused low-code platform Langflow, enabling attackers to execute arbitrary Python code with root pr...
In July 2026, several critical vulnerabilities were exploited, impacting SonicWall SMA1000 appliances and SharePoint servers. Two zero-day vulnerabilities, CVE-2026-15409 and CVE-2026-15410, were discovered in SonicWall appliances, allowing unauthenticated attackers to execute commands as root. Addi...
A moderate-scored IDOR vulnerability (CVE-2026-55255) in Langflow has been actively exploited since June 25, 2026, allowing attackers to access and execute flows belonging to other users. This exploit leverages a natural-language prompt to extract sensitive credentials, highlighting a significant ov...