 Heise.De
Critical CVE-2026-0768 Exploited in Langflow Attacks
Article Content

- •CVE-2026-0768 allows unauthenticated remote code execution in Langflow.
- •Over 350 exploitation attempts have been reported, primarily targeting UK systems.
- •A patch has been available since January 2026, but many systems remain vulnerable.
Hackers are actively exploiting a critical vulnerability in Langflow, tracked as CVE-2026-0768, which allows unauthenticated remote code execution. The flaw affects all versions up to 1.4.2 of the AI-focused low-code platform Langflow, enabling attackers to execute arbitrary Python code with root privileges. Security researchers from VulnCheck reported over 350 attempted attacks, primarily targeting UK-based systems. The vulnerability was disclosed in January 2026, and a patch has been available since then, but many systems remain unpatched. Attackers are stealing admin credentials and conducting reconnaissance on environment variables. The current exploitation is confirmed to be ongoing, with significant activity observed in recent days. Organizations are urged to apply the available fixes immediately to mitigate risks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (21)
Following this threat?
Track Langflow and CVE-2026-0768 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
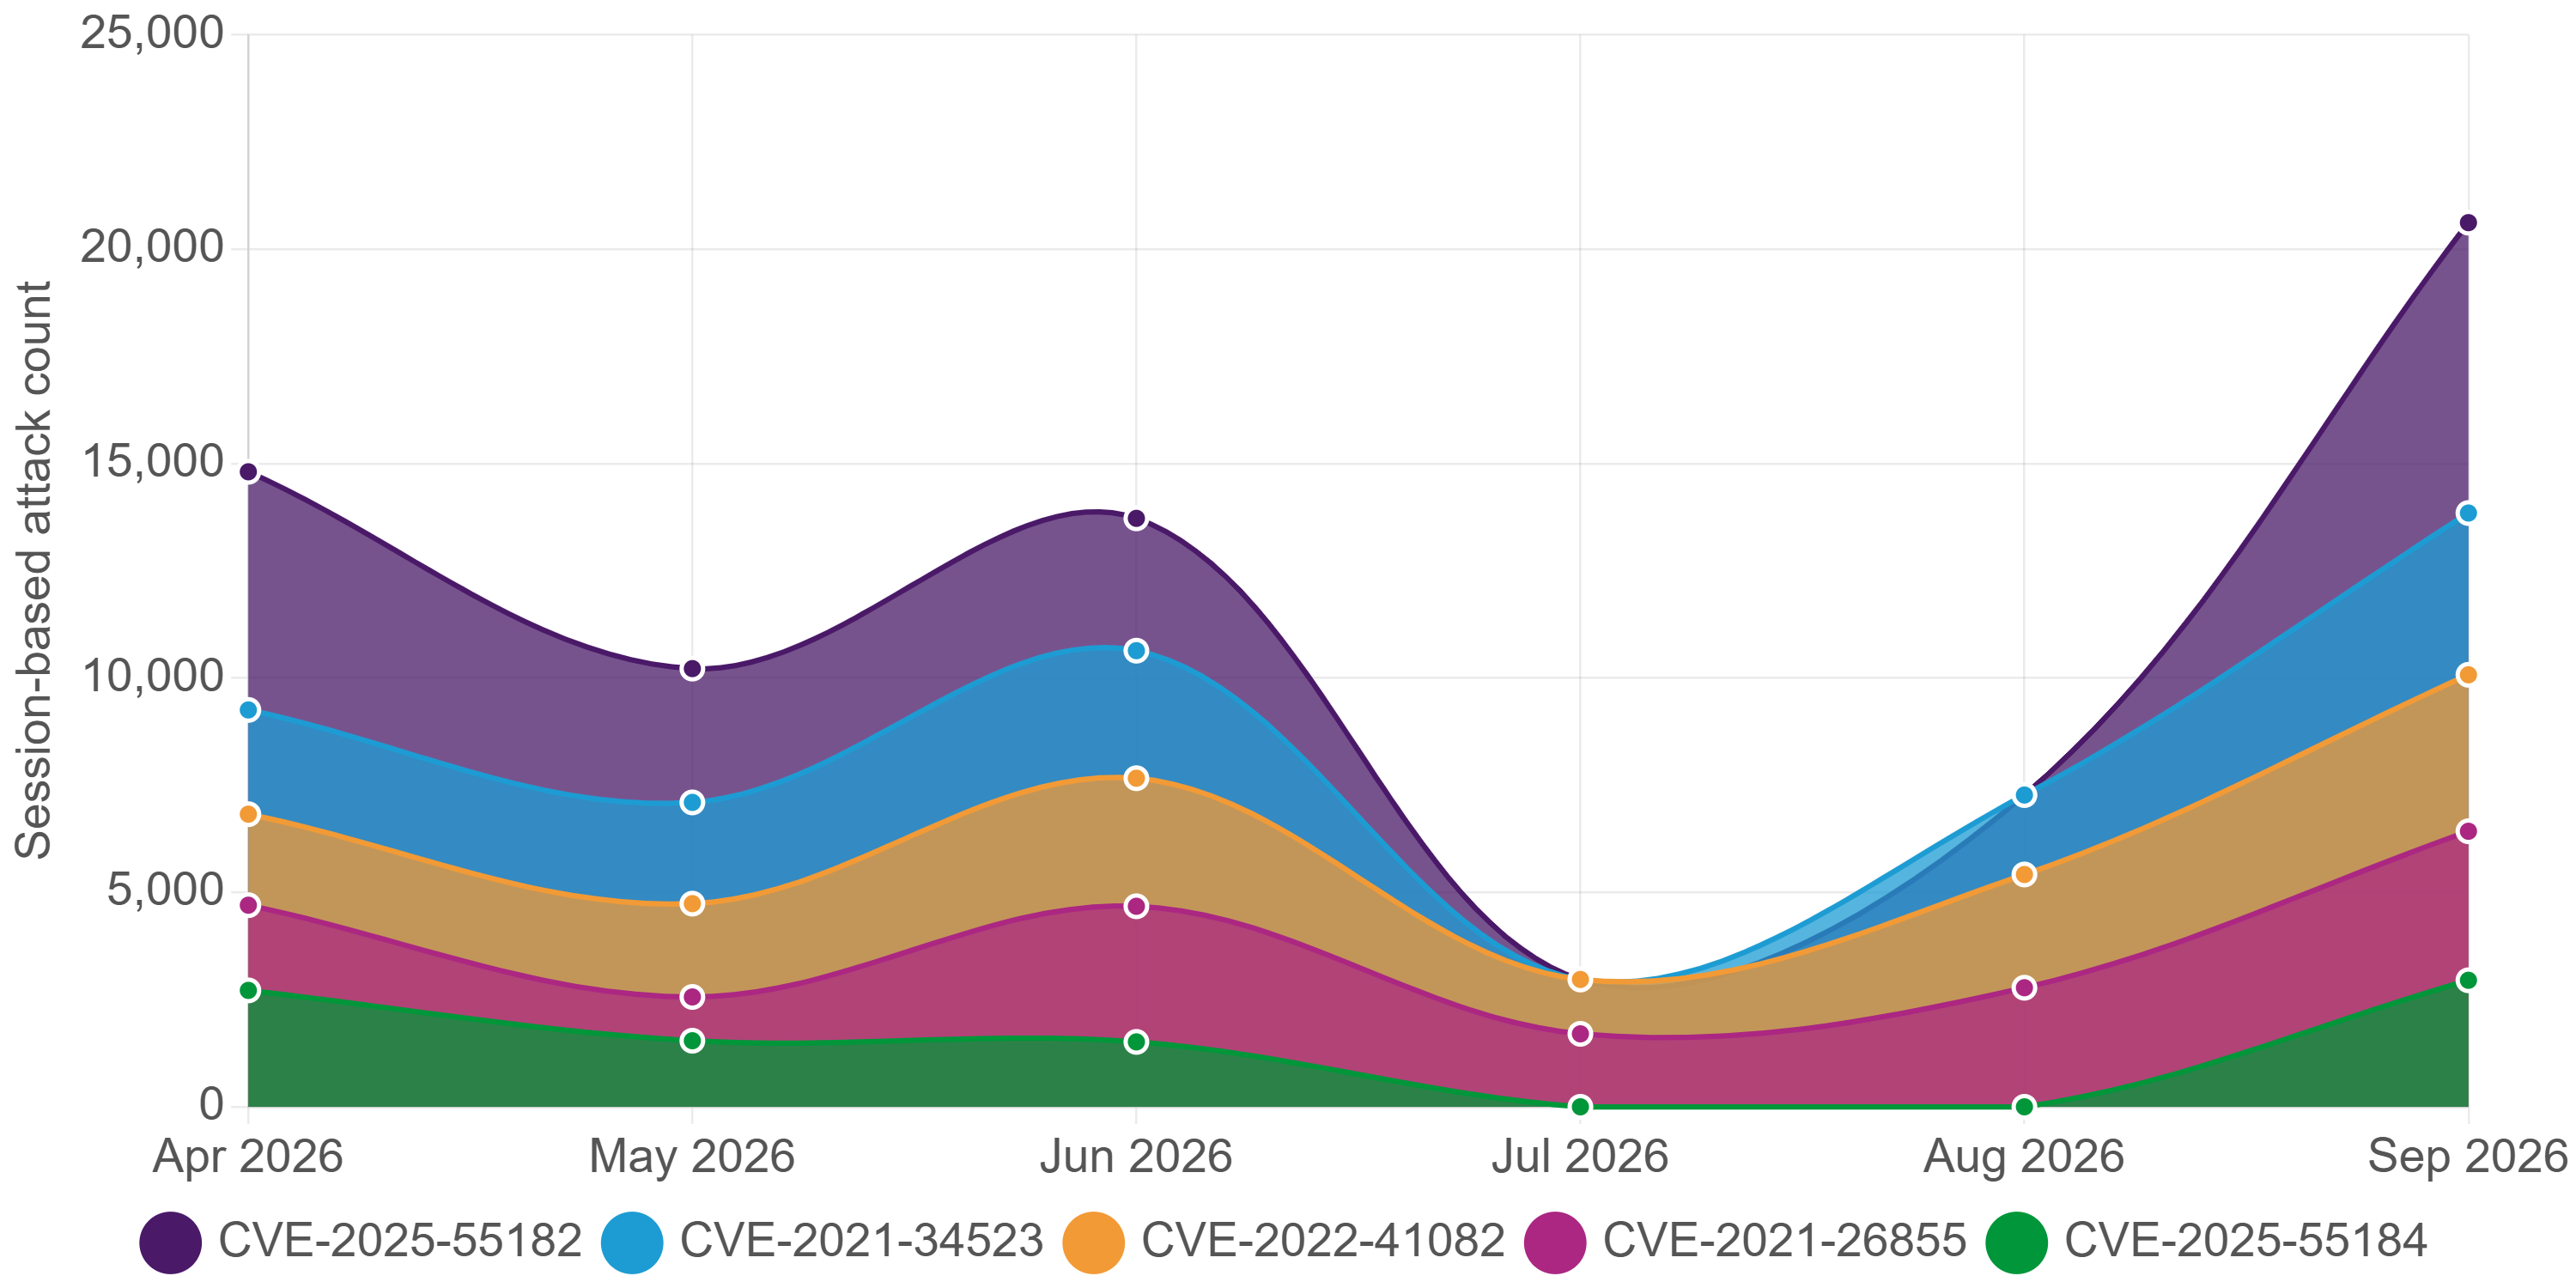 Langflow AI Platform Targeted by RCE Exploitation In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. The vulnerability…
 Langflow CVE-2026-0768 Exploited in Credential Theft Campaign CVE-2026-0768, an unauthenticated remote code execution vulnerability in Langflow, is being, allowing attackers to execute arbitrary code with root privileges. As of October 6, 2026, VulnCheck reported over 360 exploitation attempts, primarily targeting environment variables such as AWS secrets and OpenAI API keys.…