Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
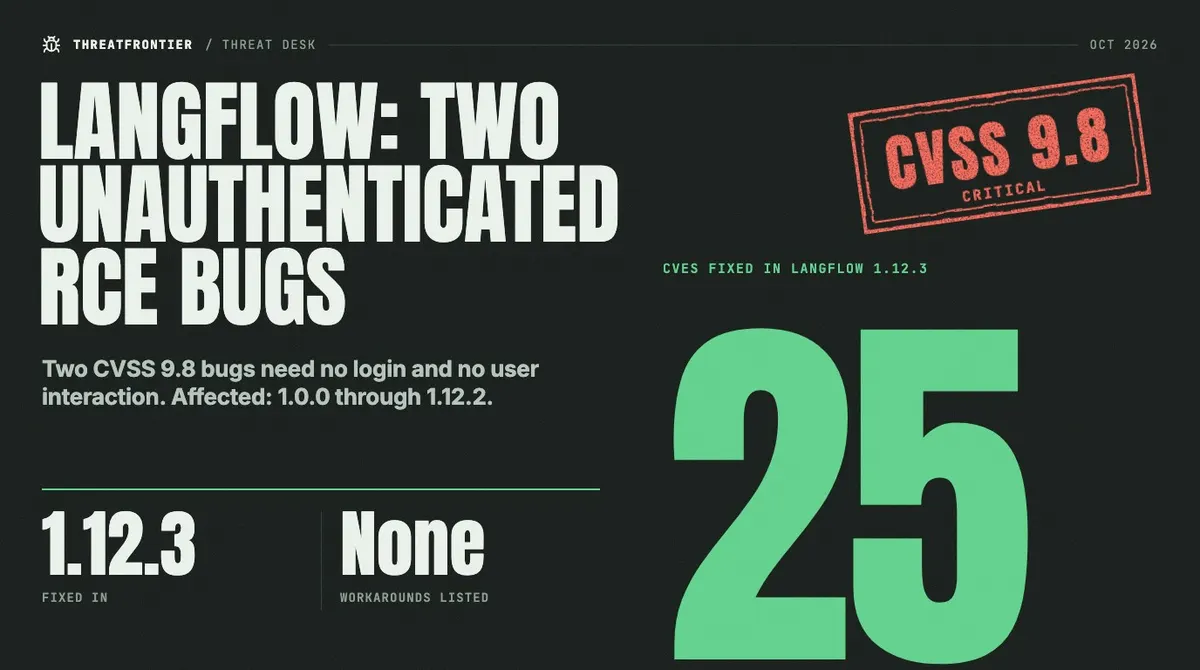
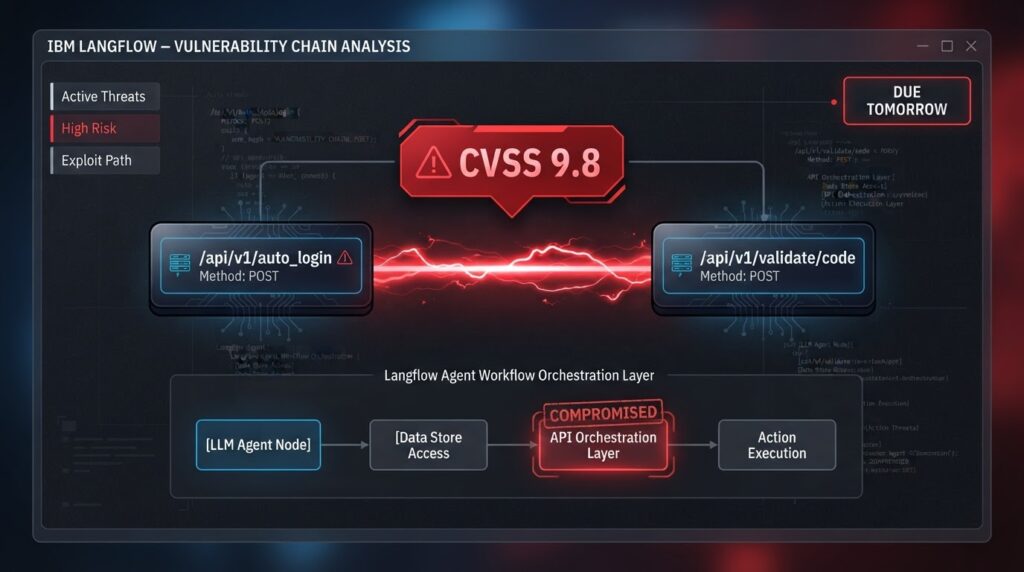
IBM Langflow OSS is facing a critical remote code execution (RCE) vulnerability, tracked as CVE-2026-9198, which allows unauthenticated attackers to execute arbitrary code on default deployments. The vulnerability combines an authentication bypass with a code execution flaw, enabling attackers to ga...
A critical zero-day vulnerability (CVE-2026-35273) in Oracle PeopleSoft has been exploited by the ShinyHunters group, leading to breaches of over 100 organizations, primarily in the education sector. The vulnerability allows unauthenticated remote code execution, enabling attackers to compromise sys...
Hackers are actively exploiting a critical vulnerability in Langflow, tracked as CVE-2026-0768, which allows unauthenticated remote code execution. The flaw affects all versions up to 1.4.2 of the AI-focused low-code platform Langflow, enabling attackers to execute arbitrary Python code with root pr...
Threat actors are exploiting CVE-2026-33017, a critical unauthenticated remote code execution vulnerability in Langflow, to compromise exposed AI application servers. This exploitation allows attackers to deploy a customized Monero (XMR) cryptominer silently. The vulnerability was published on March...