Article Content

- •CVE-2026-0768 allows unauthenticated RCE on Langflow, with a CVSS score of 9.8.
- •Over 405 exploitation attempts were recorded from 55 distinct IPs in September 2026.
- •Attackers are targeting sensitive data, including cloud credentials and API keys.
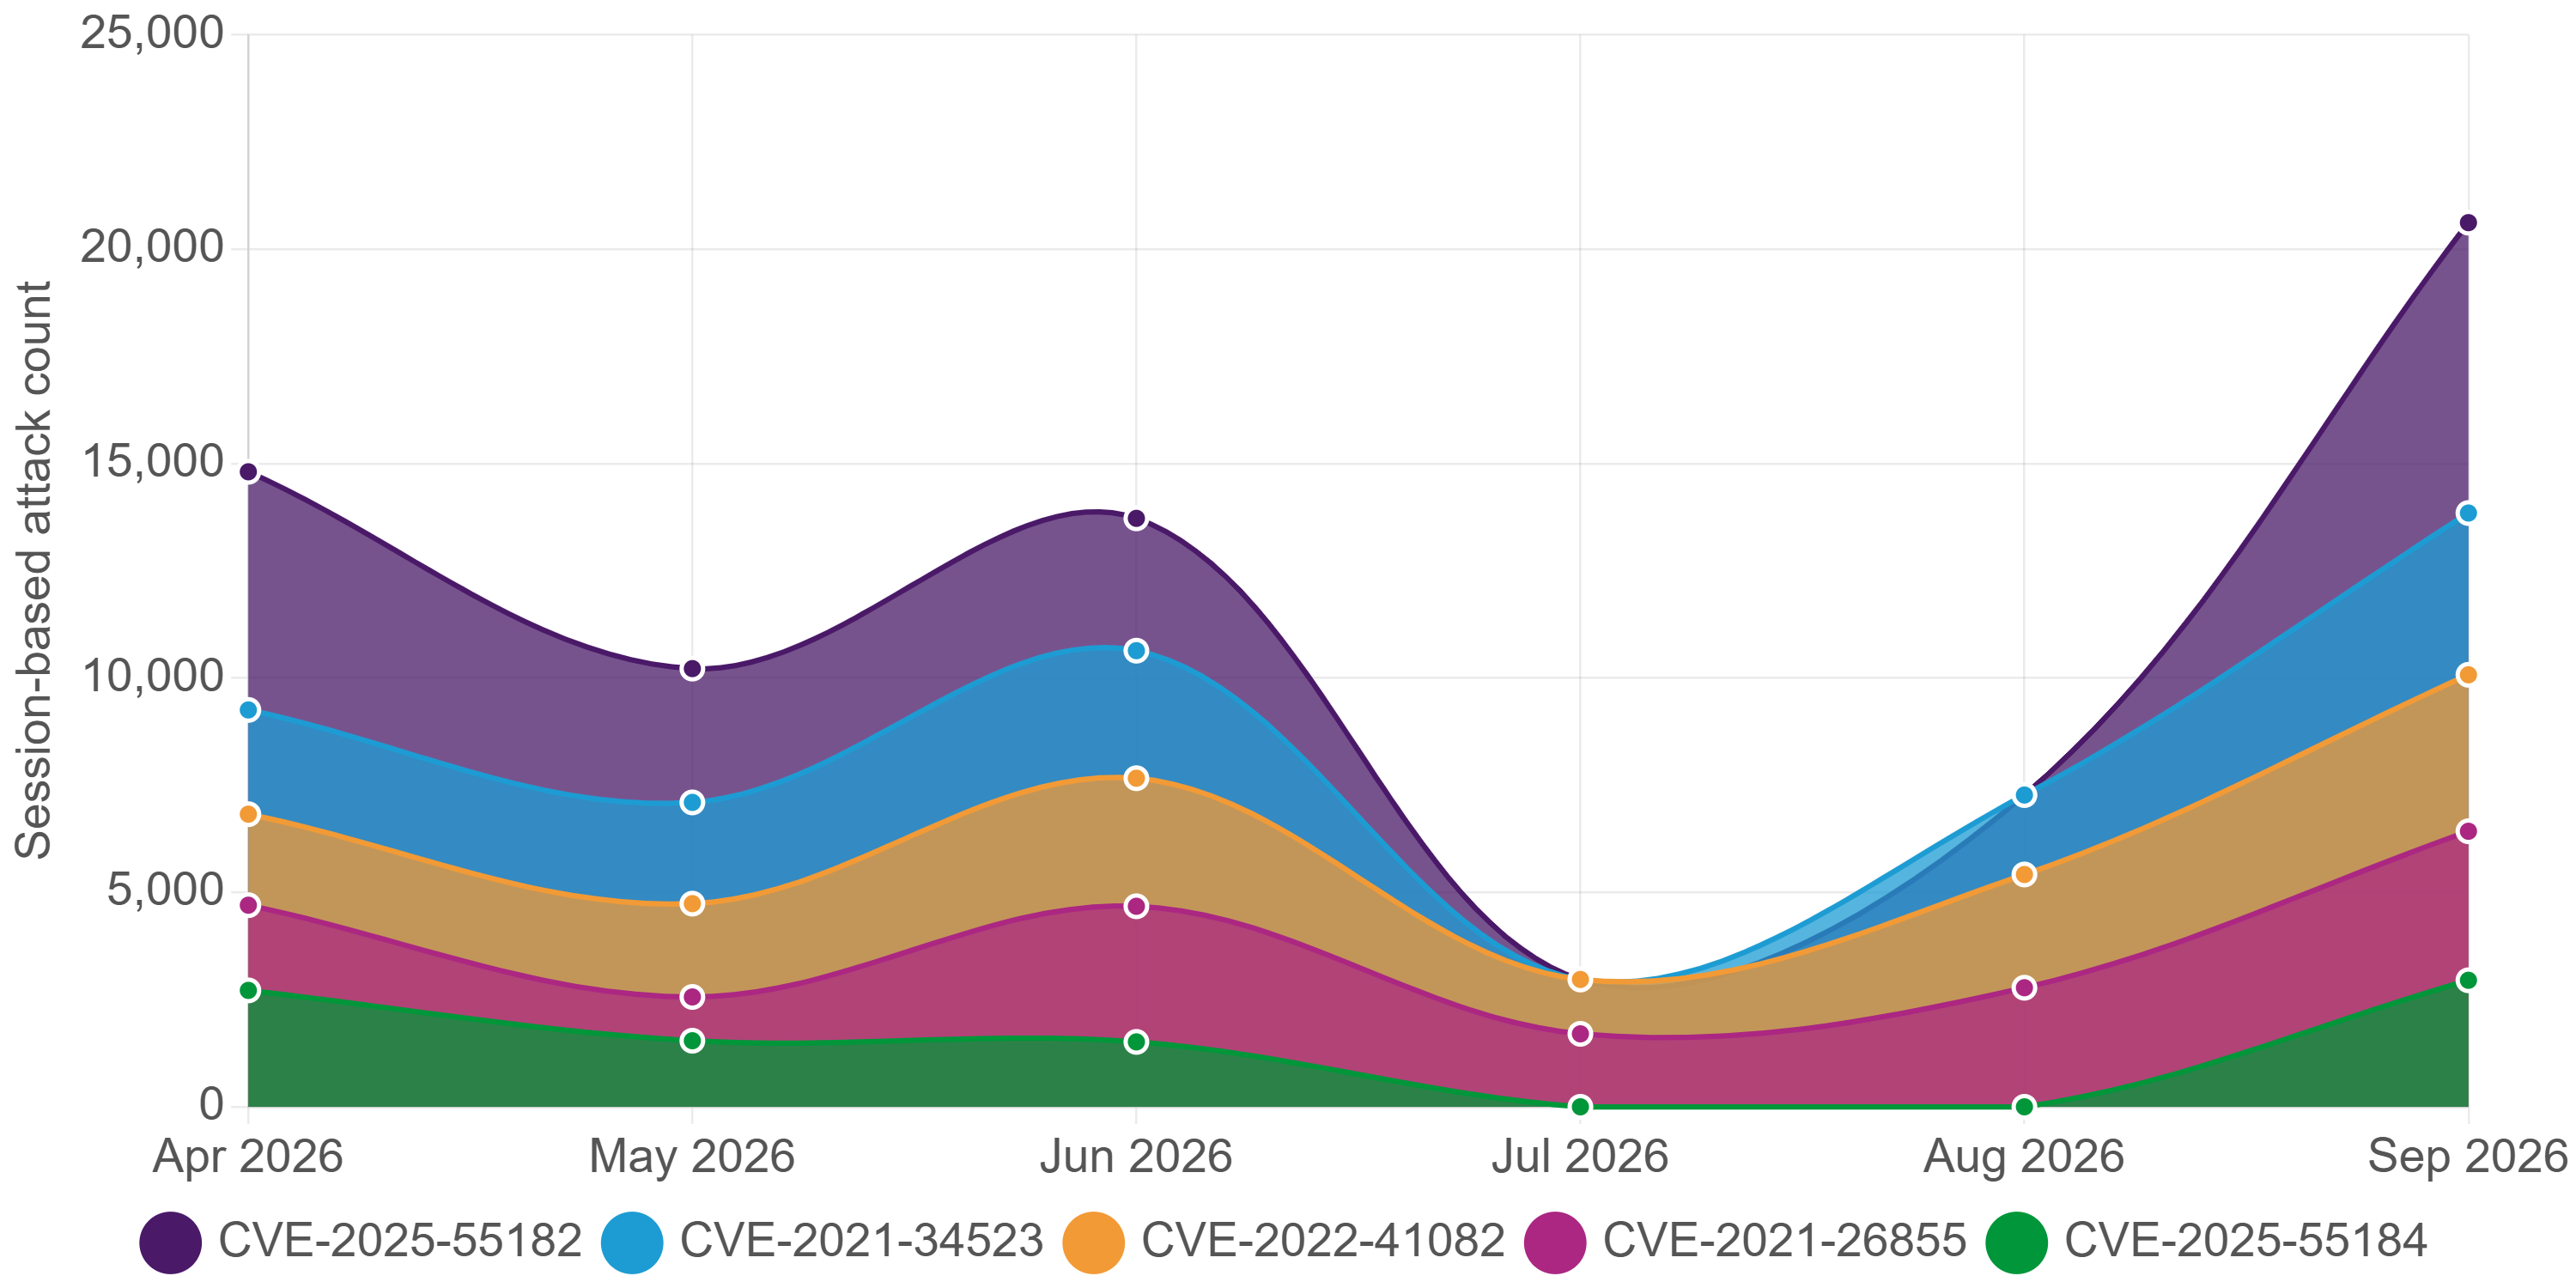
In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. The vulnerability allows attackers to execute arbitrary Python code via a validation endpoint without authentication. Exploitation attempts began in late August, with a peak of 162 events recorded on September 26. Attackers are reportedly harvesting sensitive data such as cloud credentials and API keys. The vulnerability was disclosed on January 23, 2026, and has a CVSS score of 9.8, marking it as. As of now, exploitation in the wild is confirmed, raising urgent concerns for organizations using Langflow.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track AWS and CVE-2016-4800 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is CVE-2026-0768?
How can I protect my organization?
What data is at risk?
Continue Reading
 Mass Scanning Campaign Targets Exposed Vite Servers for Cloud Credentials In August 2026, a mass-scanning campaign targeted internet-exposed Vite development servers to steal sensitive cloud credentials and configuration files from AWS and Azure. The attackers exploited CVE-2026-39364, a high-severity vulnerability allowing unauthenticated access to restricted files via manipulated query…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…