Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
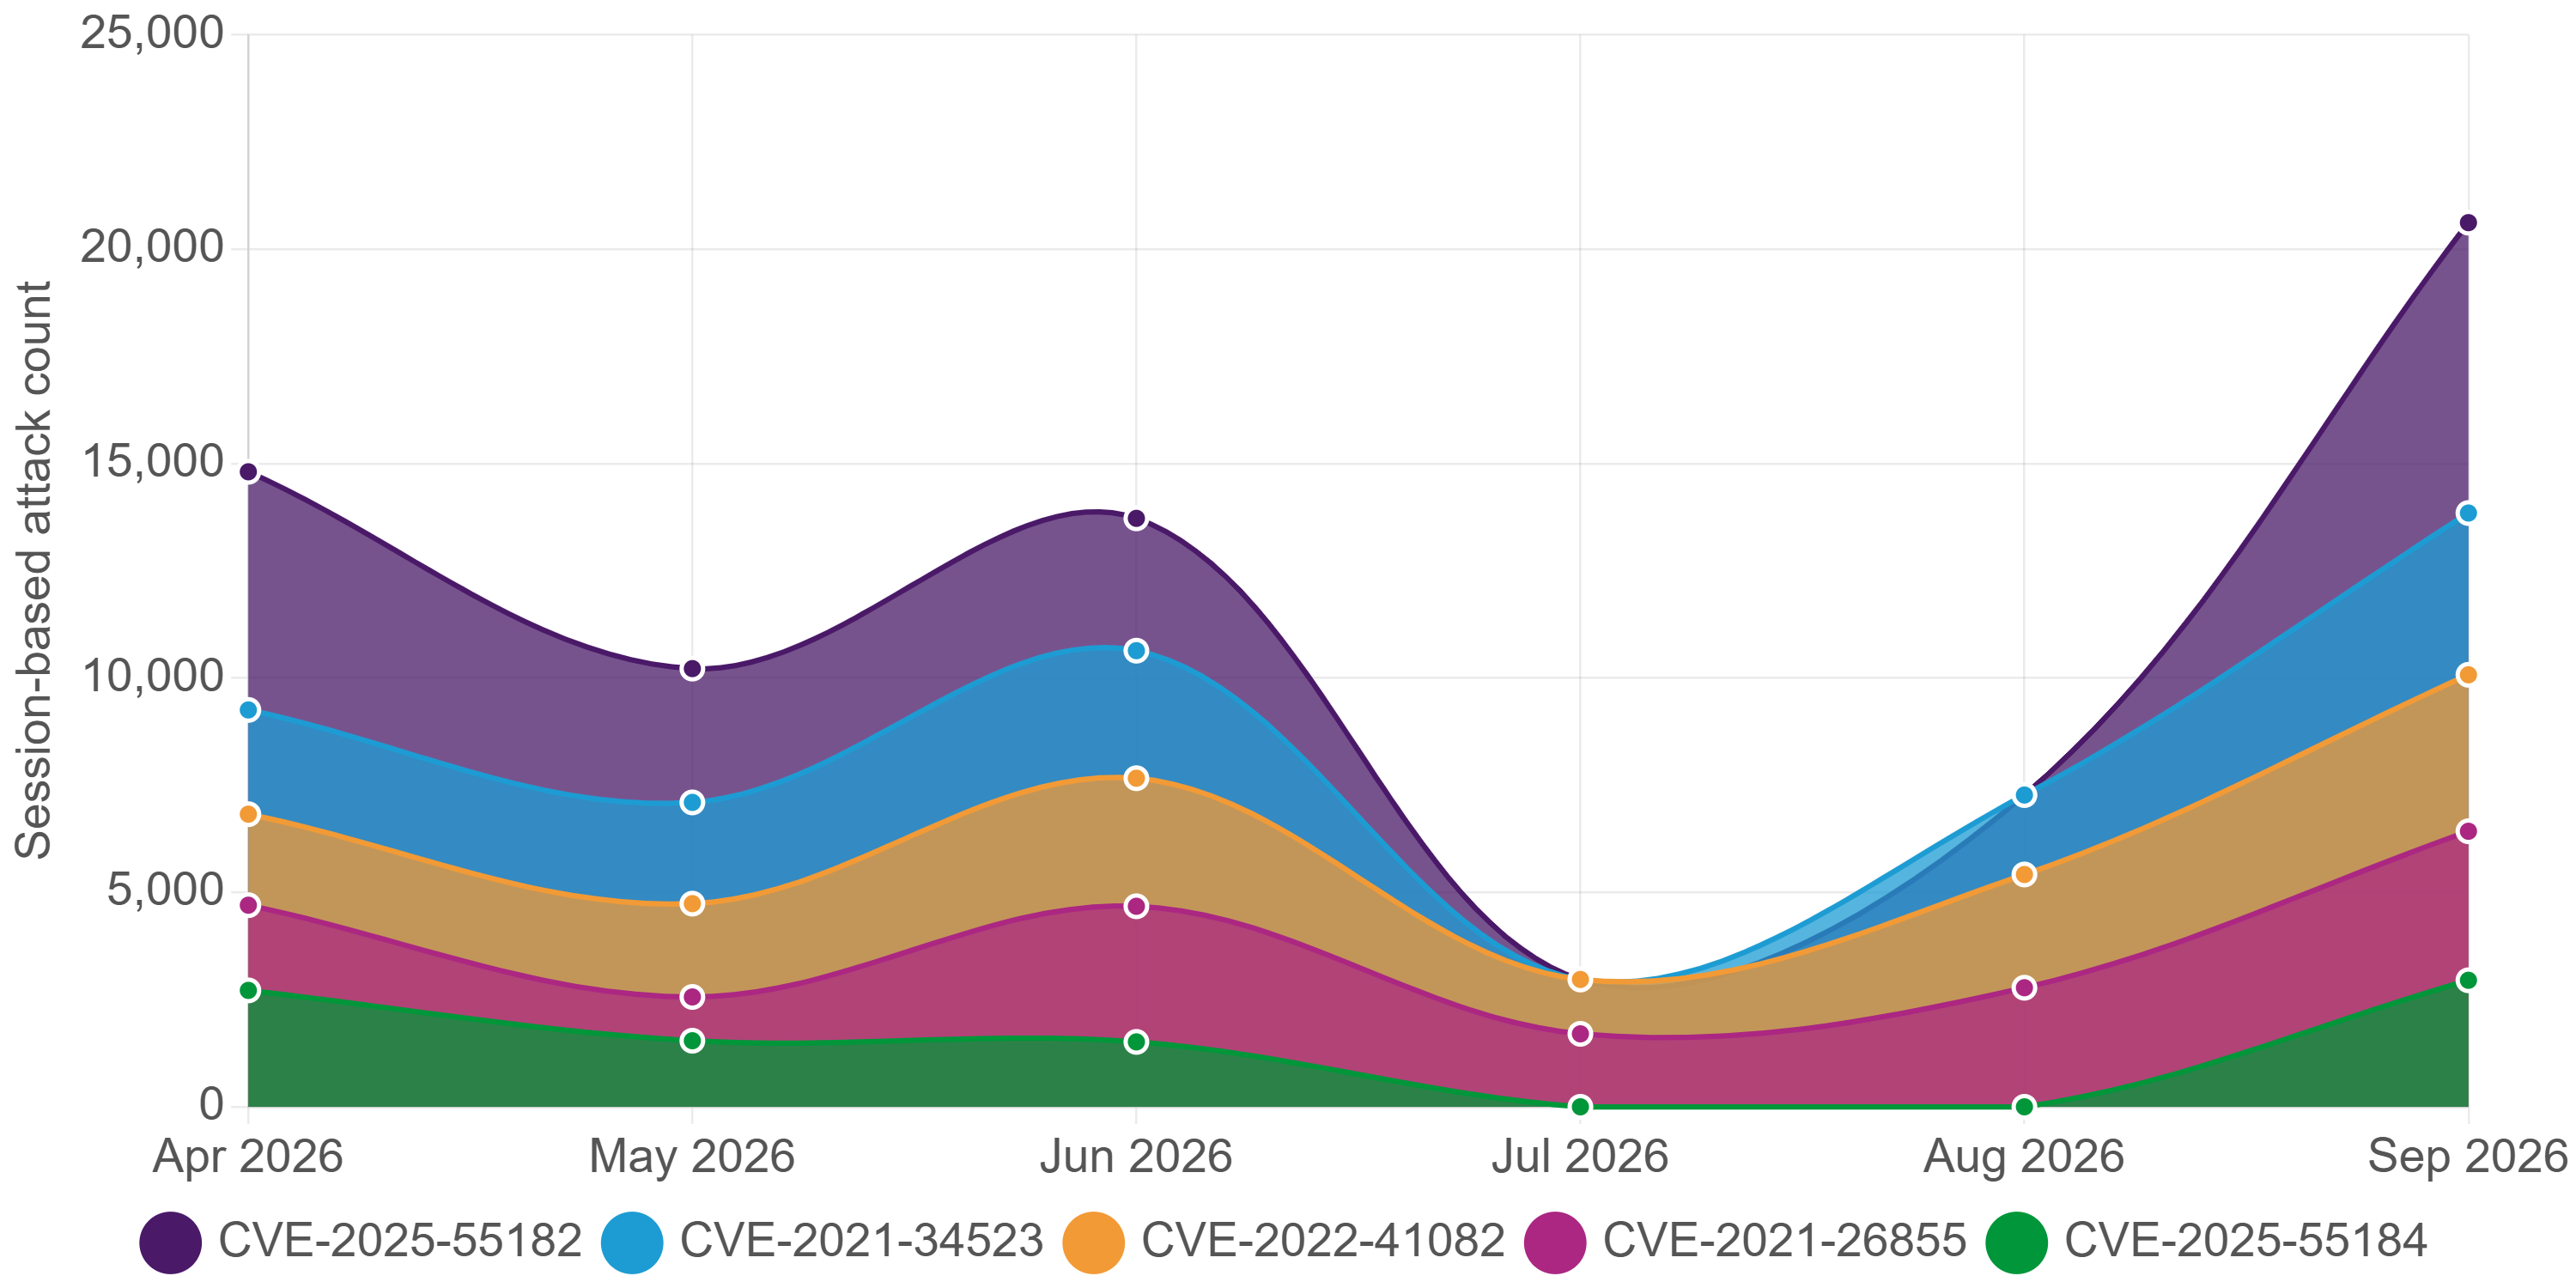
The RondoDox botnet is exploiting the React2Shell vulnerability (CVE-2025-55182) to infect vulnerable .js servers with malware and cryptominers. This ongoing campaign has been active for nine months, primarily targeting IoT devices and web applications, as reported by CloudSEK researchers.
A critical vulnerability in the nginx-ui web server management tool, tracked as CVE-2026-33032, has been actively exploited since March 2026. This flaw allows attackers to bypass authentication on the /mcp_message endpoint, enabling full control over NGINX servers through a single unauthenticated AP...
AWS has highlighted the risks associated with unmonitored outbound traffic in cloud environments, particularly in light of the CVE-2025-55182 vulnerability affecting React Server Components. This vulnerability allows for pre-authentication remote code execution, which can lead to unauthorized data e...
A coordinated supply chain attack has been identified, targeting vulnerability researchers and penetration testers through malicious proof-of-concept (PoC) repositories on GitHub. The malware, named ChocoPoC, is a Python-based remote access trojan (RAT) that stealthily exfiltrates sensitive data. At...