Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
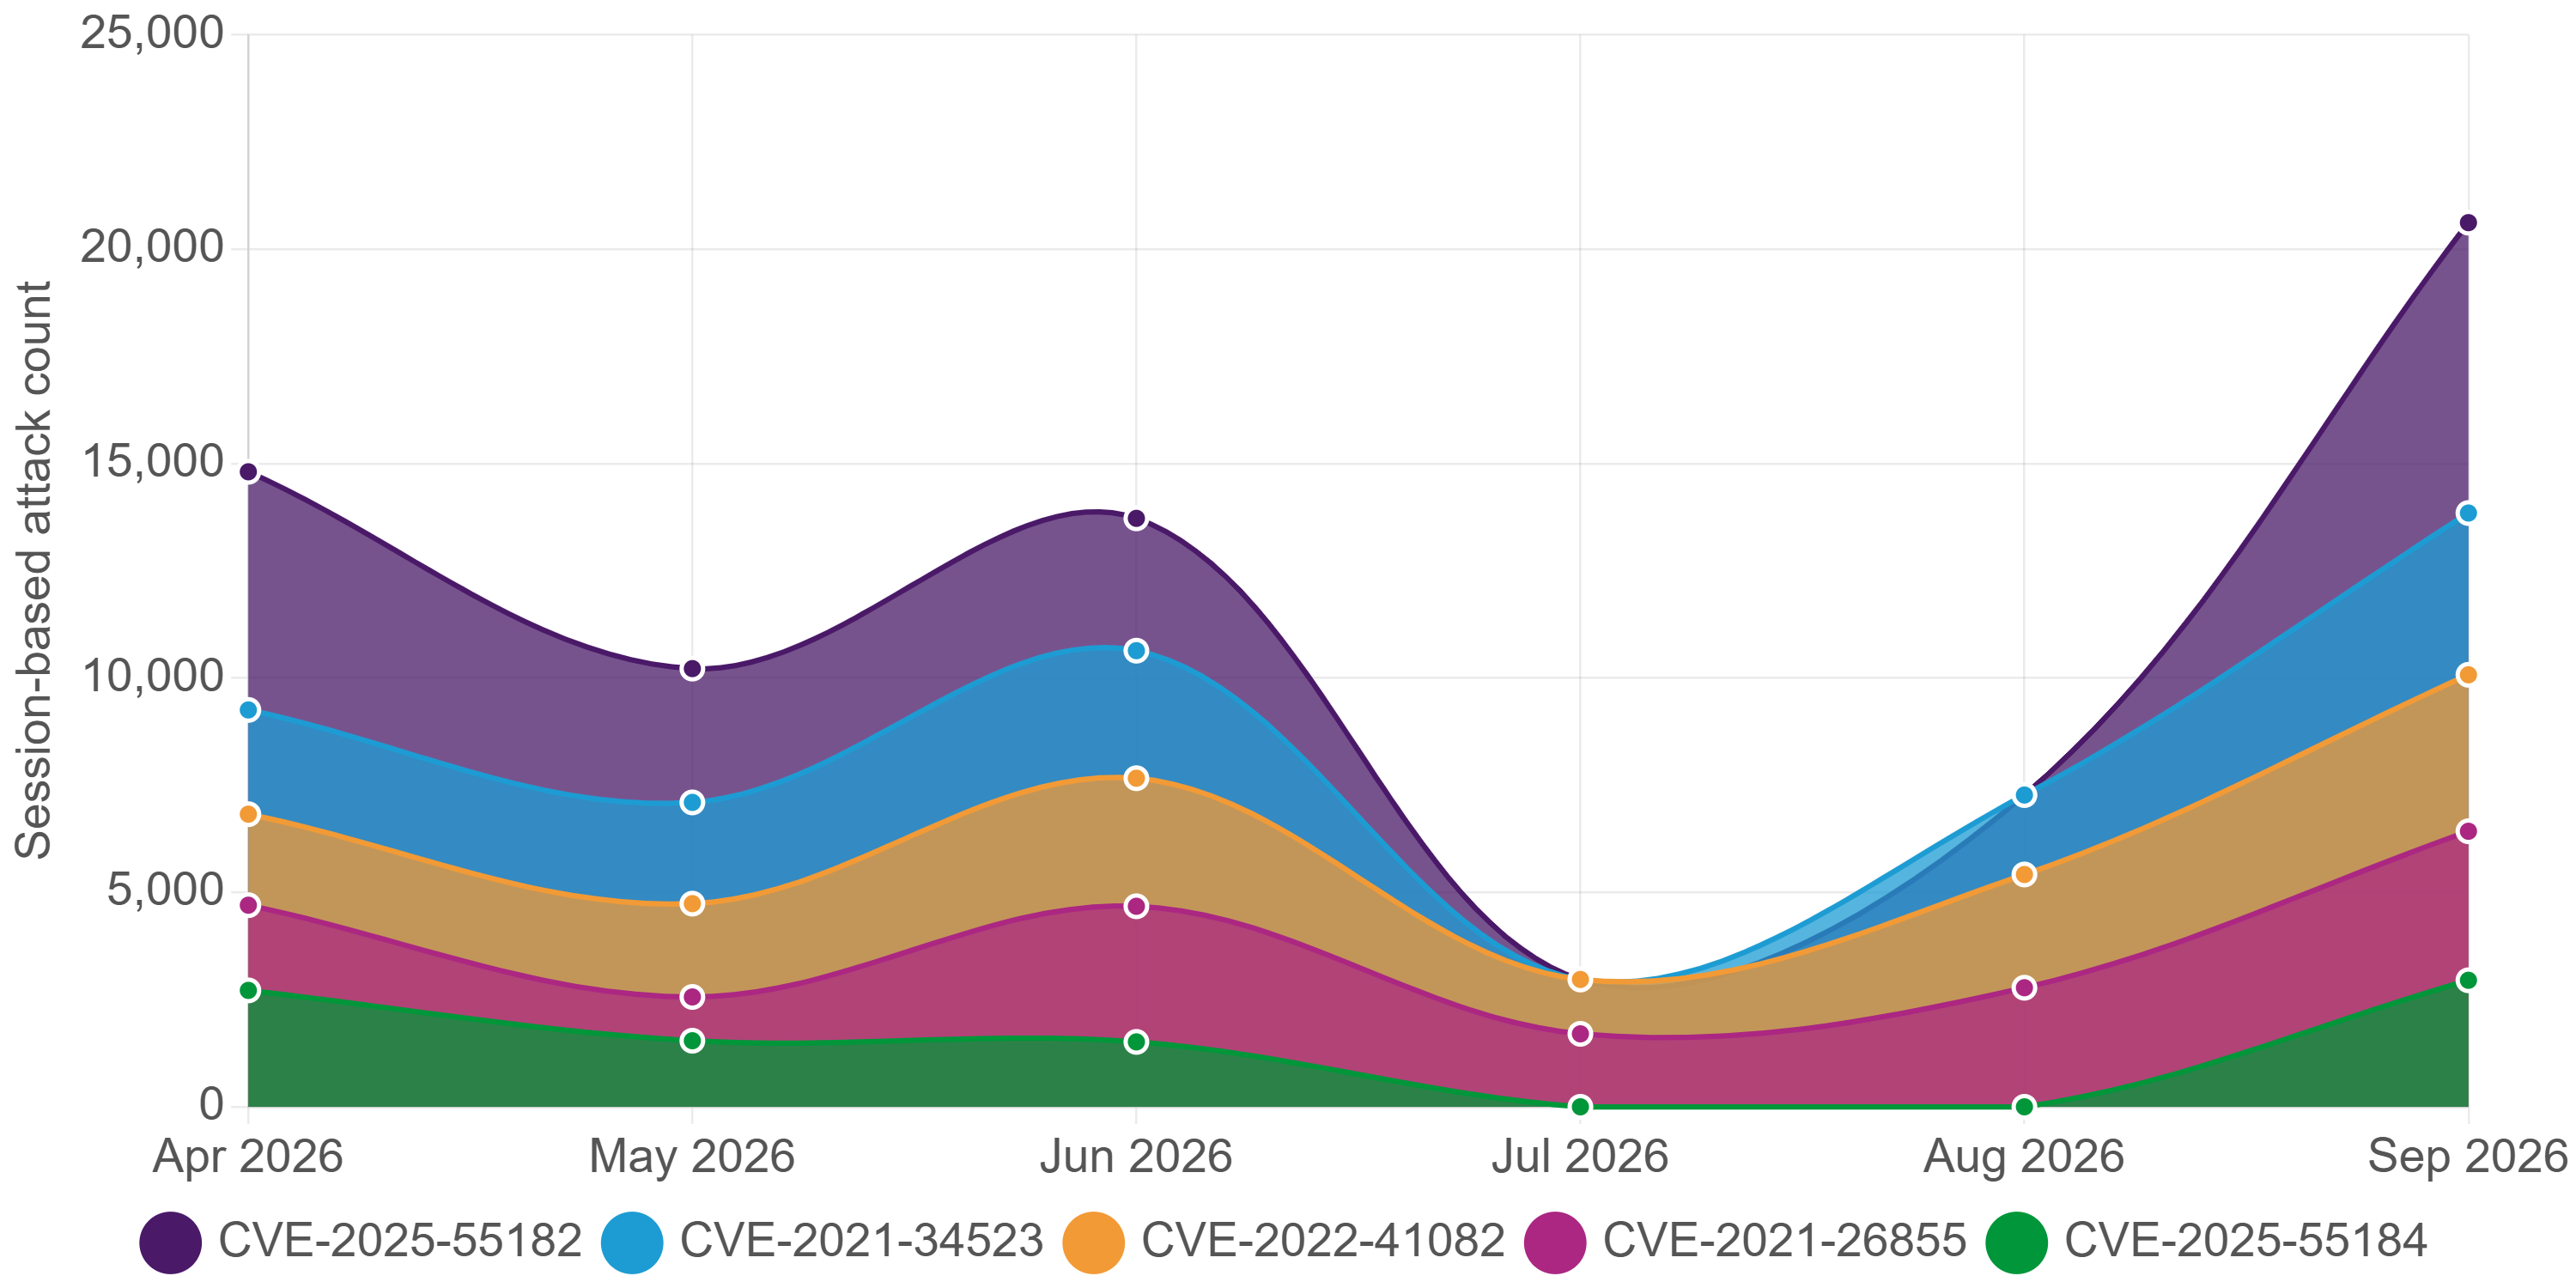
A series of vulnerabilities, including CVE-2025-49144, CVE-2025-31702, and CVE-2026-46333, have been identified, affecting systems like Notepad++ and FortiWeb devices. These vulnerabilities allow for local privilege escalation, SQL injection, and remote code execution. Attackers exploit these flaws...
In August 2026, a mass-scanning campaign targeted internet-exposed Vite development servers to steal sensitive cloud credentials and configuration files from AWS and Azure. The attackers exploited CVE-2026-39364, a high-severity vulnerability allowing unauthenticated access to restricted files via m...
In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. T...
Operation PCPcat has compromised 59,128 Next.js and React servers in under 48 hours, exploiting critical vulnerabilities CVE-2025-29927 and CVE-2025-66478. The attackers utilized prototype pollution in JSON payloads to achieve a 64.6% success rate across 91,505 scanned targets, deploying PCPCat scan...