 Sophos
Vect and TeamPCP Form Alliance for Ransomware Operations
Article Content

- •Vect and TeamPCP have formed a partnership to enhance ransomware operations.
- •TeamPCP's credential theft has compromised over 500,000 login credentials from various organizations.
- •The collaboration signifies a shift towards industrialized ransomware tactics in the cyber threat landscape.
In late March 2026, the Vect ransomware group partnered with TeamPCP, a credential theft specialist, to enhance their cybercriminal operations. This collaboration aims to leverage TeamPCP's extensive credential harvesting capabilities alongside Vect's ransomware deployment infrastructure, targeting organizations through supply chain attacks. TeamPCP gained notoriety for exploiting the React2Shell vulnerability (CVE-2025-55182) and has been linked to significant breaches, including a compromise of Aqua Security's Trivy scanner, affecting over 10,000 CI/CD workflows and stealing more than 500,000 login credentials. The partnership marks a notable shift in the ransomware landscape, as it allows for a more industrialized approach to cybercrime, increasing the risk for organizations with compromised credentials. The FBI has issued warnings regarding TeamPCP's activities, highlighting their history of large-scale software supply chain compromises.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (8)
Following this threat?
Track Vect, TeamPCP and CanisterWorm in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
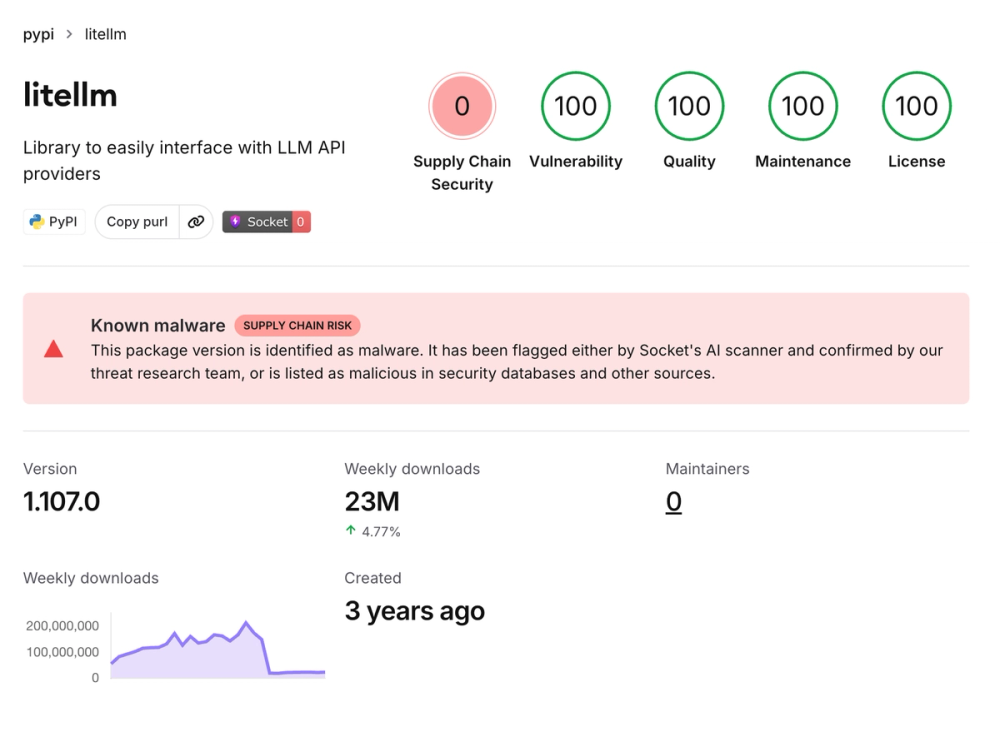 LiteLLM 1.107.0 Compromised: Credential Stealer and RAT Distributed via PyPI On October 21, 2026, the LiteLLM Python package version 1.107.0 was compromised in a supply chain attack, distributing malware that includes a credential stealer and a remote access trojan (RAT). The malicious code was injected into the package's wheels on PyPI and Docker images, affecting all platforms. The attack…
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…