Vulnerability Overview
Exploitation Activity
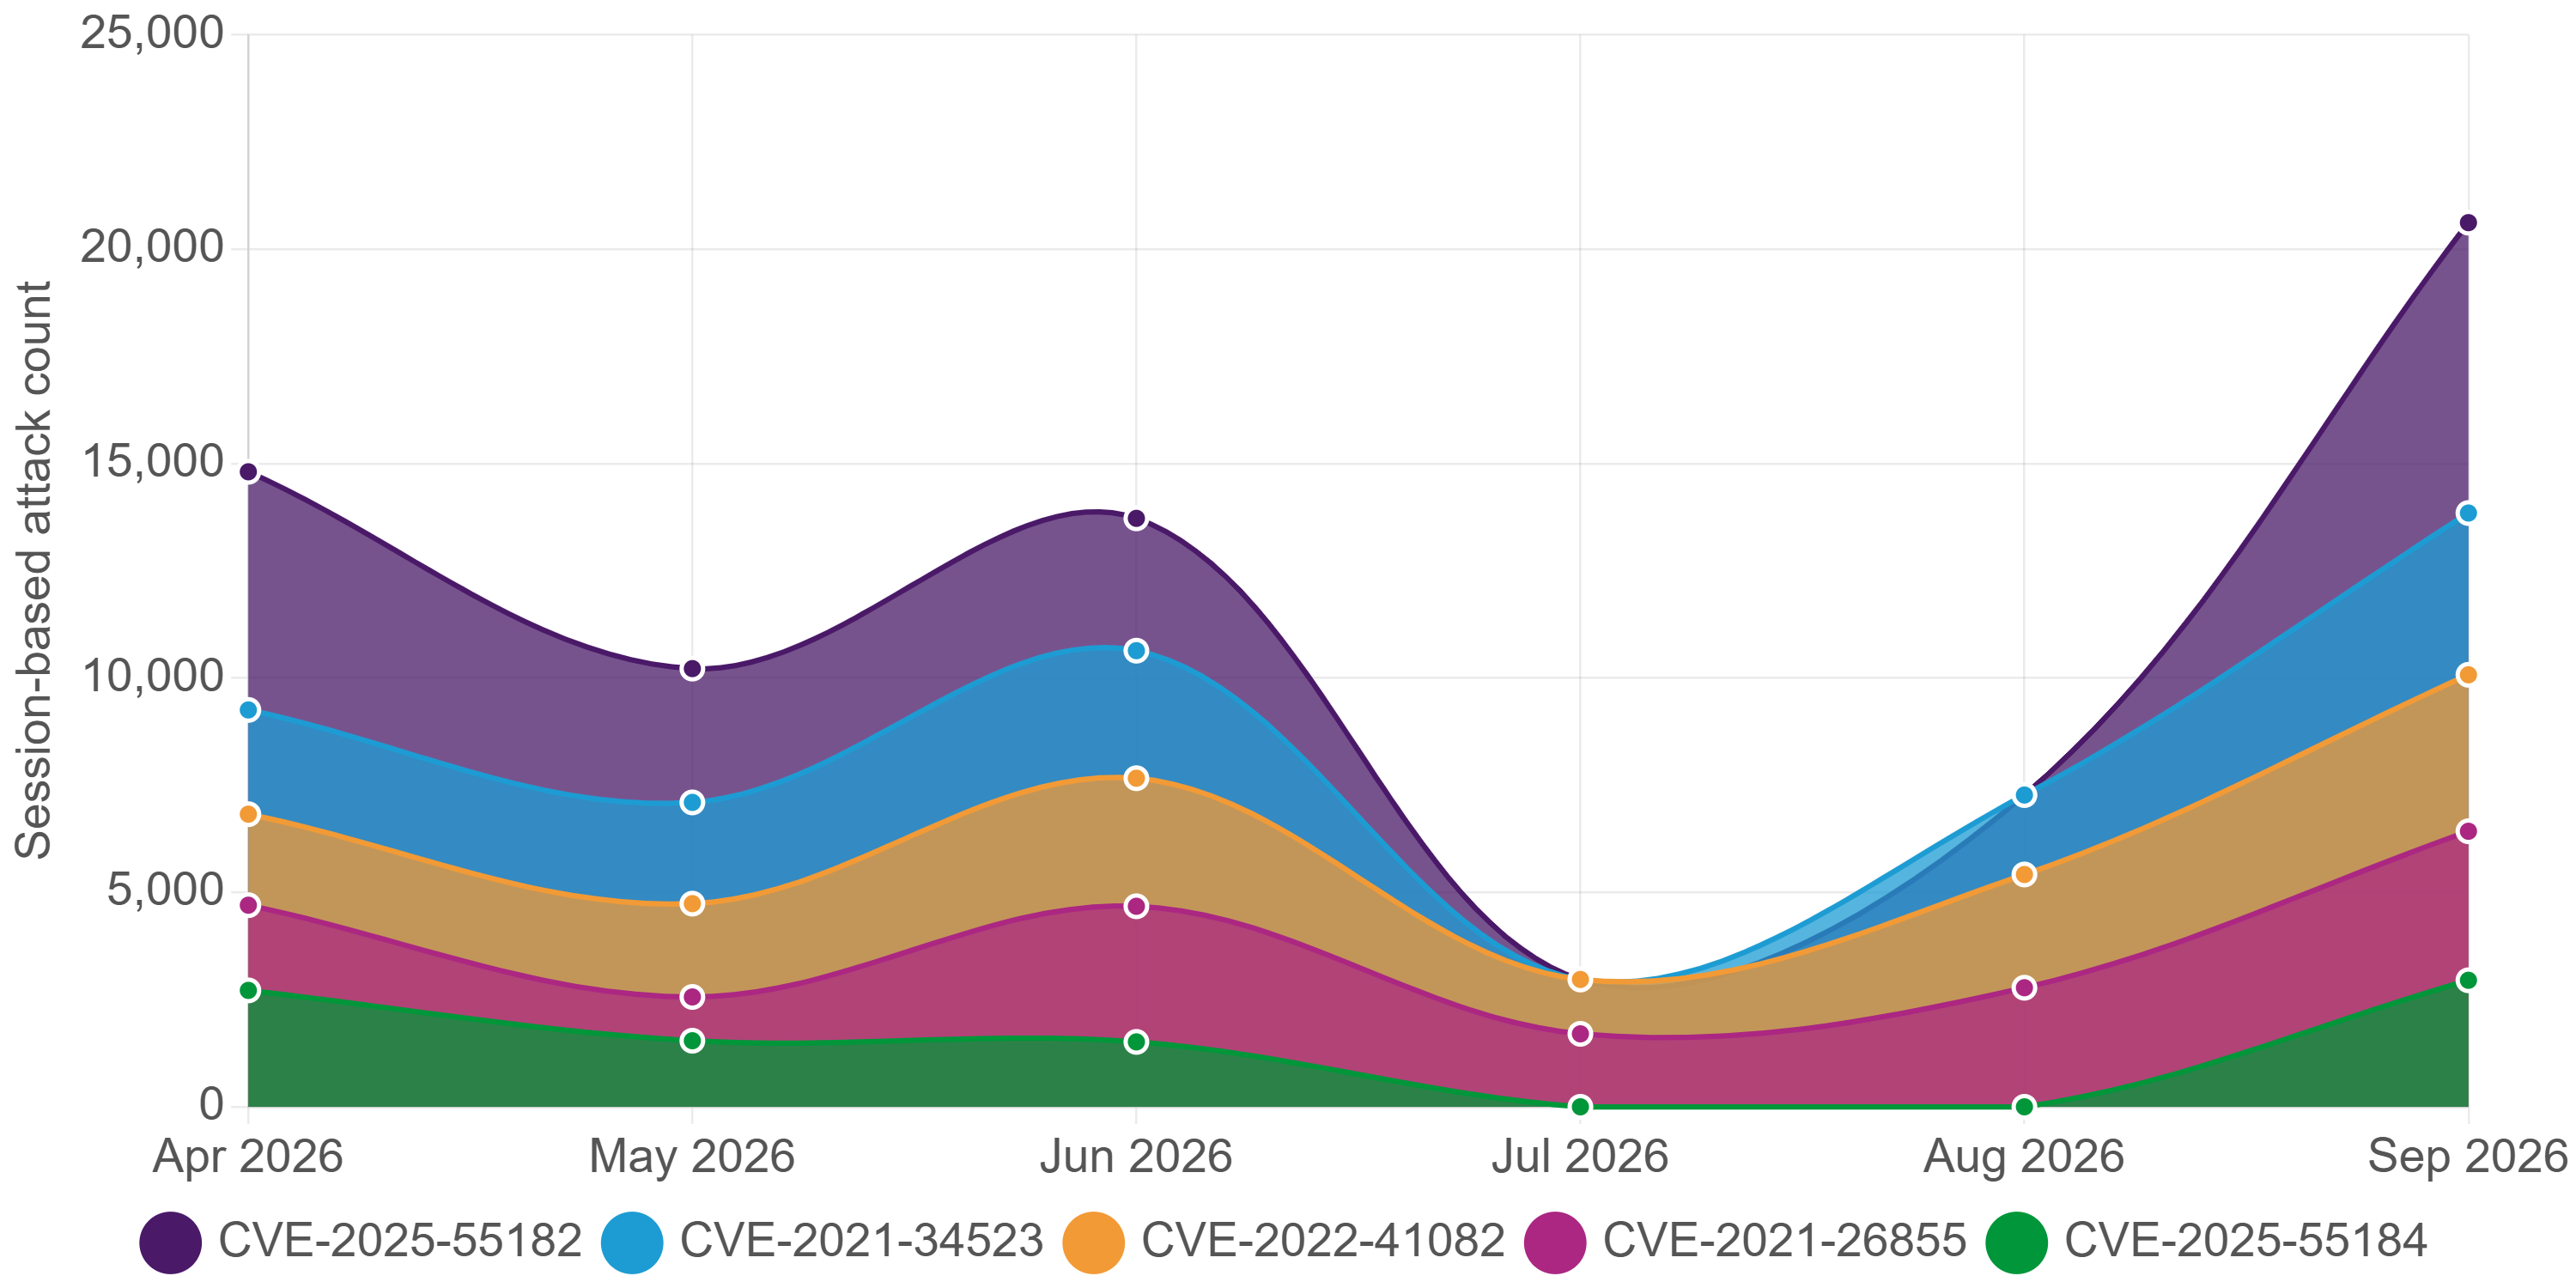
Exploitation Intelligence
Adversaries have exploited two known remote code execution vulnerabilities in the AI application platform Langflow, specifically CVE-2025-3248 and CVE-2026-0770. These exploits were detected during a period of active commodity crawling, with 3,968 and 4,770 connection attempts recorded respectively....
Threat actors are actively exploiting CVE-2026-66066, a critical Ruby on Rails vulnerability known as KindaRails2Shell, which allows unauthenticated attackers to read arbitrary files from servers, potentially leading to remote code execution (RCE). Disclosed on July 30, 2026, this flaw affects numer...
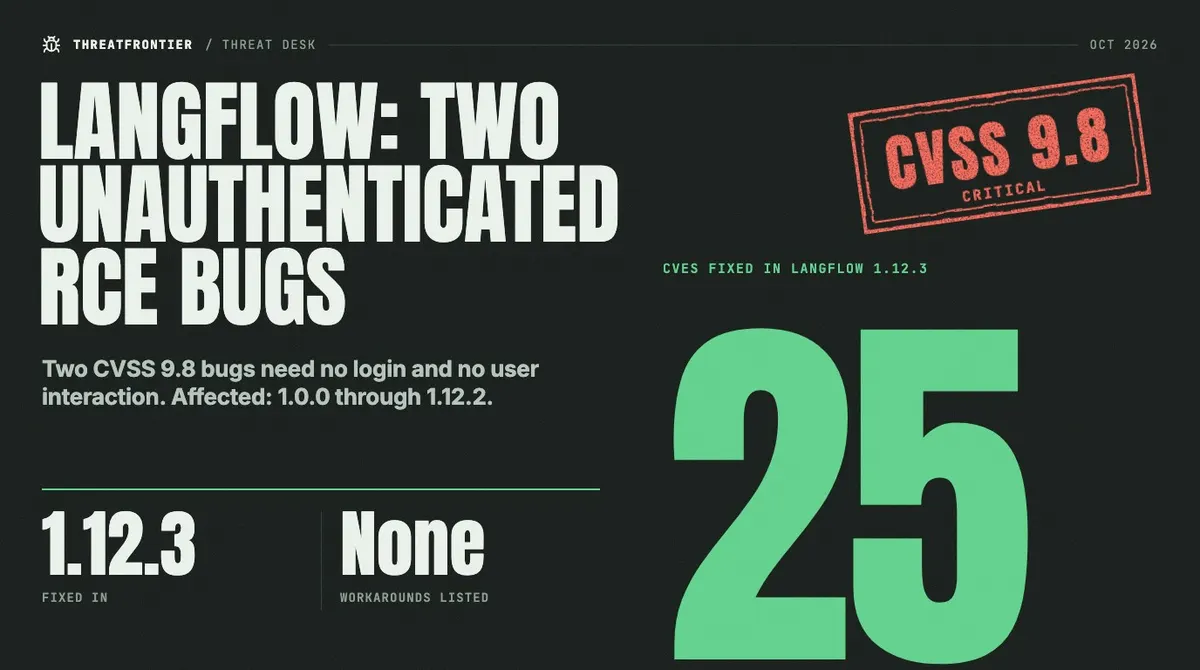
A critical vulnerability in Langflow, tracked as CVE-2026-33017, allows unauthenticated remote code execution (RCE) via the POST /api/v1/build_public_tmp/{flow_id}/flow endpoint. This flaw was exploited within 20 hours of its disclosure on March 20, 2026, with the first successful data exfiltration...
Recent research from Darktrace reveals the evolution of Chinese-nexus cyber operations over the past two decades, highlighting a shift from high-volume attacks to more strategic, identity-centric intrusions. This change reflects a broader integration of cyber operations into long-term geopolitical s...