Frequency
3
occurrences
First Seen
June 17, 2026
Last Seen
October 6, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
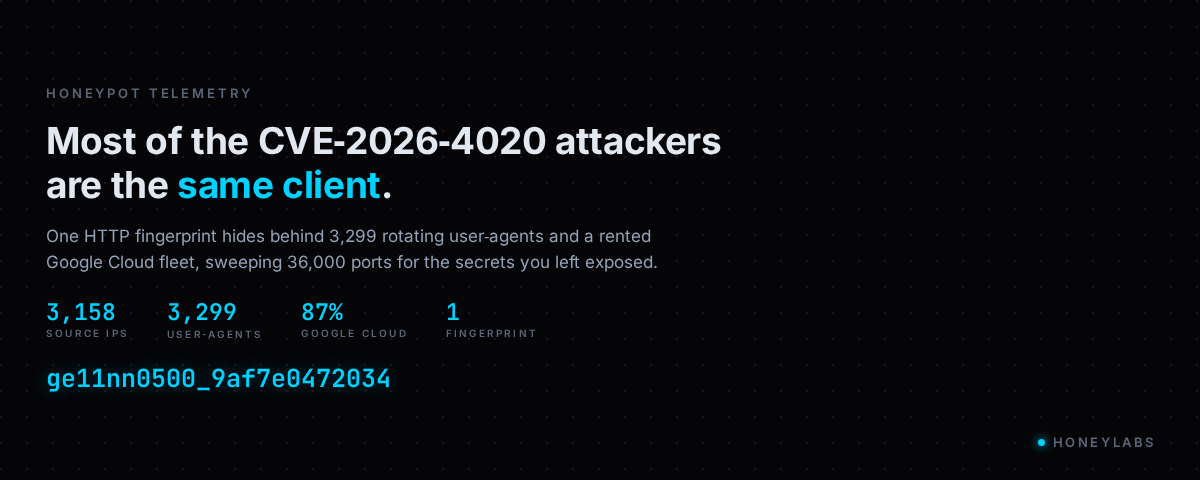
CVE-2026-4020 is an information disclosure vulnerability in the Gravity SMTP WordPress plugin, published on March 31, 2026. The flaw allows unauthenticated visitors to access sensitive system reports, including SMTP credentials and API keys, via a REST API endpoint. Active exploitation began on May...
In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. T...
Public Exploits
Checking GitHub for proof-of-concept code…