Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Multiple critical vulnerabilities affecting React Server Components and .js have been disclosed, including denial of service, server-side request forgery, and middleware bypass issues. These flaws impact versions 13.x to 16.x of .js and 19.x of React Server Components. Vercel has released patches fo...
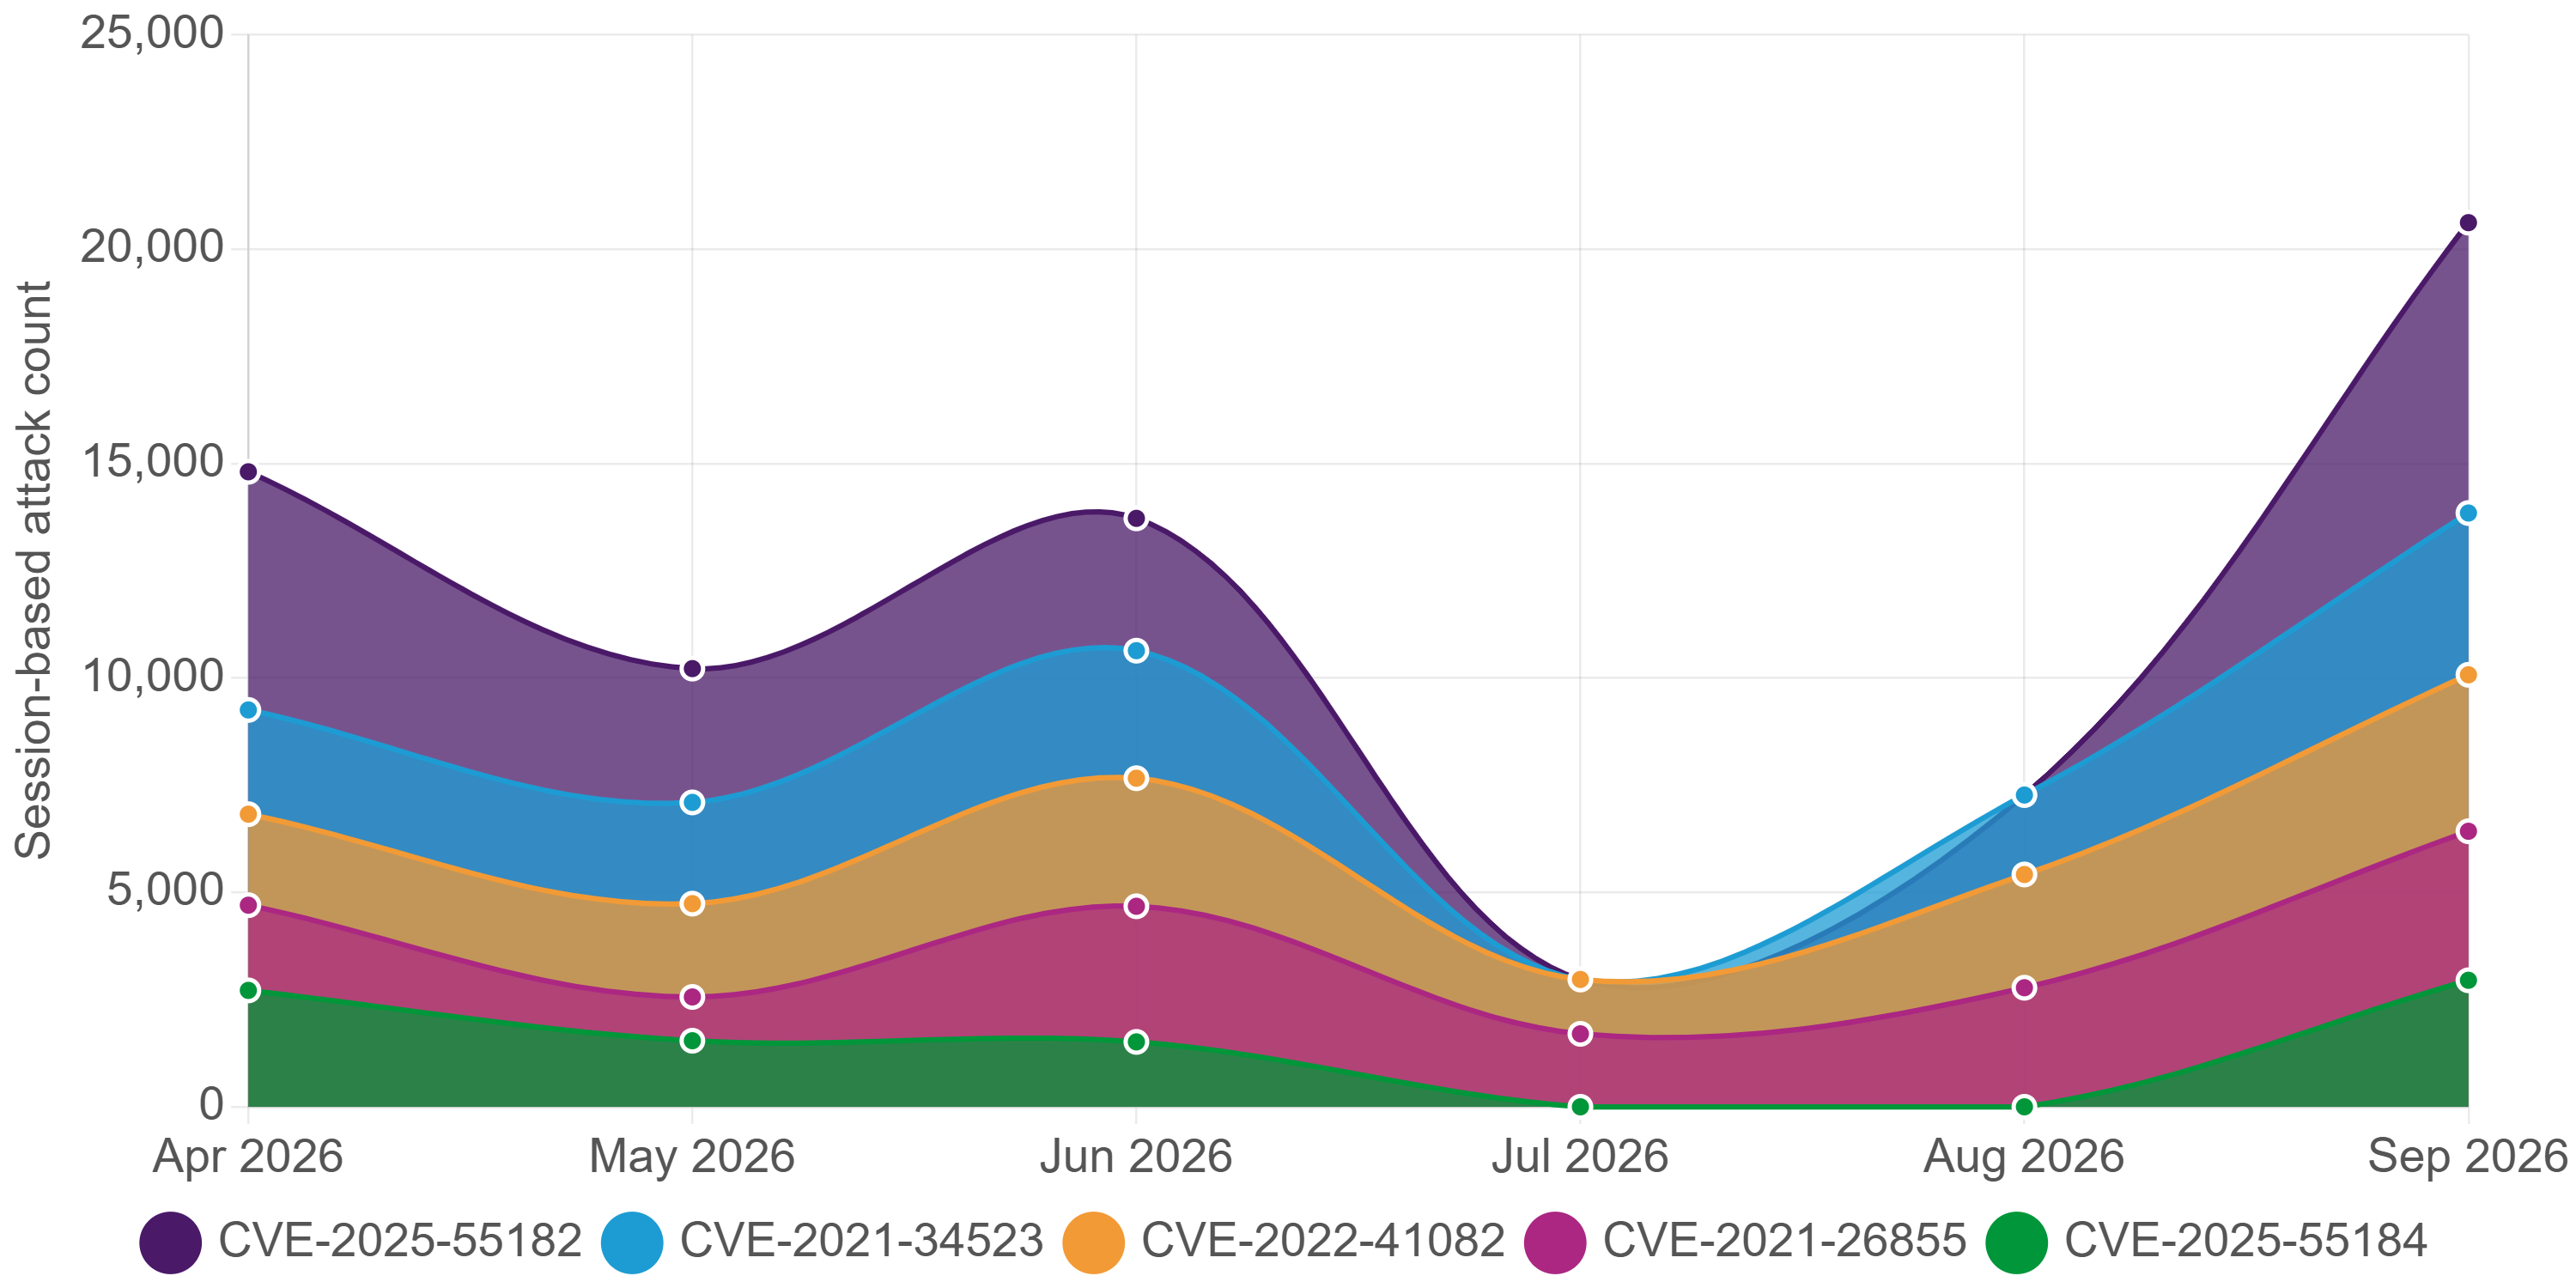
In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. T...
Two vulnerabilities have been identified in React Server Components versions 19.0.0 to 19.2.1. CVE-2025-55184 is a pre-authentication denial of service vulnerability, while CVE-2025-55183 is an information leak vulnerability that can expose source code through crafted HTTP requests. The affected pac...
Two vulnerabilities have been identified in the React Server Components (RSC) protocol during a security review of patches for React2Shell. These vulnerabilities do not allow for Remote Code Execution, and the existing patch for React2Shell remains effective. The vulnerabilities were discovered by s...