Vulnerability Overview
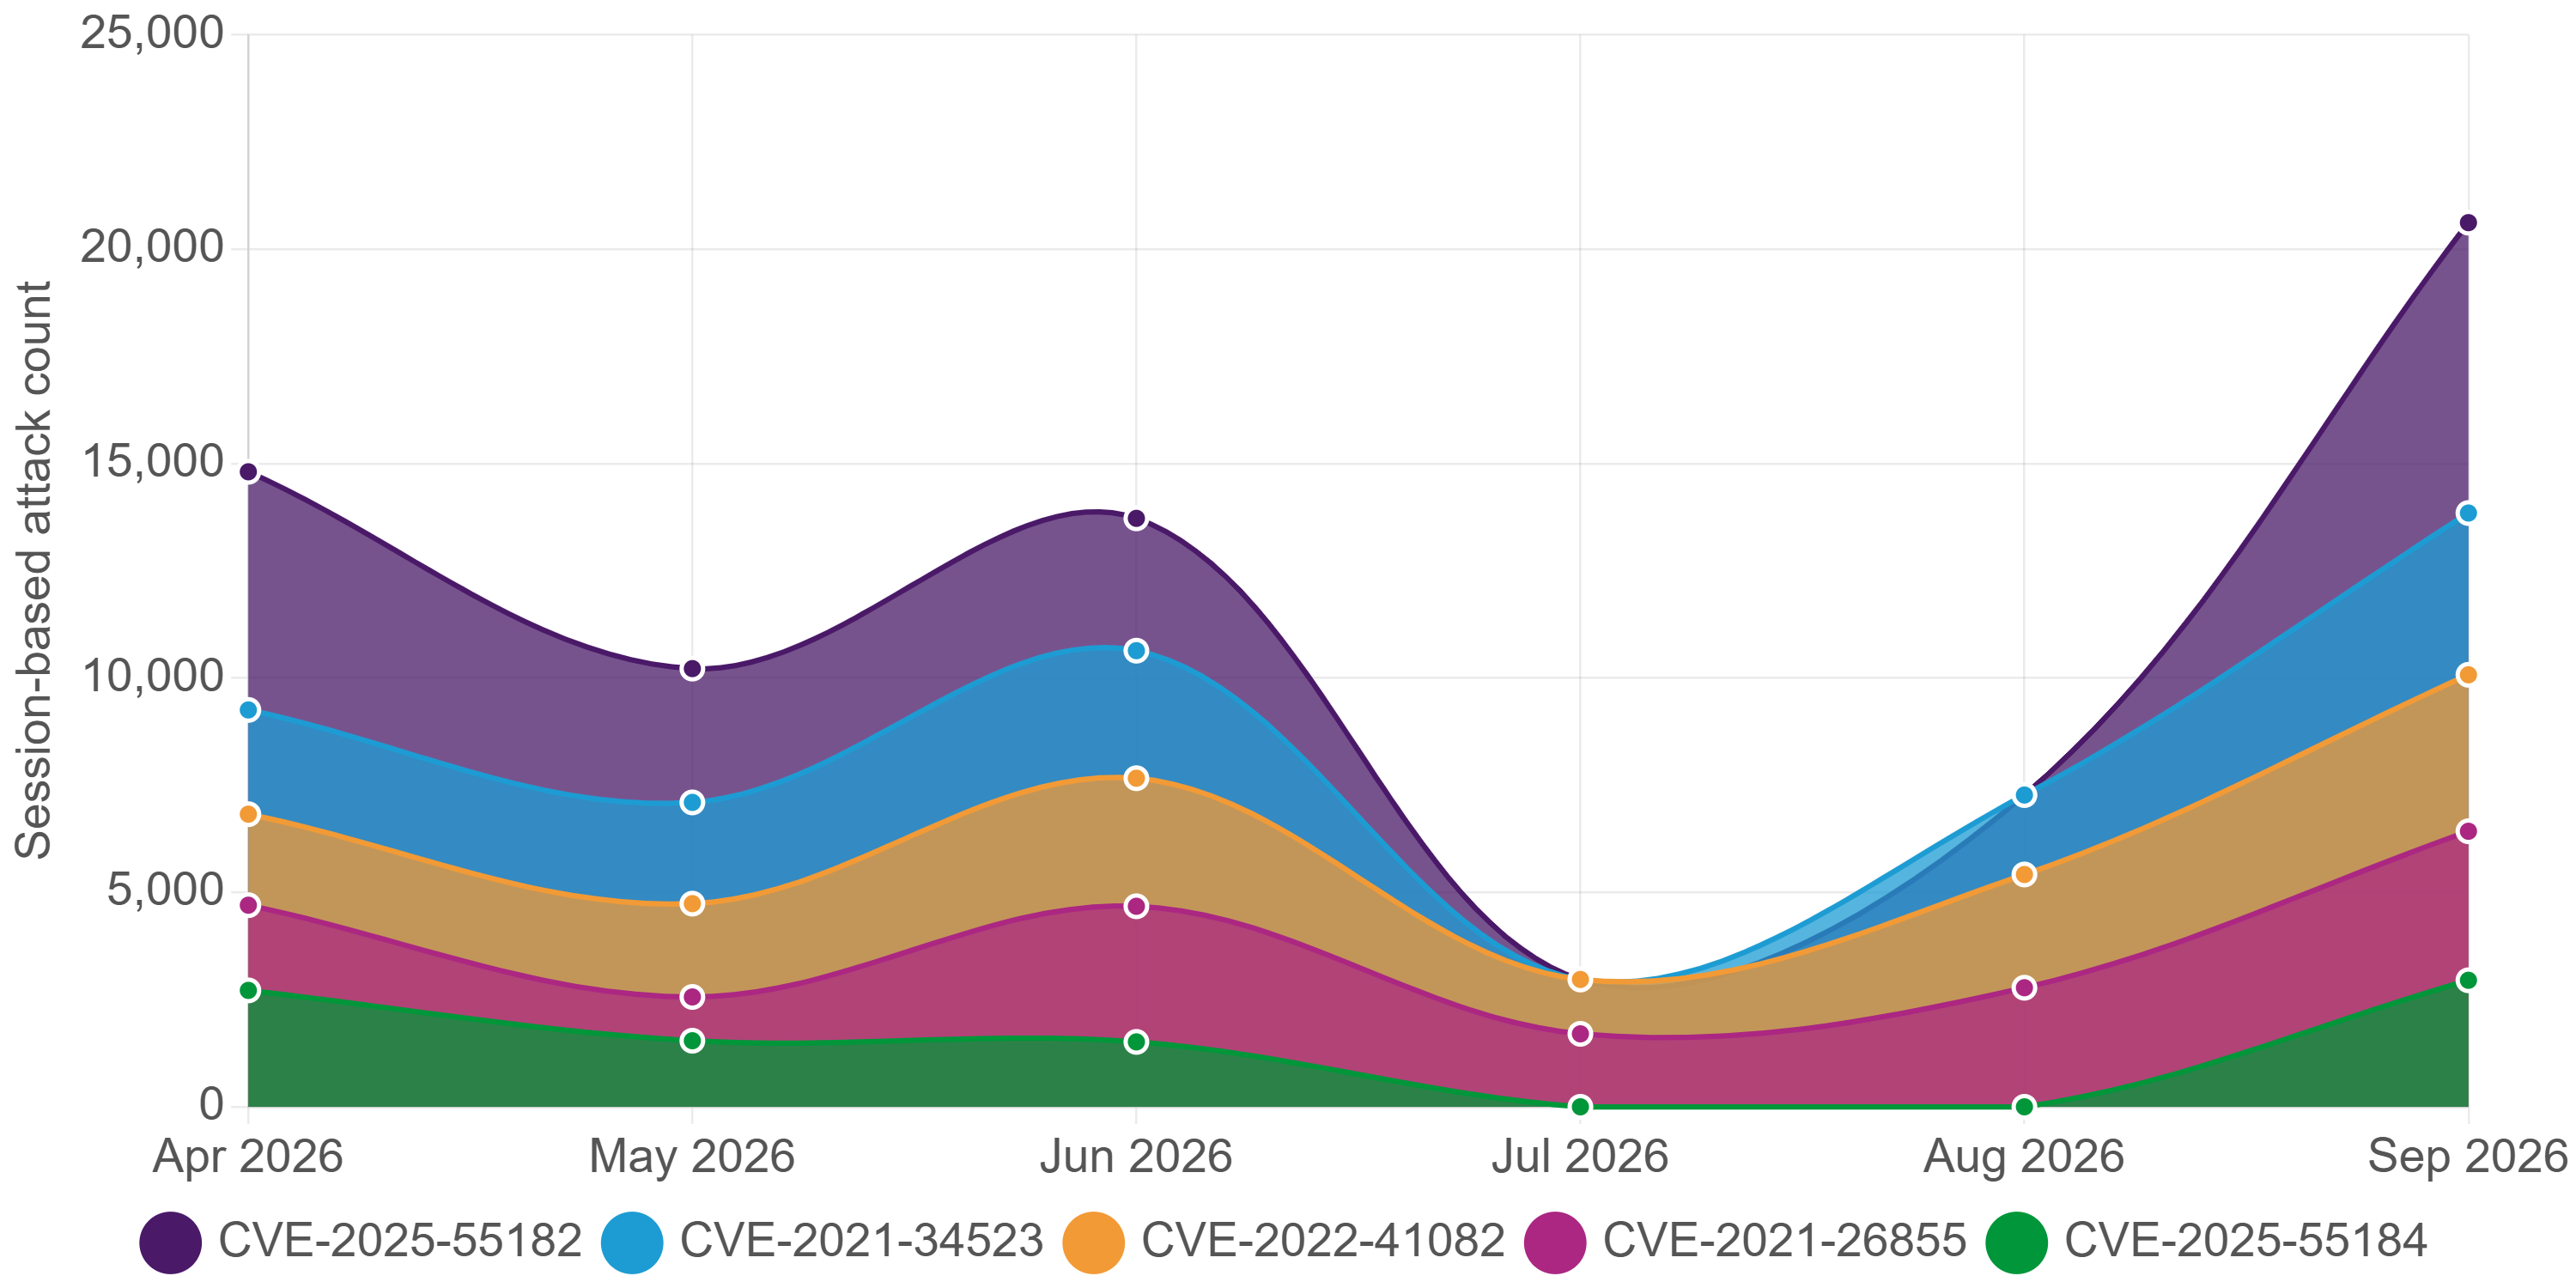
Exploitation Activity
Exploitation Intelligence
Google has released an emergency update for Chrome to address CVE-2026-85046, a high-severity zero-day vulnerability in the V8 JavaScript and WebAssembly engine, rated 8.8 on the CVSS scale. The flaw, identified as a type confusion issue, allows remote attackers to execute arbitrary code within Chro...
Hackers are actively exploiting a critical vulnerability in Langflow, tracked as CVE-2026-0768, which allows unauthenticated remote code execution. The flaw affects all versions up to 1.4.2 of the AI-focused low-code platform Langflow, enabling attackers to execute arbitrary Python code with root pr...
Threat actors are actively exploiting CVE-2026-66066, a critical Ruby on Rails vulnerability known as KindaRails2Shell, which allows unauthenticated attackers to read arbitrary files from servers, potentially leading to remote code execution (RCE). Disclosed on July 30, 2026, this flaw affects numer...
Google's September 2026 Android Security Bulletin addresses 180 vulnerabilities, including 95 bugs from the 2026-09-01 patch level and 85 from the 2026-09-05 patch level. The most severe vulnerability, CVE-2026-28662, allows remote code execution without user interaction. Samsung's September update...