Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
FamousSparrow, a China-aligned APT group, launched a multi-wave cyberespionage campaign against an Azerbaijani oil and gas company from late December 2025 to February 2026. The attackers employed an evolved DLL sideloading technique to deploy the Deed RAT and Terndoor backdoors, enhancing their evas...
In August 2026, a mass-scanning campaign targeted internet-exposed Vite development servers to steal sensitive cloud credentials and configuration files from AWS and Azure. The attackers exploited CVE-2026-39364, a high-severity vulnerability allowing unauthenticated access to restricted files via m...
In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. T...
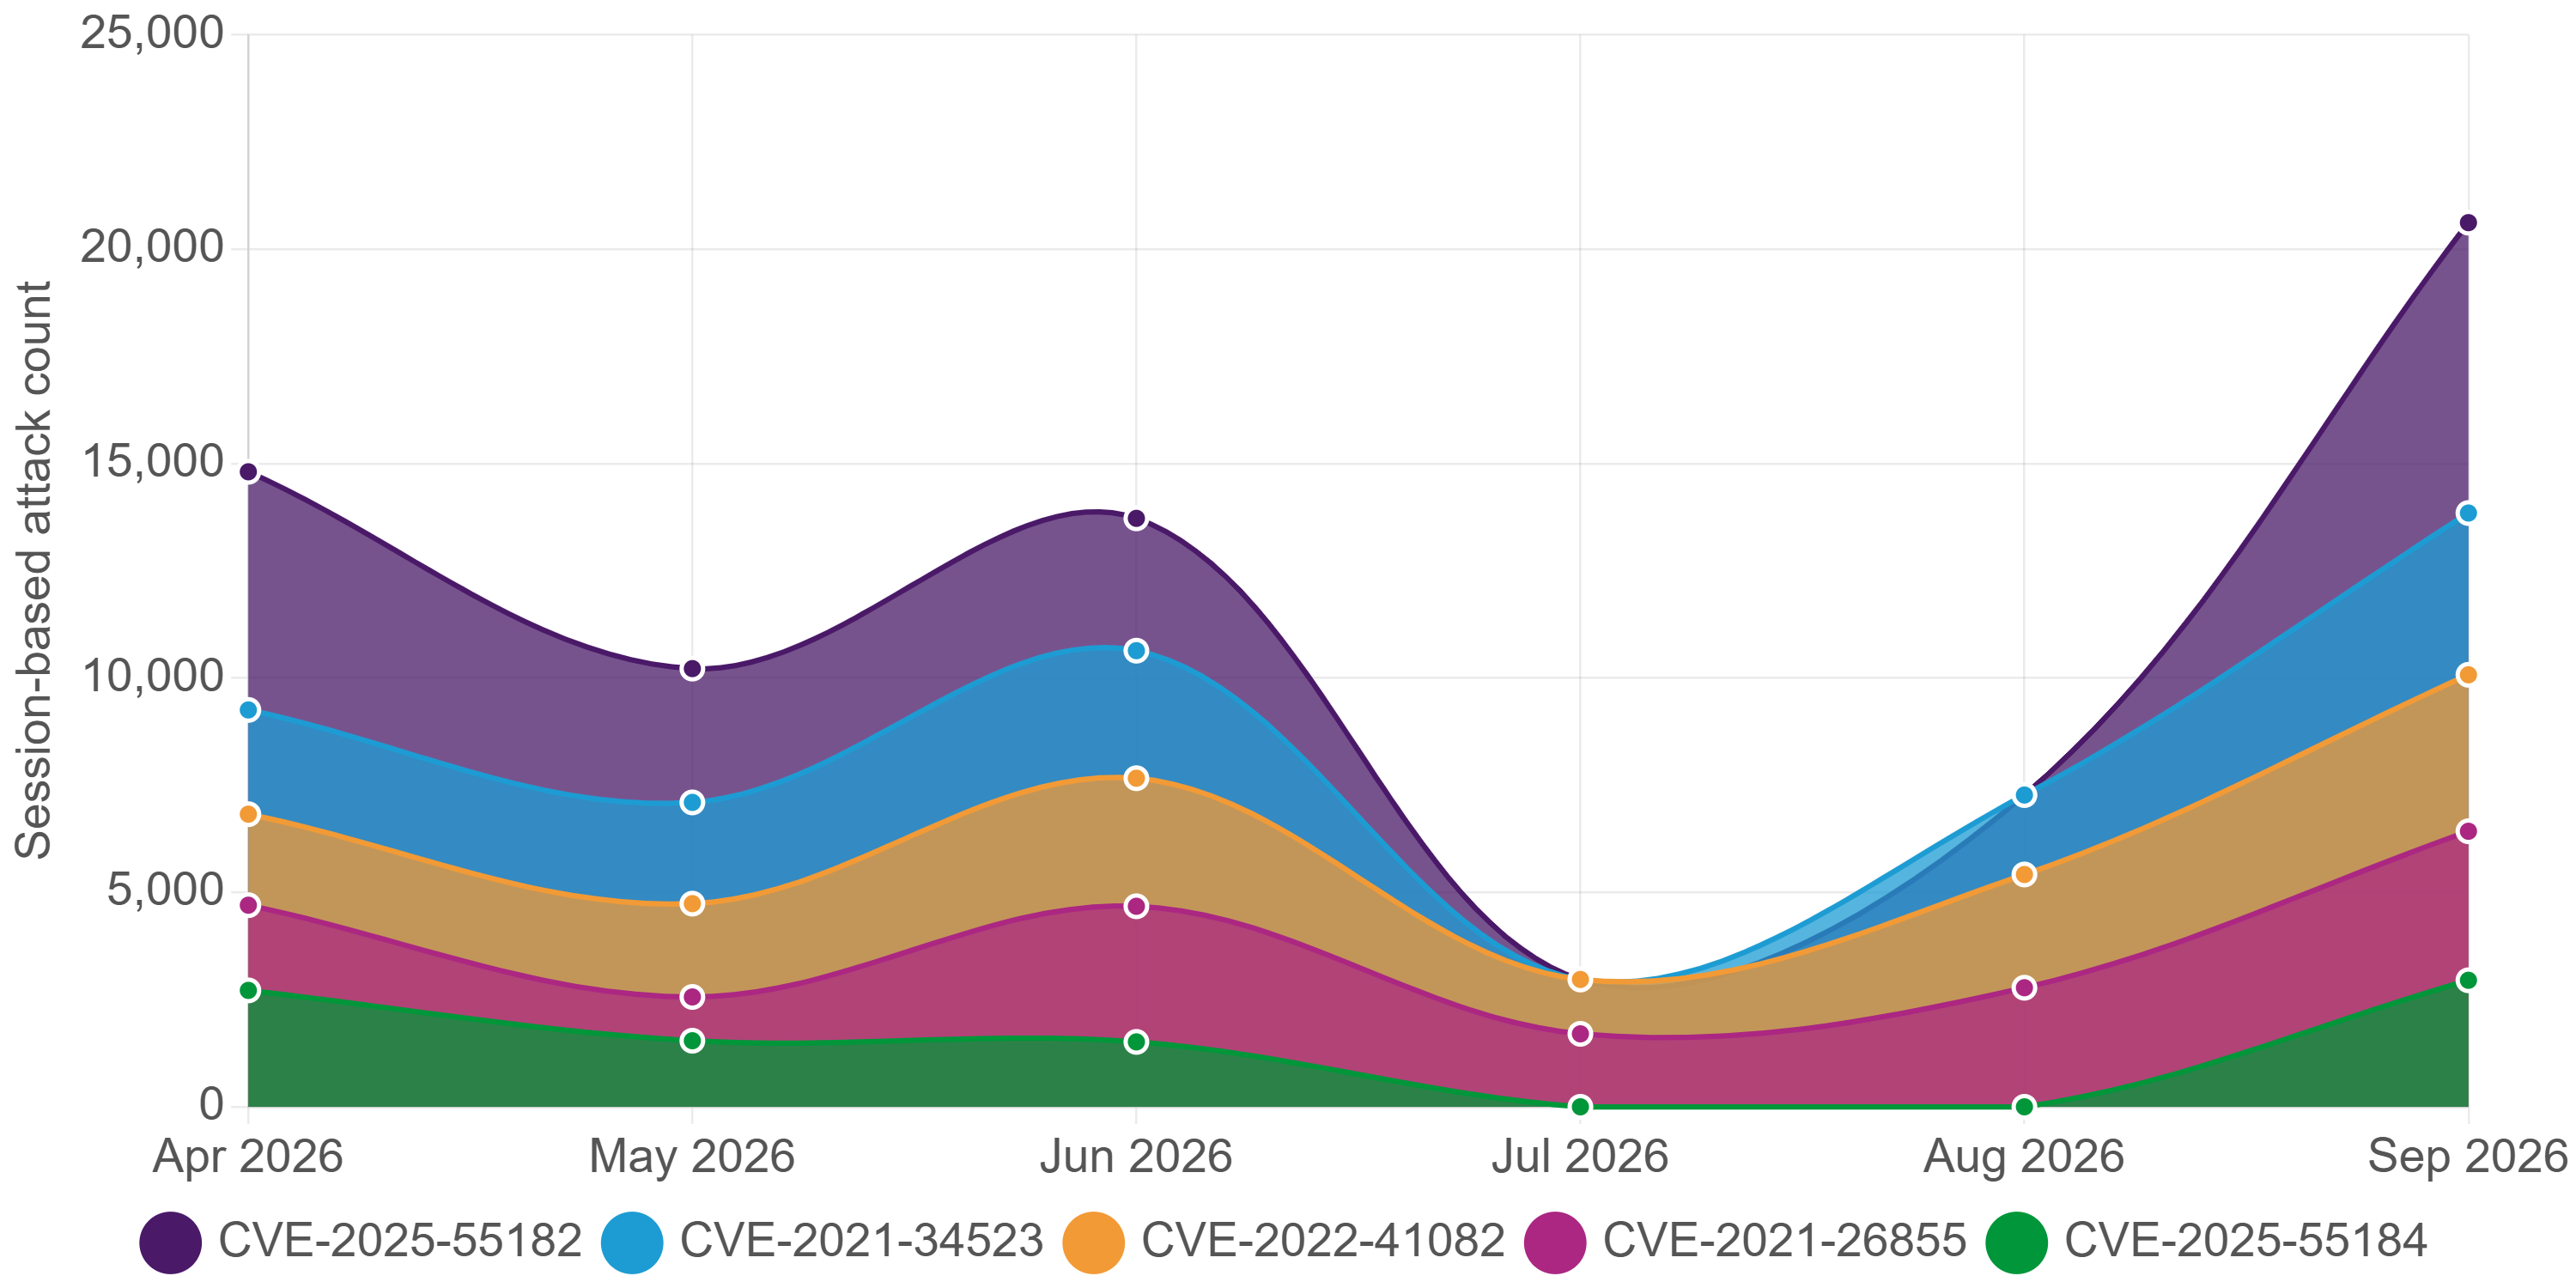
Organizations face heightened risks from old vulnerabilities as the AI era progresses. A recent study by TrendAI™ Research highlights that cybercriminals continue to exploit long-disclosed vulnerabilities, with the oldest request targeting a flaw from 2011. The resurgence of the exploit market, part...