Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
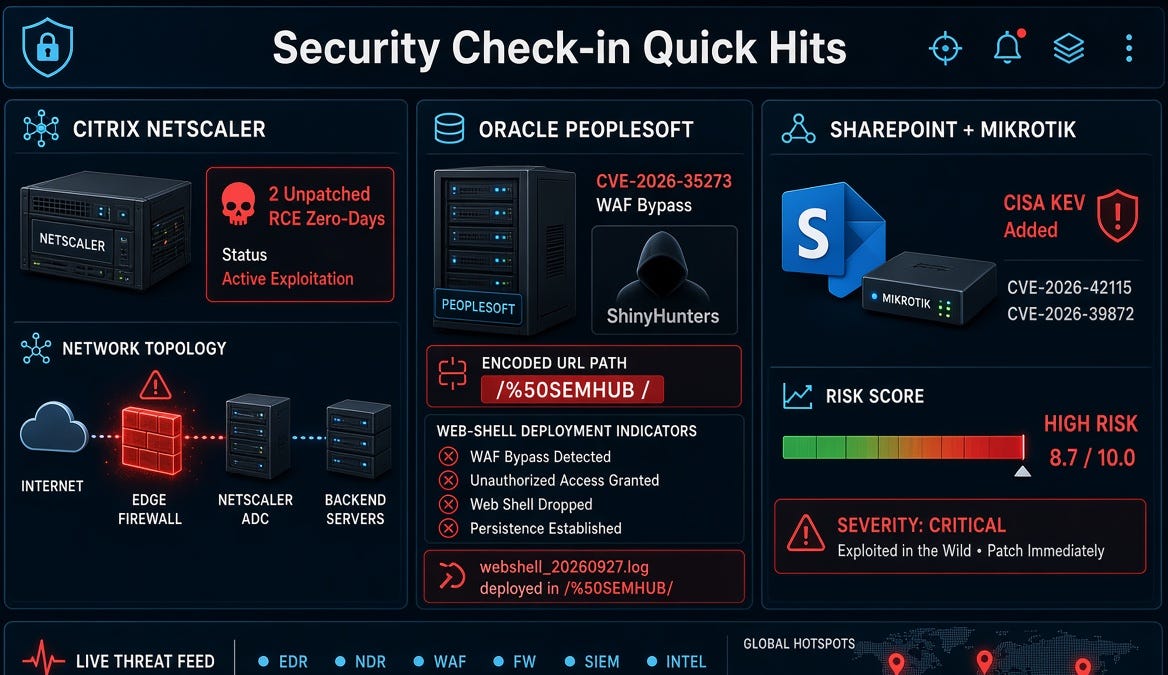
On September 26, 2026, security firm watchTowr reported two unpatched zero-day vulnerabilities in Citrix NetScaler ADC and Gateway appliances, allowing remote code execution (RCE) and actively exploited in the wild. Citrix has confirmed the existence of these vulnerabilities, tracked as CVE-2026-887...
Two critical vulnerabilities, CVE-2026-67279 and CVE-2026-86060, allow unauthenticated SSH takeover of MikroTik RouterOS. CVE-2026-67279 exploits a state-machine flaw permitting rekey requests before authentication, while CVE-2026-86060 allows argument injection to gain full admin access. These vuln...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two vulnerabilities to its Known Exploited Vulnerabilities catalog, confirming active exploitation. The vulnerabilities include CVE-2026-65660, a code injection flaw in Microsoft SharePoint Server, which allows authenticated...