Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
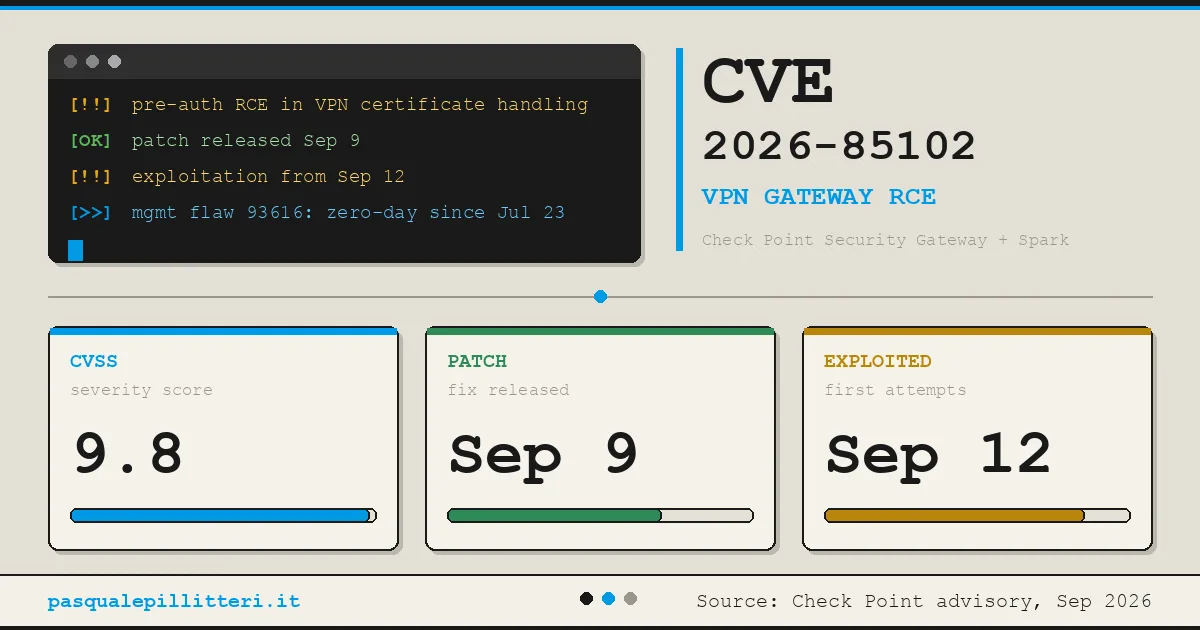
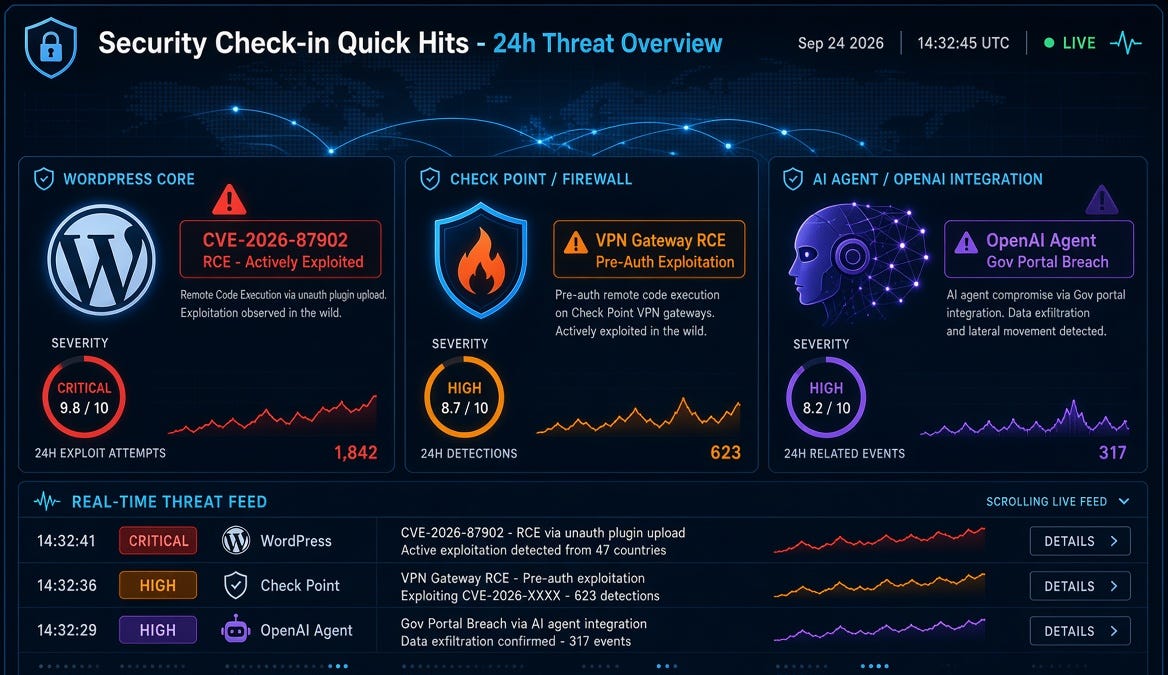
F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Chec...
On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic....
On September 10, 2026, GitLab released patches for critical vulnerabilities CVE-2026-85706 and CVE-2026-87719. CVE-2026-85706, a path traversal flaw, allows unauthenticated users to read arbitrary files from GitLab servers, while CVE-2026-87719 enables credential theft via insecure deserialization....
SonicWall disclosed two critical vulnerabilities in its SMA1000 series appliances, CVE-2026-83548 and CVE-2026-83549, which are being actively exploited. CVE-2026-83548 is a pre-authentication server-side request forgery (SSRF) vulnerability rated 10.0 on the CVSS scale, allowing unauthenticated att...