Frequency
10
occurrences
First Seen
September 7, 2026
Last Seen
September 7, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
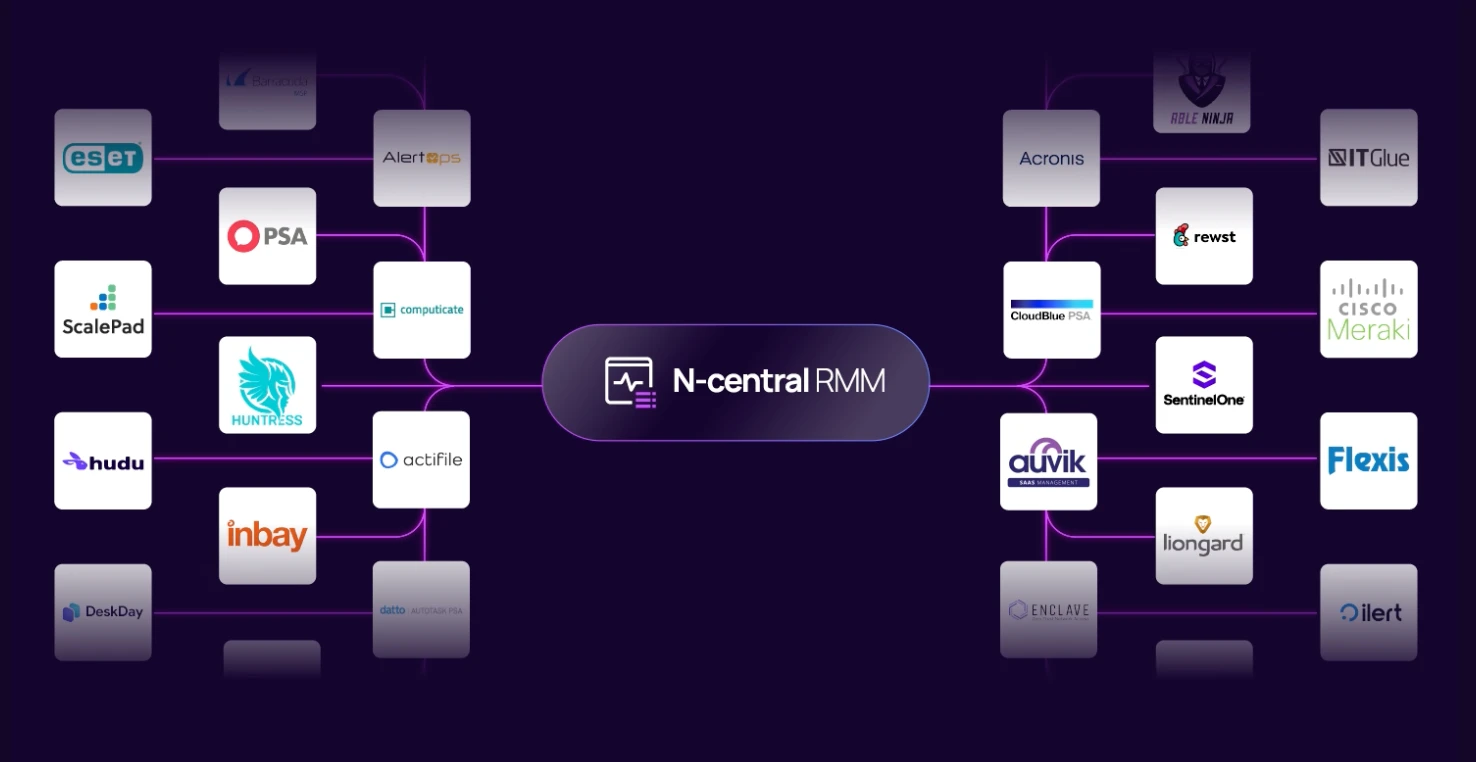
N-able has released Hotfix 4 for its N-central platform to address CVE-2026-86218, a critical remote code execution (RCE) vulnerability rated CVSS 10.0. This flaw allows unauthenticated attackers to execute arbitrary code on N-central servers running versions prior to 2026.3.1.14. The vulnerability...
Public Exploits
Checking GitHub for proof-of-concept code…
Related Clusters (1)
Related Articles (10)




1 / 2