Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
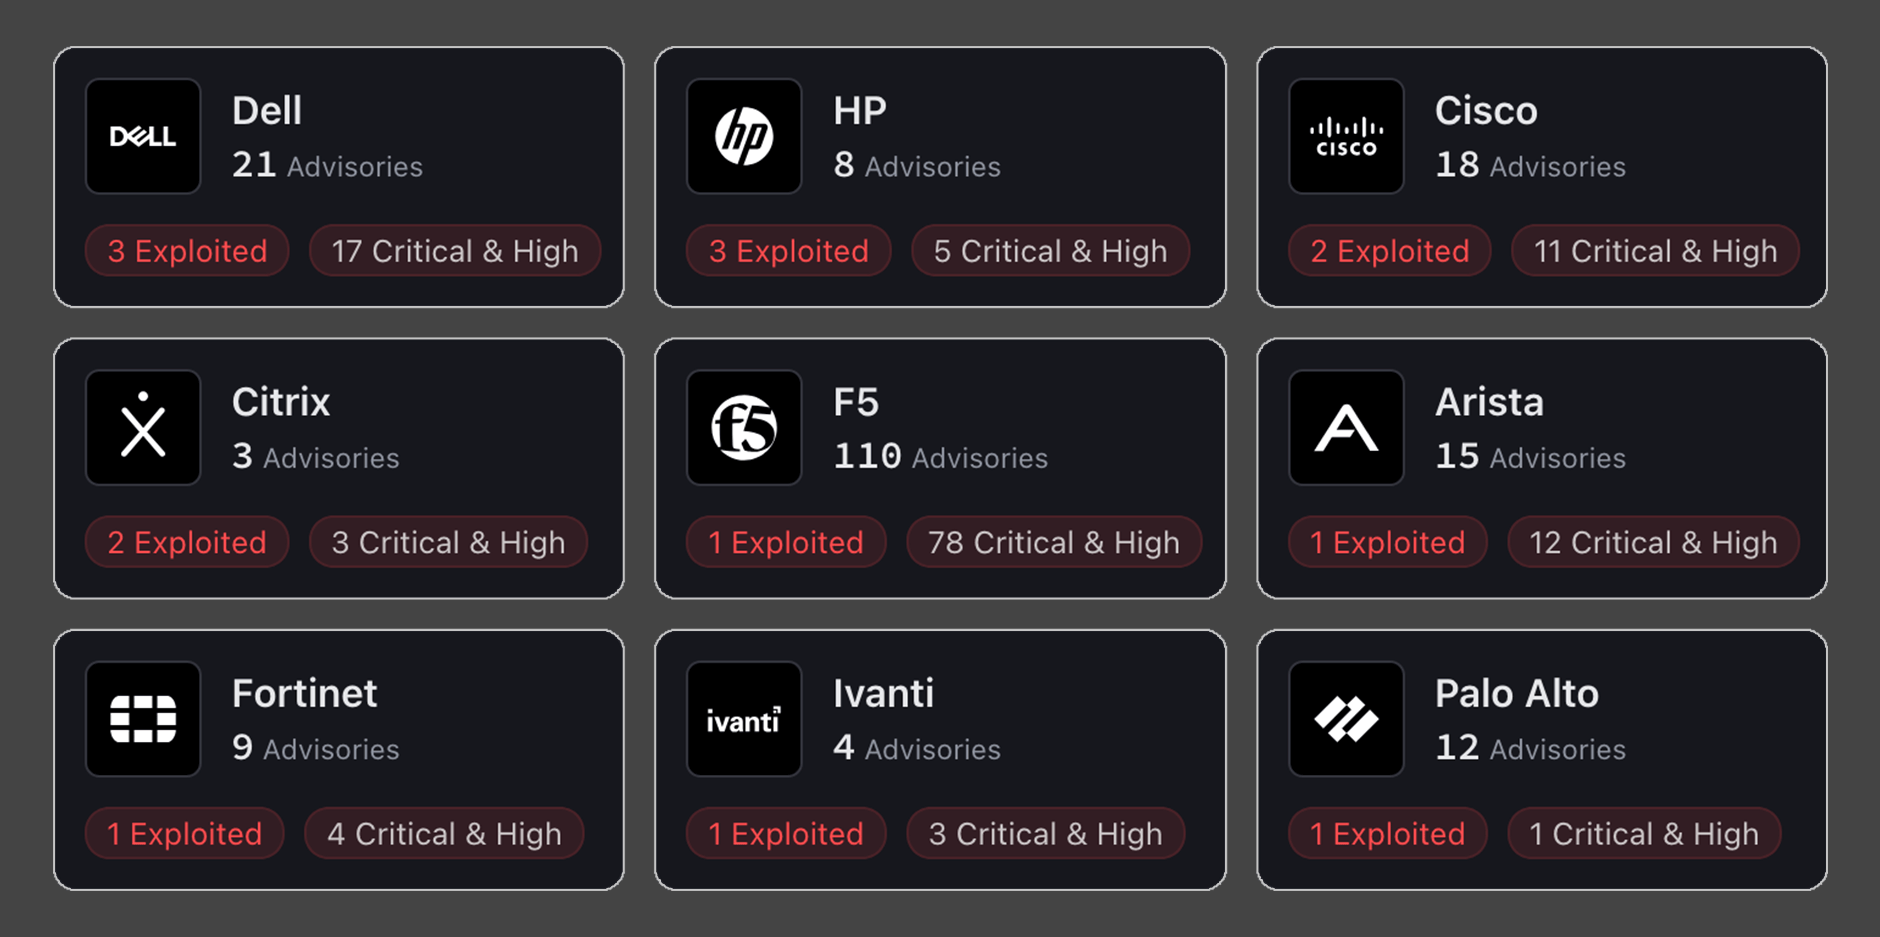
Recent reports indicate multiple critical vulnerabilities are being actively exploited, including zero-day exploits for Citrix NetScaler ADC and Gateway (CVE-2026-88771, CVE-2026-88772) and PaperCut NG/MF. The vulnerabilities allow unauthenticated remote code execution, posing significant risks to a...
In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabi...
A critical vulnerability, CVE-2026-61500, in Rejetto HTTP File Server (HFS) allows unauthenticated remote code execution (RCE) due to a weak pseudo-random number generator (PRNG) used for session keys. Discovered by Anthropic's Mythos AI, the flaw affects HFS versions 3.0.0 to 3.2.0, with a CVSS sco...
CISA has added two vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog due to evidence of active exploitation. CVE-2026-102489, a session fixation vulnerability in Zammad, and CVE-2026-102490, an improper privilege management vulnerability in Zammad, were added on 2026-10-02. Additi...