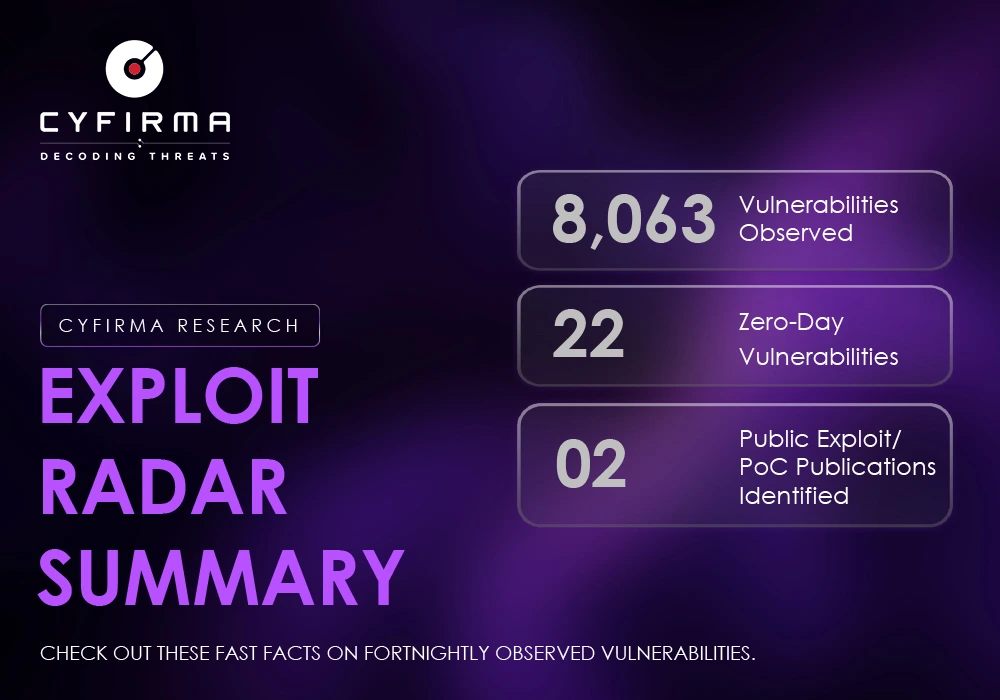
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Atlassian has disclosed a critical remote code execution vulnerability (CVE-2026-90436) affecting Confluence Data Center, which utilizes a vulnerable third-party library, Apache Axis. This vulnerability allows attackers to execute arbitrary code if the 'Remote API (XML-RPC & SOAP)' feature is enable...
Beginning on October 30, 2026, attackers exploited unpatched vulnerabilities in Check Point Security Gateways, specifically the PHP2Shell flaws (CVE-2026-109618 and CVE-2026-109619) and a local privilege escalation vulnerability (CVE-2026-123039). The initial wave targeted Israeli organizations, lea...
CSIRT Italia has reported active exploitation of CVE-2026-90436 in Apache Axis 1.x, a vulnerability with a CVSS score of 9.8. This flaw allows unauthenticated remote attackers to execute arbitrary code via unsafe deserialization of incoming SOAP messages. A proof-of-concept (PoC) code for the exploi...