Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
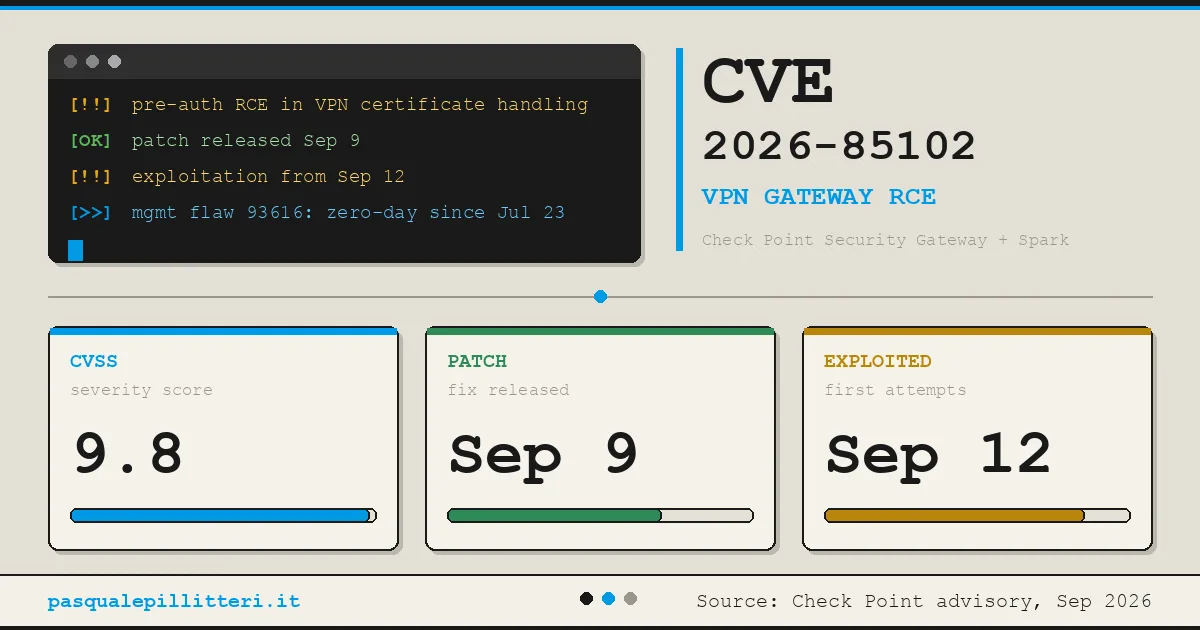
F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Chec...
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, with a CVSS score of 9.8. This path traversal vulnerability allows unauthenticated attackers to write arbitrary files on affected systems via crafted HTTP or HTTPS requests. The flaw has been confirmed to be ac...
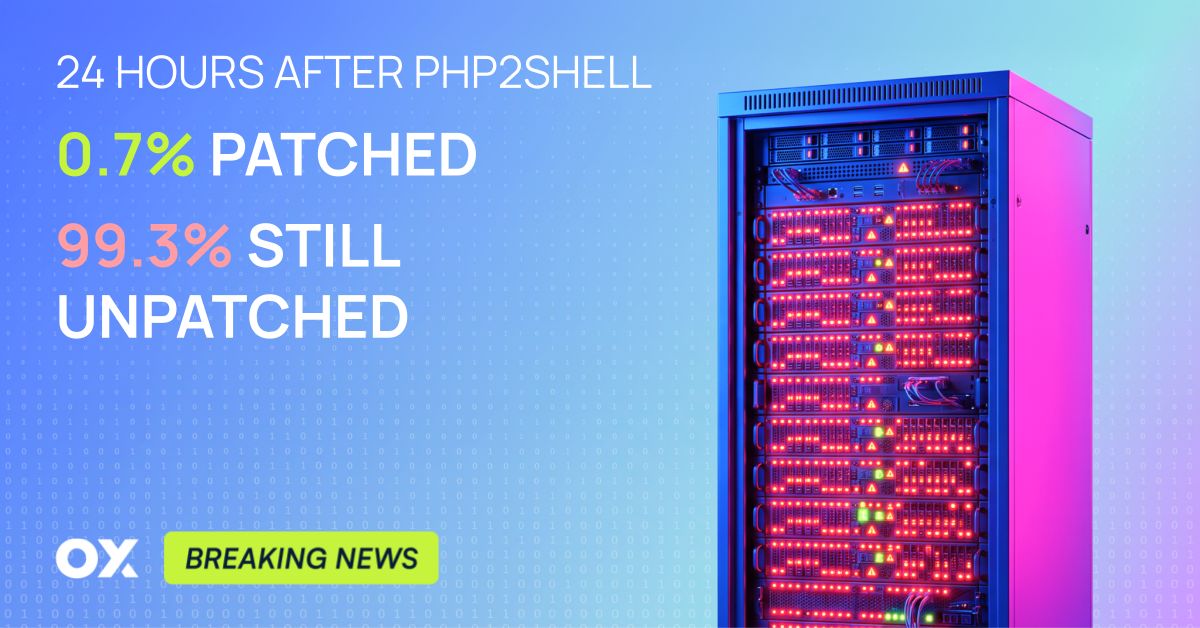
Two critical vulnerabilities in PHP, tracked as CVE-2026-109618 and CVE-2026-109619, were disclosed on October 21, 2026, allowing unauthenticated remote code execution (RCE). The vulnerabilities, collectively known as PHP2Shell, affect all PHP installations serving web requests, including popular pl...