Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
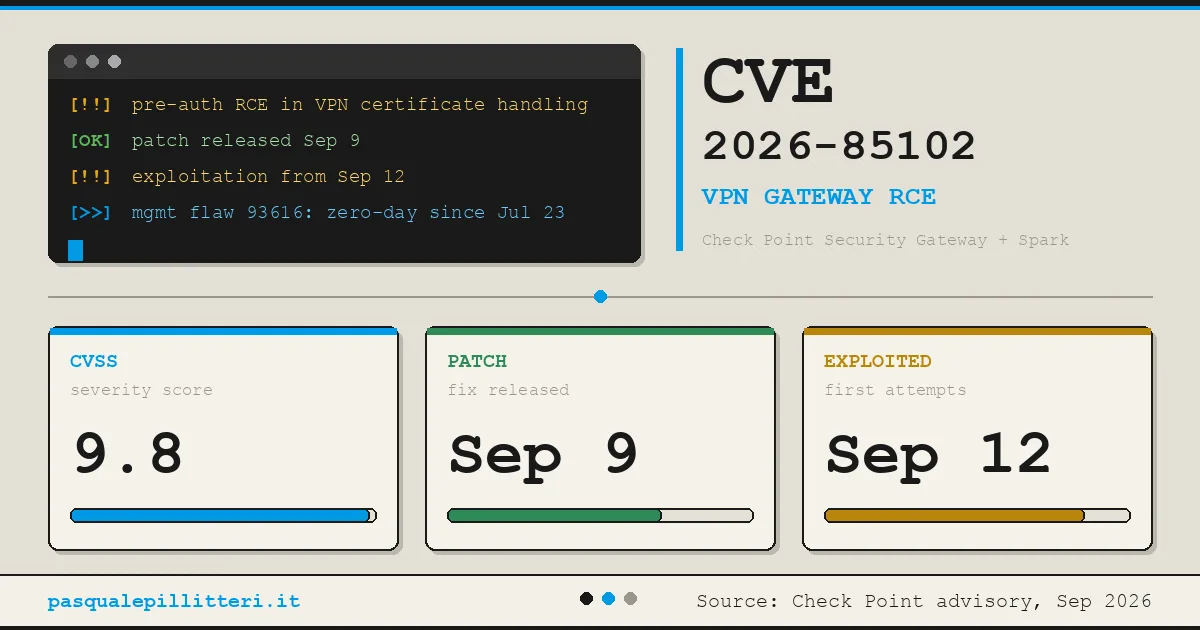
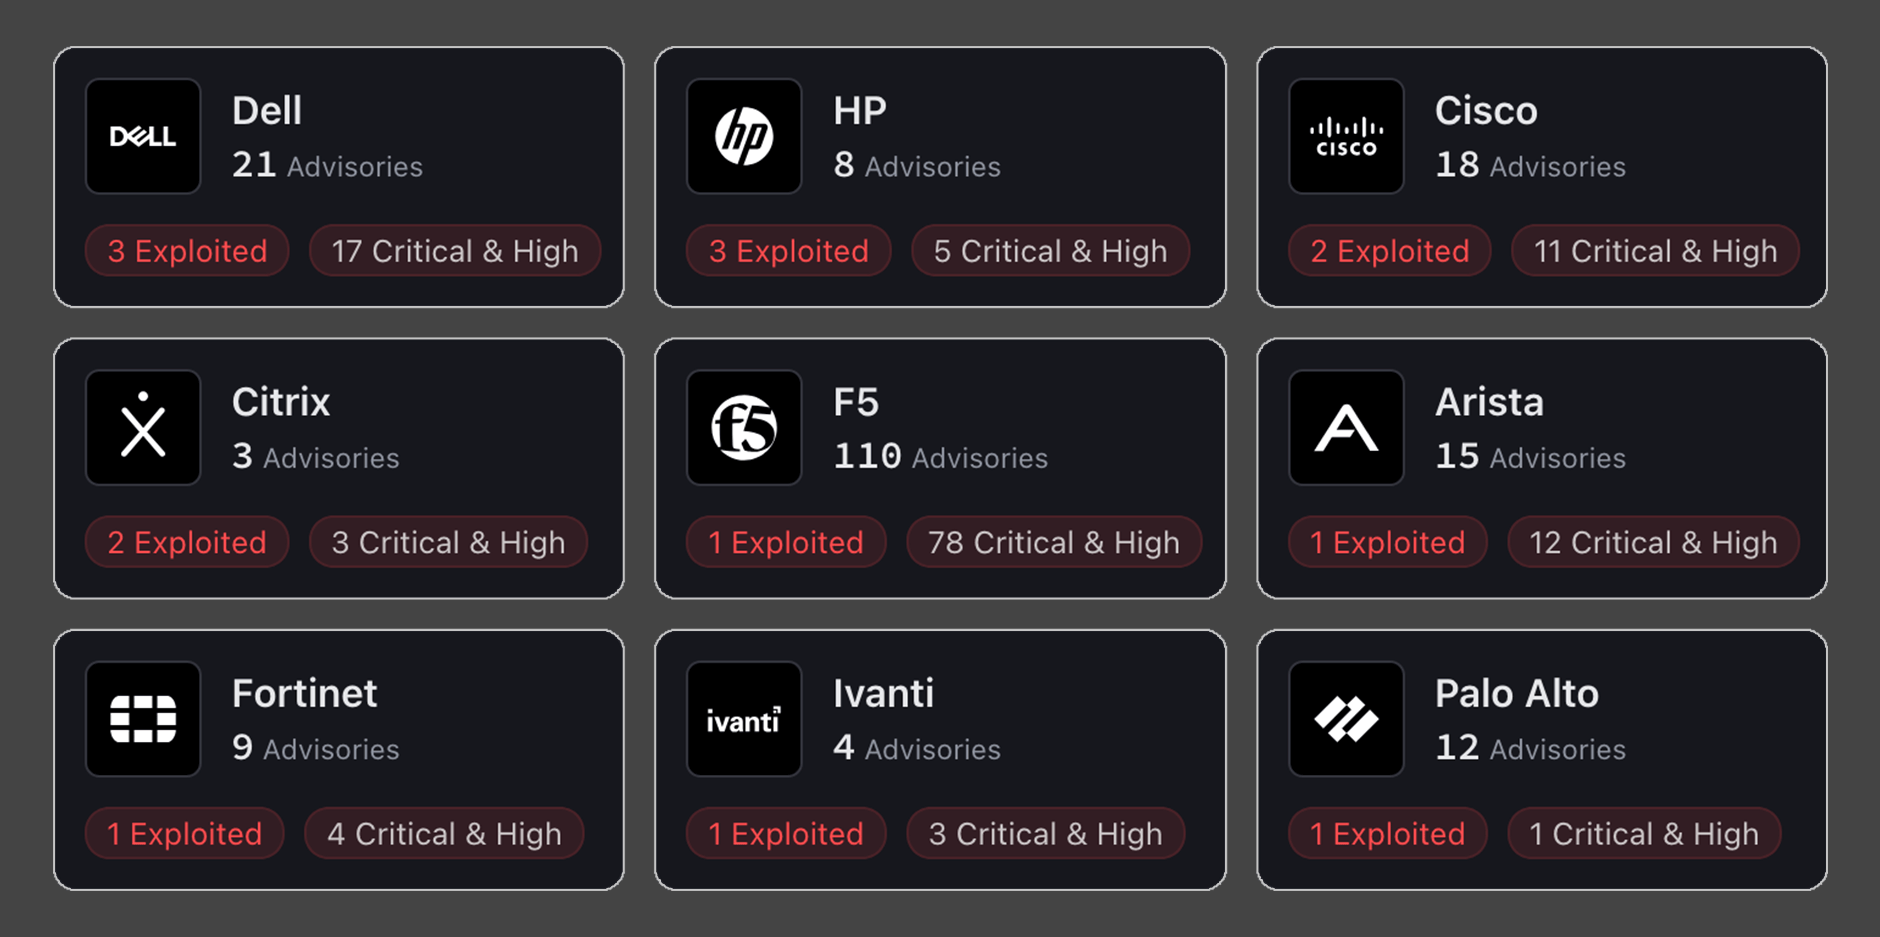
F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Chec...
F5 Networks has reported a critical vulnerability in its BIG-IP Access Policy Manager (APM), tracked as CVE-2026-94127, which is being actively exploited in the wild. The flaw allows unauthenticated attackers to execute remote code on systems configured with both an APM access policy and an OAuth pr...
On September 26, 2026, security firm watchTowr reported two unpatched zero-day vulnerabilities in Citrix NetScaler ADC and Gateway appliances, allowing remote code execution (RCE) and actively exploited in the wild. Citrix has confirmed the existence of these vulnerabilities, tracked as CVE-2026-887...
In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabi...