Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A vulnerability in Atlassian Data Center products, tracked as CVE-2026-21589 with a CVSS score of 9.3, was within two hours of its disclosure. The flaw allows arbitrary file access and affects multiple products, including Bitbucket, Confluence, and Jira. Exploitation activity targeting honeypot netw...
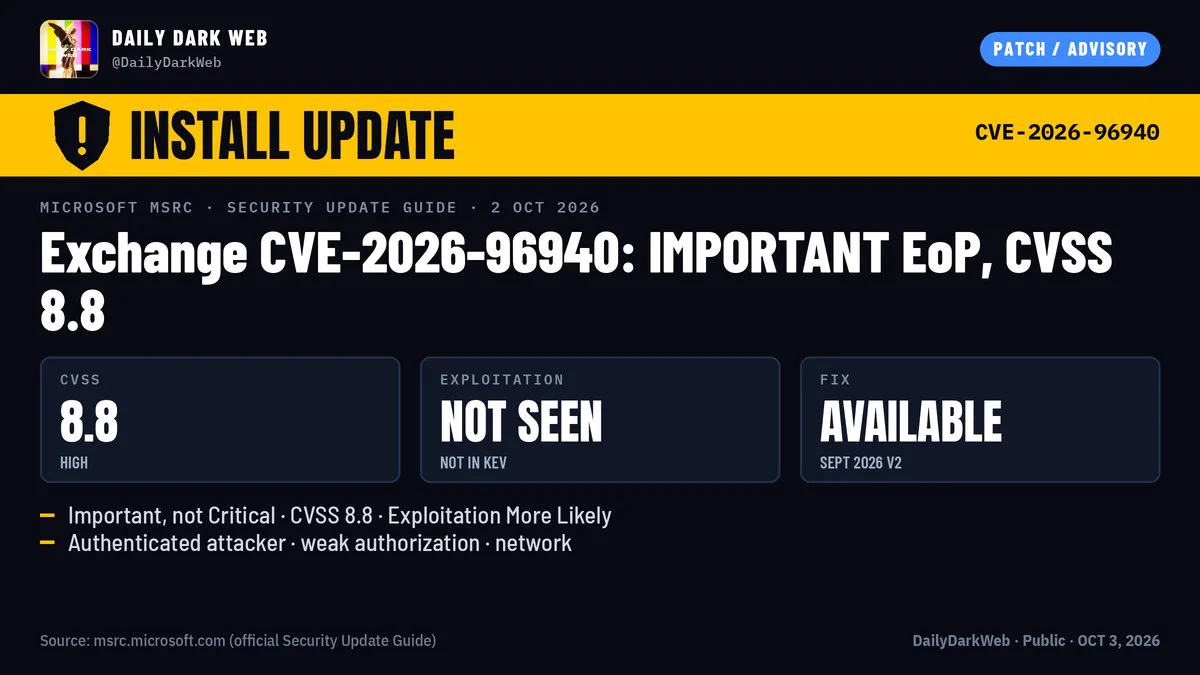
On October 2, 2026, Microsoft disclosed CVE-2026-96940, a privilege escalation vulnerability in Microsoft Exchange Server. This flaw allows authenticated attackers to gain unauthorized access to other users' mailboxes within the same organization. The vulnerability has a CVSS score of 8.8, categoriz...
Microsoft has released an out-of-band security update for Exchange Server to address CVE-2026-96940, a high-severity vulnerability rated 8.8 on the CVSS scale. This flaw allows authenticated attackers to escalate privileges and access other users' mailboxes within the same organization. The vulnerab...