Dark Web Intelligence on X: "🇺🇸🚨 MICROSOFT EXCHANGE CVE-2026-96940 — IMPORTANT EOP IN SEPT 2026 V2 SU
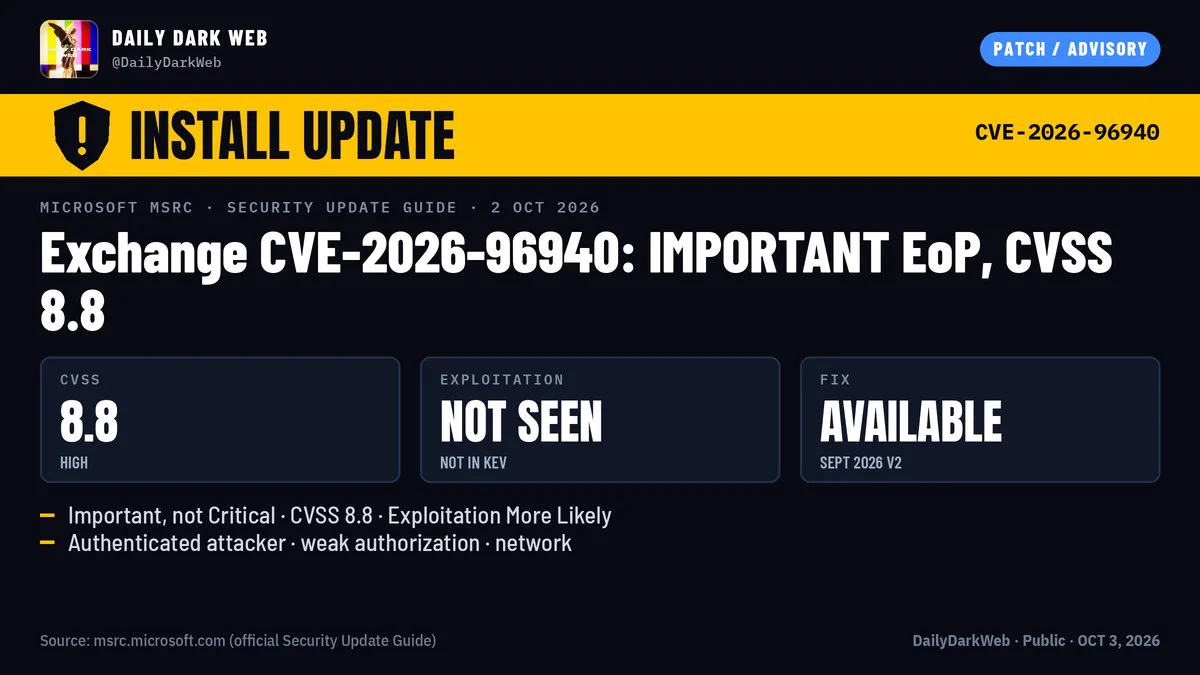
Microsoft released September 2026 V2 / October 2026 early Exchange Server security updates adding CVE-2026-96940.
• Important elevation of privilege, CVSS 8.8, Exploitation More Likely
• Weak authorization lets an authenticated attacker elevate privileges over the network
• On-prem: Exchange SE RTM (KB5129955); 2019 CU15/CU14 (KB5129956/KB5129957, Period 2 ESU); 2016 CU23 (KB5129958, Period 2 ESU)
• Exchange Online is already protected. Install on every on-prem Exchange server, including hybrid management
Microsoft found this internally and is not aware of exploitation. It is not in CISA KEV. It is Important, not Critical. An authenticated attacker is required.
#DDW #DarkWeb #Microsoft #Exchange #CyberSecurity #ThreatIntelligence"
🇺🇸🚨 MICROSOFT EXCHANGE CVE-2026-96940 — IMPORTANT EOP IN SEPT 2026 V2 SU
Microsoft released September 2026 V2 / October 2026 early Exchange Server security updates adding CVE-2026-96940.
• Important elevation of privilege, CVSS 8.8, Exploitation More Likely
• Weak authorization lets an authenticated attacker elevate privileges over the network
• On-prem: Exchange SE RTM (KB5129955); 2019 CU15/CU14 (KB5129956/KB5129957, Period 2 ESU); 2016 CU23 (KB5129958, Period 2 ESU)
• Exchange Online is already protected. Install on every on-prem Exchange server, including hybrid management
Microsoft found this internally and is not aware of exploitation. It is not in CISA KEV. It is Important, not Critical. An authenticated attacker is required.
[.]com/update-guide/en-US/vulnerability/CVE-2026-96940
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
