Skip to content
Product
Threat intelligence API
Free key, 70+ endpoints, OpenAPI. The product.
Get started
Pick your stack, make your first call.
Live feed
The console: incidents, filters, entities, search.
Public IOC feed
Free blocklists: domains, IPs, hashes, wallets. No key.
Dark web
First-party leak-site collection: victims and groups.
CLI & agents
tc from a terminal; agent keys with scoped budgets.
Docs
Pricing
No results found
Sign in
Get a free key
No results found
Product
Threat intelligence API
Get started
Live feed
Public IOC feed
Dark web
CLI & agents
Docs
Pricing
Contact
Get a free key
Sign in
Back
Plugin4Shell
Vulnerability
Threat entity extracted from intelligence sources
Entities
›
vulnerability
›
Plugin4Shell
Frequency
8
occurrences
First Seen
September 17, 2026
Last Seen
September 23, 2026
API
Overview
Recent Events
Profile
Profile
MITRE ATT&CK
1 / 2
Exploited By
Clop
Conti
Associated Malware
RatHat
Tools Used
BitBucket
Git
Claude Code
Codex
Gemini CLI
GitHub Copilot
Anthropic Claude Code
OpenAI Codex
Related CVEs
CVE-2026-76460
MITRE Techniques
T1195 - Supply Chain Compromise
T1059 - Command and Scripting Interpreter
T1566.001 - Spearphishing Attachment
T1566.002 - Spearphishing Link
Campaigns
SkillJacking
RepoJacking
MCPjacking
Affected Platforms
GitHub
Air Filter
Air Marketplace
Antigravity
Copilot
Google Gemini CLI
Regions
Switzerland
United Kingdom
United States
Australia
Canada
Sectors Affected
Financial
Healthcare
-
REC
Recon
No techniques detected
-
RD
Resource Dev
No techniques detected
1
IA
Initial Access
T1566.001 - Spearphishing Attachment
1
EX
Execution
T1059 - Command and Scripting Interpreter
-
PE
Persistence
No techniques detected
-
PE
Priv Esc
No techniques detected
-
DE
Defense Evasion
No techniques detected
-
CA
Cred Access
No techniques detected
-
DI
Discovery
No techniques detected
-
LM
Lateral Mov
No techniques detected
-
CO
Collection
No techniques detected
-
C2
C2
No techniques detected
-
EX
Exfil
No techniques detected
-
IM
Impact
No techniques detected
3
techniques detected across
2
tactics
Related Clusters (1)
Plugin4Shell: Zero-Click RCE Vulnerability in Major AI Coding Agents
Sep 17
·
14 sources
73
Related Articles (8)
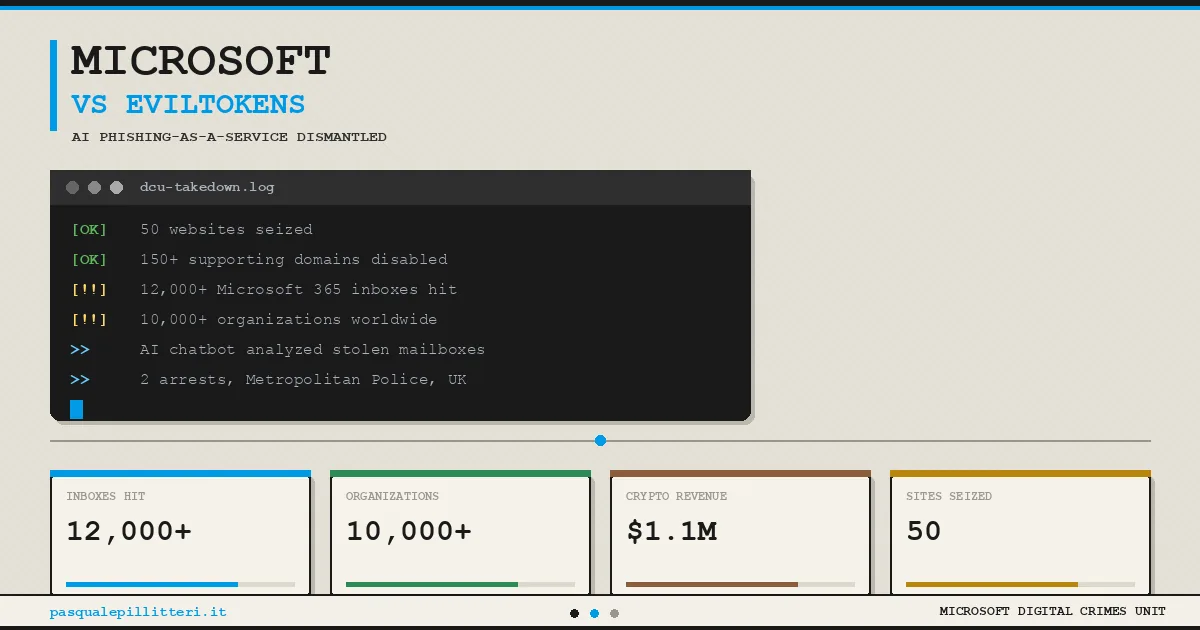
Microsoft dismantles EvilTokens, the AI phishing service that hit 12,000 inboxes
Pasqualepillitteri.It
·
Sep 23
Plugin4Shell Flaw Lets Repo Owners Bypass Version Locks in Four AI Coding Agents
Finance.Biggo
·
Sep 18
Zero-click RCE flaw in AI coding agents let attackers swap in malicious plugins
Daily.Dev
·
Sep 18
A zero
Csoonline
·
Sep 18
Plugin4Shell Bypasses SHA Pinning Across All Four Major AI Coding Agents
Tech.Yahoo
·
Sep 18
Zero-click RCE vulnerability hit four major AI coding agents, two remain unpatched
Helpnetsecurity
·
Sep 18
AI coding agents' 0
Theregister
·
Sep 17
Plugin4Shell
News.Ycombinator
·
Sep 17
Prev
1 / 2
Next
Related Entities
Supply Chain Attack
Phishing
Malware
Zero-day Exploit
SkillJacking
RepoJacking
MCPjacking
Anthropic
Google
Microsoft
OpenAI
Switzerland