Skip to content
Product
Use it
Threat intelligence API
Free key, 70+ endpoints, OpenAPI. The product.
Get started
Pick your stack, make your first call.
Live feed
The console: incidents, filters, entities, search.
Recipes
Runnable examples for the free key.
Free feeds
RSS, ransomware feed, IOC blocklist, MISP — no key.
CLI & agents
tc from a terminal; agent keys with scoped budgets.
The data
Incident records
900 articles a day become ~70 scored incidents.
Dark web
First-party leak-site collection: victims, groups, markets.
Validated IOCs
Indicators with a false-positive gate; STIX, MISP, CSV.
Vulnerabilities
CVEs with EPSS, KEV and exploit status.
Entity graph
Actors, malware, CVEs, companies — pivotable.
For teams
For service providers
Per-client feeds, alerts and branded digests.
Use cases
How teams and builders use the corpus.
About ThreatCluster
What it is and how it is built.
Pricing
Docs
Reference
OpenAPI (Swagger)
Every endpoint, parameter and response model.
ReDoc
The same reference, long-form.
Examples on GitHub
curl, Python and Node quickstarts; daily spec snapshot.
Guides
Quickstart & plans
Key, scopes, budgets, tiers.
Integrations
Splunk, Sentinel, Elastic, agents and terminals, step by step
Export formats
STIX 2.1, MISP, CSV, text.
CLI setup
Install, log in, wire an agent.
No results found
Sign in
Get a free key
No results found
Product
Threat intelligence API
Get started
Live feed
Recipes
Free feeds
CLI & agents
The data
Incident records
Dark web
Validated IOCs
Vulnerabilities
Entity graph
For teams
For service providers
Use cases
About ThreatCluster
Docs
OpenAPI (Swagger)
ReDoc
Examples on GitHub
Quickstart & plans
Integrations
Export formats
CLI setup
Pricing
Contact
Get a free key
Sign in
Back
Stm32 Entropy Vulnerability
Vulnerability
Threat entity extracted from intelligence sources
Entities
›
vulnerability
›
Stm32 Entropy Vulnerability
Frequency
19
occurrences
First Seen
September 9, 2026
Last Seen
September 11, 2026
API
Overview
Recent Events
Profile
Profile
MITRE ATT&CK
1 / 2
Tools Used
Sendinblue
MITRE Techniques
T1566.002 - Spearphishing Link
T1566 - Phishing
T1041 - Exfiltration Over C2 Channel
T1078 - Valid Accounts
T1110 - Brute Force
T1567 - Exfiltration Over Web Service
Affected Platforms
Stm32
Tropic01
Google Sites
Safepal
Regions
France
Paraguay
-
REC
Recon
No techniques detected
-
RD
Resource Dev
No techniques detected
2
IA
Initial Access
T1566.002 - Spearphishing Link
T1078 - Valid Accounts
-
EX
Execution
No techniques detected
-
PE
Persistence
No techniques detected
-
PE
Priv Esc
No techniques detected
-
DE
Defense Evasion
No techniques detected
1
CA
Cred Access
T1110 - Brute Force
-
DI
Discovery
No techniques detected
-
LM
Lateral Mov
No techniques detected
-
CO
Collection
No techniques detected
-
C2
C2
No techniques detected
2
EX
Exfil
T1041 - Exfiltration Over C2 Channel
T1567 - Exfiltration Over Web Service
-
IM
Impact
No techniques detected
5
techniques detected across
3
tactics
Related Clusters (3)
Trezor Data Breach Exposes 80,689 Customers to Phishing Risks
Sep 9
·
31 sources
70
Phishing Attack Targets 347K Trezor Users via Brevo Breach
Sep 10
·
15 sources
69
Phishing Attack Targets Trezor and BitBox Users via Compromised Email Provider
Sep 10
·
14 sources
68
Related Articles (19)
Trezor Says 347,000 Users Received Phishing Emails After Brevo Hack
Securityweek
·
Sep 11
Trezor phishing attack traced to Brevo login authorization flaw
Crypto.News
·
Sep 11
Security Incident At Brevo Our Third Party Email Provider
trezor.io
·
Sep 11
cointelegraph.com
cointelegraph.com
·
Sep 11
Brevo login flaw enabled phishing email targeting 347K Trezor subscribers
Cryptonews
·
Sep 11
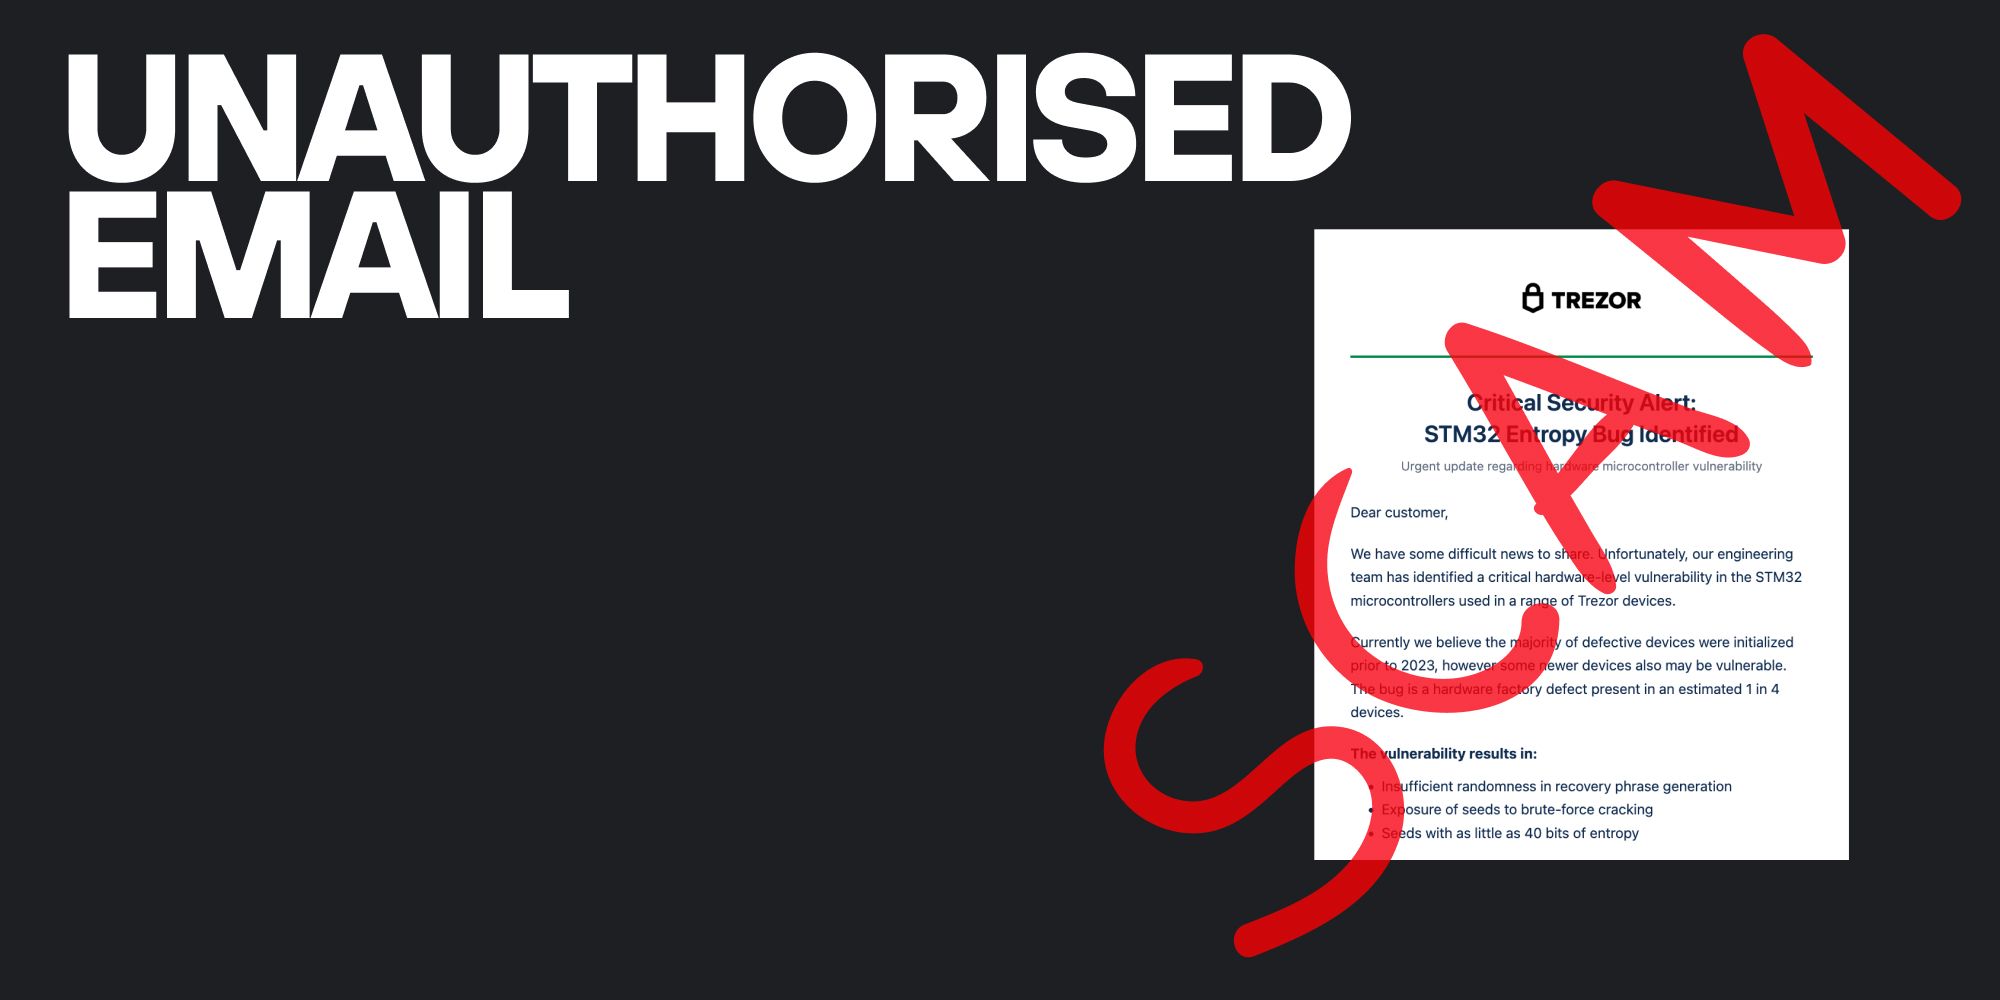
Trezor users targeted by phishing emails claiming an STM32 vulnerability
Kucoin
·
Sep 10
Trezor, BitBox Warn of Phishing Emails After Email Provider Breach
Altcoinbuzz
·
Sep 10
Multiple crypto companies warn customers of phishing emails after alleged provider breach
Therecord.Media
·
Sep 10
Decrypt of September 9, 2026
decrypt.co
·
Sep 10
Phishing Email From the Real Sender Address: How to Check a Wallet Security Warning
Cryptoticker
·
Sep 10
Read original article on U.Today
u.today
·
Sep 10
Trezor, BitBox users targeted in newsletter phishing spree
Theregister
·
Sep 10
Trezor Users Targeted by Terrifying Phishing Attack After Third-Party Breach
Tradingview
·
Sep 10
Trezor Says Third
Unchainedcrypto
·
Sep 10
Trezor Phishing Attack Hits BitBox Too After Email Provider Breach
En.Cryptonomist.Ch
·
Sep 10
Fake Trezor Warning Claims 25% of Devices Are Vulnerable in Latest Phishing Campaign
Cryptopotato
·
Sep 10
Trezor, BitBox warn users about fake hardware wallet security alerts
Tradingview
·
Sep 10
Trezor Warns Users of Phishing Emails After Third
Finance.Biggo
·
Sep 10
Trezor Warns of Email Provider Breach as Phishing Attacks Escalate Across Crypto
Glitchwire
·
Sep 9
Prev
1 / 4
Next
Related Entities
Phishing
Data Breach
Zero-day Exploit
Trezor
BitBox
ShipMonk
Brevo
CoinTracking
Casa
Coldcard
Coinkite
Foundation