Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
The Akira ransomware group has been identified as a significant threat to critical infrastructure, with the U.S. Cybersecurity and Infrastructure Security Agency (CISA) and the FBI warning of its active ransomware attacks. Since its emergence in March 2023, Akira has exploited vulnerabilities in edg...
A Russian-speaking threat actor has exploited vulnerabilities CVE-2026-81578 and CVE-2026-82078 in PaperCut NG/MF software, compromising at least 440 instances across 395 organizations in 48 countries. The campaign began on August 31, 2026, utilizing hundreds of AI agents powered by OpenAI's Codex a...
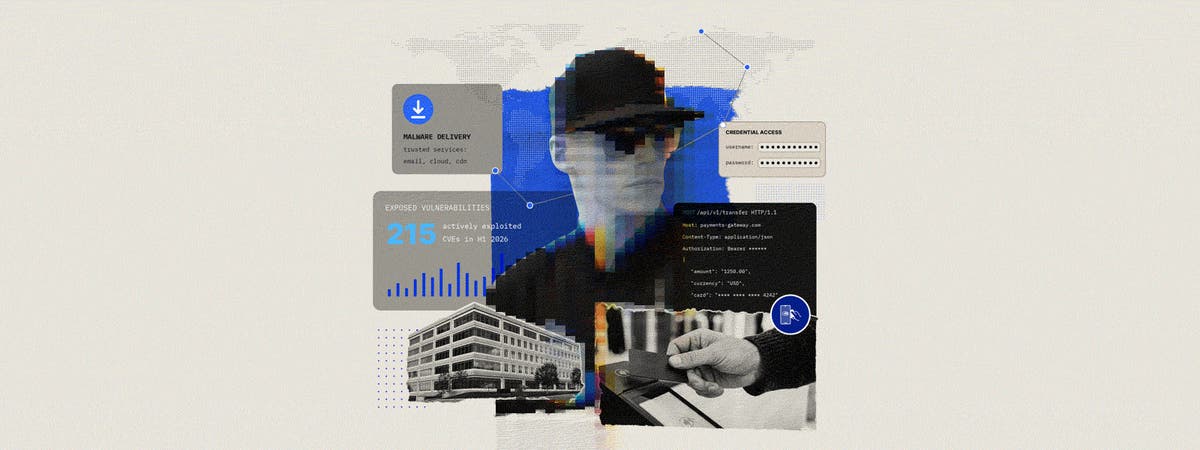
The FBI, CISA, and U.S. Secret Service issued a joint advisory on October 20, 2026, revealing that the SafePay ransomware group has compromised at least 600 organizations across critical infrastructure sectors since August 2024. The group employs various attack vectors, including stolen credentials,...
Ransomware groups, including Qilin and INC, are exploiting a critical authentication bypass vulnerability (CVE-2026-0257) in Palo Alto Networks' PAN-OS GlobalProtect and Prisma Access. This flaw allows attackers to establish unauthorized VPN sessions, bypassing multifactor authentication controls. S...