 Cointelegraph
PHP Vulnerability Sparks Widespread Cybersecurity Concerns
Article Content

- •Critical PHP vulnerabilities could leave millions of websites exposed.
- •Experts warn of potential mass exploitation and advise caution for users.
- •Emergency patches have been released, but many sites may not update in time.
A critical PHP vulnerability has been disclosed, prompting warnings from cybersecurity experts about potential exploits. The PHP Foundation acknowledged a delay in addressing this flaw, which could leave numerous smaller websites vulnerable for weeks. Mitchell Amador, CEO of Immunefi, described the situation as a 'vulnerability apocalypse,' urging users to treat any site they log into as potentially compromised. The vulnerabilities allow attackers to execute code remotely, posing risks to sensitive data and networks. Millions of exploit attempts were reported within hours of the vulnerabilities being made public. The PHP vulnerabilities are particularly concerning as PHP powers approximately 69% of websites globally. The FBI's Cyber Division has also issued warnings regarding the potential for sensitive data compromise due to these flaws.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track CVE-2017-9841 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are the specific vulnerabilities in PHP?
How urgent is the need to patch these vulnerabilities?
What precautions should users take?
Continue Reading
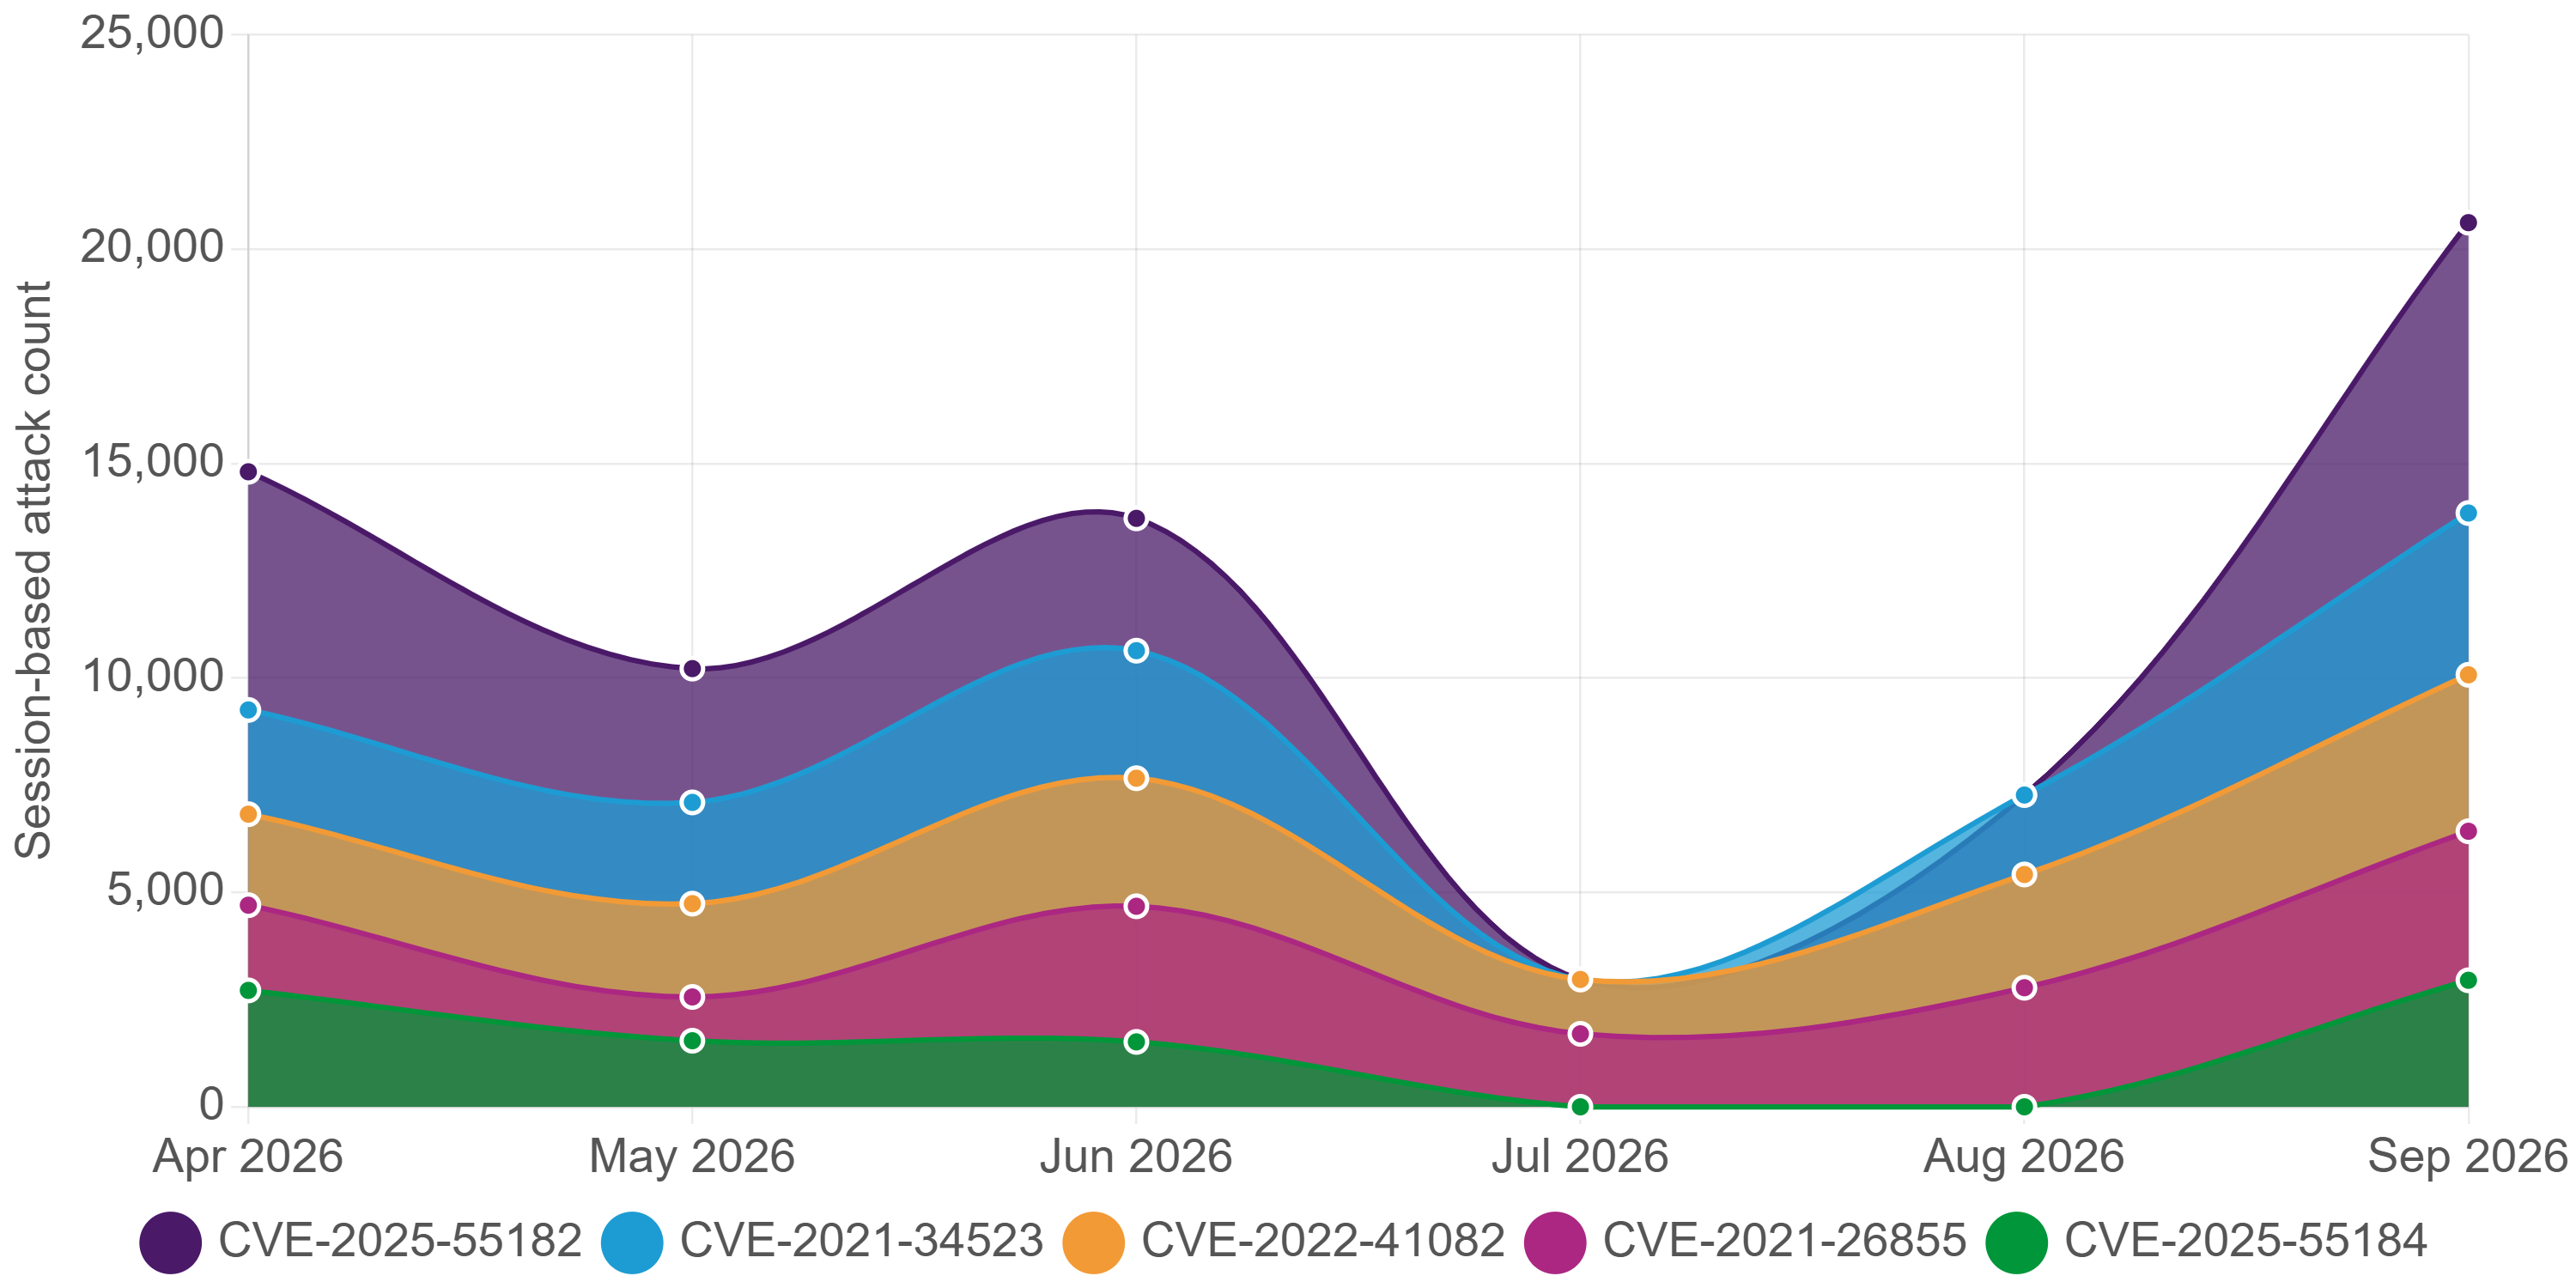 Langflow AI Platform Targeted by RCE Exploitation In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. The vulnerability…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…