Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
CyberXero, a Russian-speaking initial access broker, has launched a dual-pronged campaign targeting WordPress sites and Ukrainian critical infrastructure, leveraging AI tools like Claude Code. The operation has led to the exfiltration of over 628,000 records from Ukrainian entities, with confirmed c...
A coordinated supply chain attack has been identified, targeting vulnerability researchers and penetration testers through malicious proof-of-concept (PoC) repositories on GitHub. The malware, named ChocoPoC, is a Python-based remote access trojan (RAT) that stealthily exfiltrates sensitive data. At...
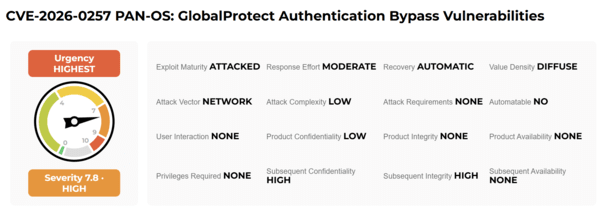
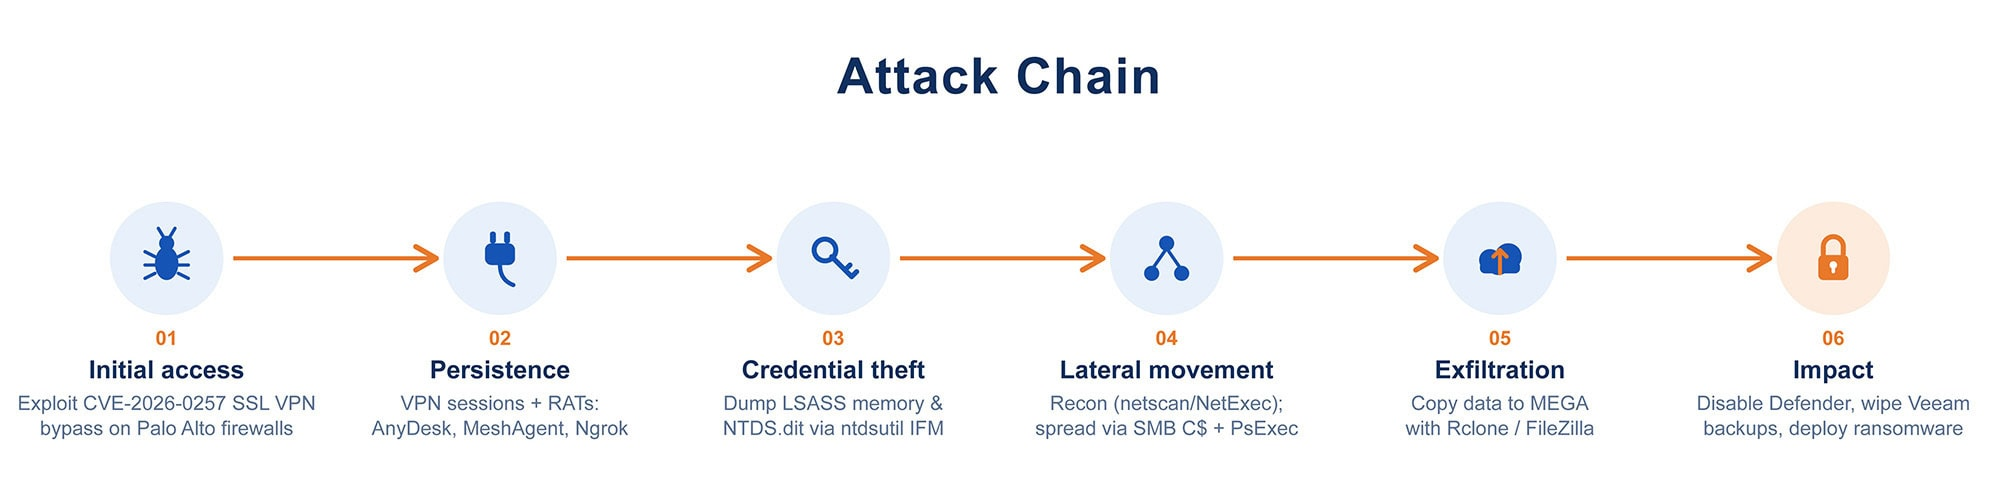
Ransomware groups, including Qilin and INC, are exploiting a critical authentication bypass vulnerability (CVE-2026-0257) in Palo Alto Networks' PAN-OS GlobalProtect and Prisma Access. This flaw allows attackers to establish unauthorized VPN sessions, bypassing multifactor authentication controls. S...
Ransomware groups Qilin and INC are exploiting CVE-2026-0257, a vulnerability in Palo Alto Networks' PAN-OS GlobalProtect VPN, to bypass authentication and gain unauthorized access to corporate networks. Despite a security patch released in May 2026, attackers have been exploiting this flaw since Ju...