 Recordedfuture
New GhostFrame Implant Targets ESXi Hosts Linked to Settra Ransomware
Article Content

- •GhostFrame allows centralized control over compromised ESXi hosts.
- •Recent ransomware incidents exploited misconfigurations and weak access controls.
- •Insikt Group links GhostFrame to TAG-218 and Settra ransomware.
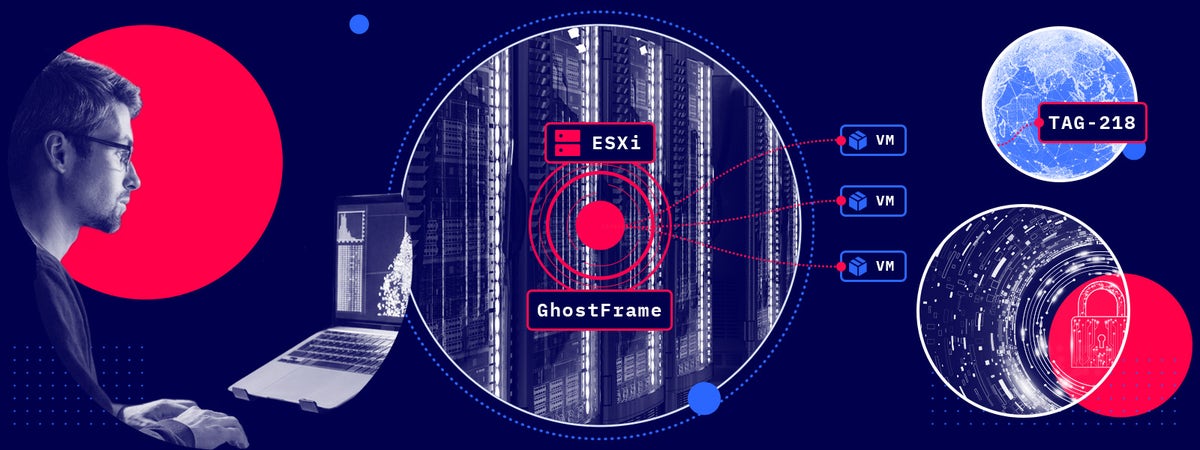
GhostFrame is a newly identified post-exploitation framework that allows attackers to control VMware ESXi environments after gaining root access. It enables extensive interaction with multiple virtual machines from a single interface, facilitating credential harvesting and deeper network penetration. The Insikt Group linked GhostFrame to TAG-218, a threat actor group associated with Settra ransomware. The framework does not exploit vulnerabilities to gain access but requires root-level access to deploy its implant. Kaspersky GERT reported recent ransomware incidents in ESXi and Proxmox environments, highlighting the risks of misconfigurations and weak access controls. These incidents emphasize the need for secure configurations and monitoring of virtualization infrastructures. The discovery of GhostFrame underscores the critical nature of protecting hypervisors as high-value targets.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track The Gentlemen, GhostFrame and CVE-2024-21626 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is GhostFrame?
How does GhostFrame operate?
What should organizations do to protect against these threats?
Continue Reading
 Hackers Exploit Firewalls, Compromise 70,000 Credentials Globally A large-scale cyber campaign has targeted exposed network edge devices, specifically Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls, leading to the compromise of over 70,000 credentials. The threat actor, known as k0t, has been active since October 2025 and is linked to ransomware groups like Qilin…
 Ransomware Groups Exploit PAN-OS Flaw, Target Critical Infrastructure Ransomware groups, including Qilin and INC, are exploiting a critical authentication bypass vulnerability (CVE-2026-0257) in Palo Alto Networks' PAN-OS GlobalProtect and Prisma Access. This flaw allows attackers to establish unauthorized VPN sessions, bypassing multifactor authentication controls. Since its disclosure…