Frequency
2
occurrences
First Seen
October 20, 2026
Last Seen
October 21, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
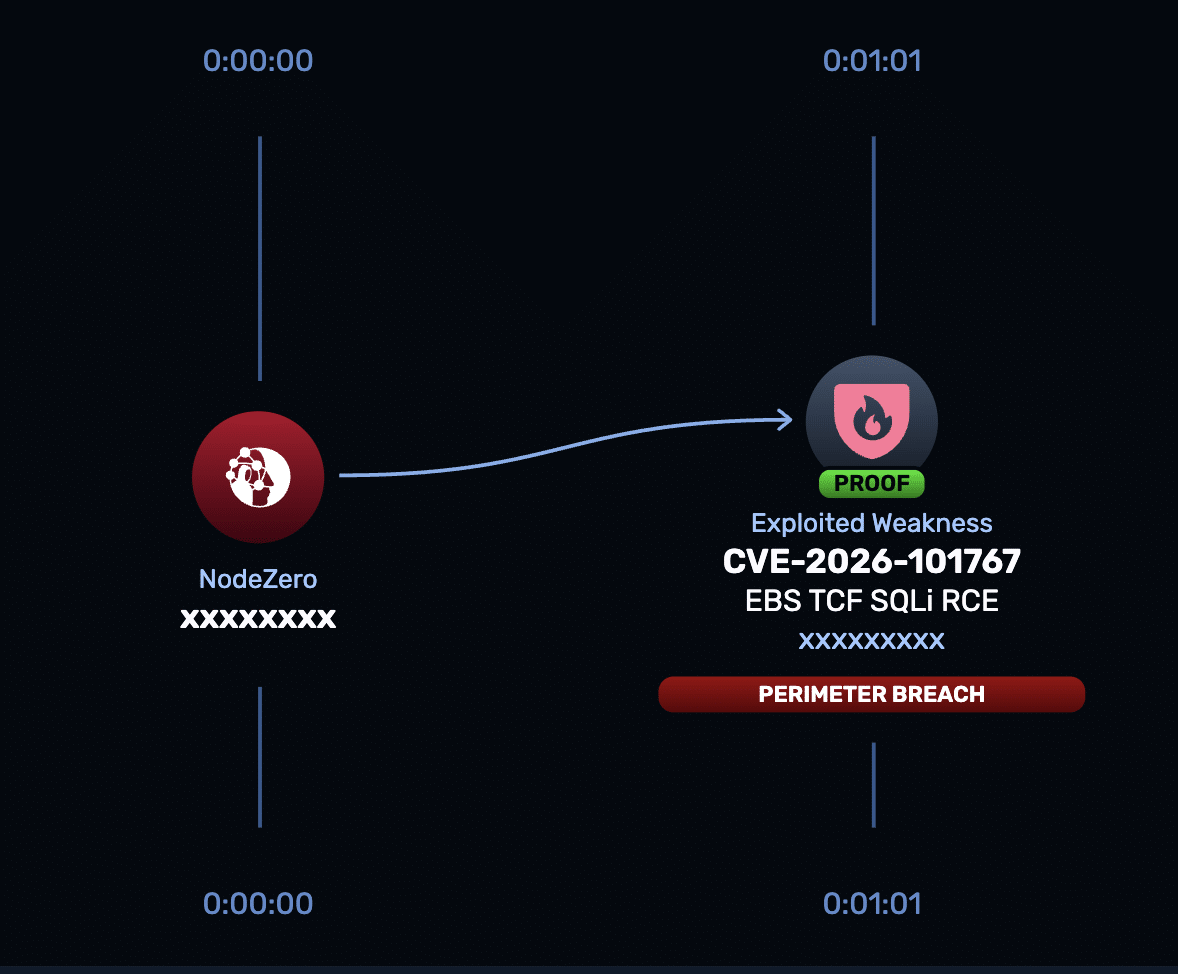
Oracle has addressed CVE-2026-101767, a critical unauthenticated SQL injection vulnerability in the Oracle Application Object Library of Oracle E-Business Suite (EBS). The flaw, rated CVSS 3.1 9.8 (Critical), allows attackers with network access to exploit the EBS Thin Client Framework (TCF) servlet...
Public Exploits
Checking GitHub for proof-of-concept code…