Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Cisco has disclosed a critical authentication bypass vulnerability, CVE-2026-20182, affecting its Catalyst SD-WAN Controller and Manager. This flaw allows unauthenticated remote attackers to bypass authentication and gain administrative privileges, enabling manipulation of network configurations. Th...
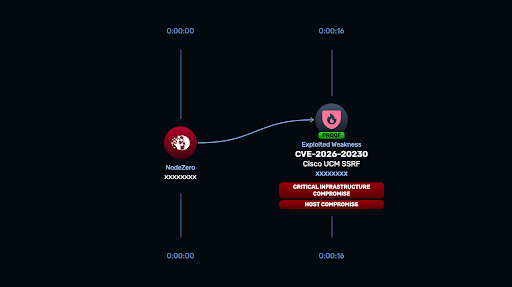
Active exploitation of two critical vulnerabilities has been reported: CVE-2026-20230 in Cisco Unified CM and CVE-2026-20971 in Samsung KNOX. The Cisco flaw, a server-side request forgery (SSRF), poses an immediate threat to organizations using the Unified Communications Manager Server. Meanwhile, t...
Cisco has confirmed that attackers are exploiting a vulnerability in its Unified Communications Manager (Unified CM), tracked as CVE-2026-20230, which was patched on June 3, 2026. This vulnerability allows for server-side request forgery (SSRF) attacks through improperly validated HTTP requests, pot...
Cisco disclosed a critical server-side request forgery (SSRF) vulnerability in its Unified Communications Manager (CVE-2026-20230) on June 3, 2026. This flaw allows attackers with network access to write arbitrary files to the operating system, potentially escalating privileges to root. A proof-of-c...