Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
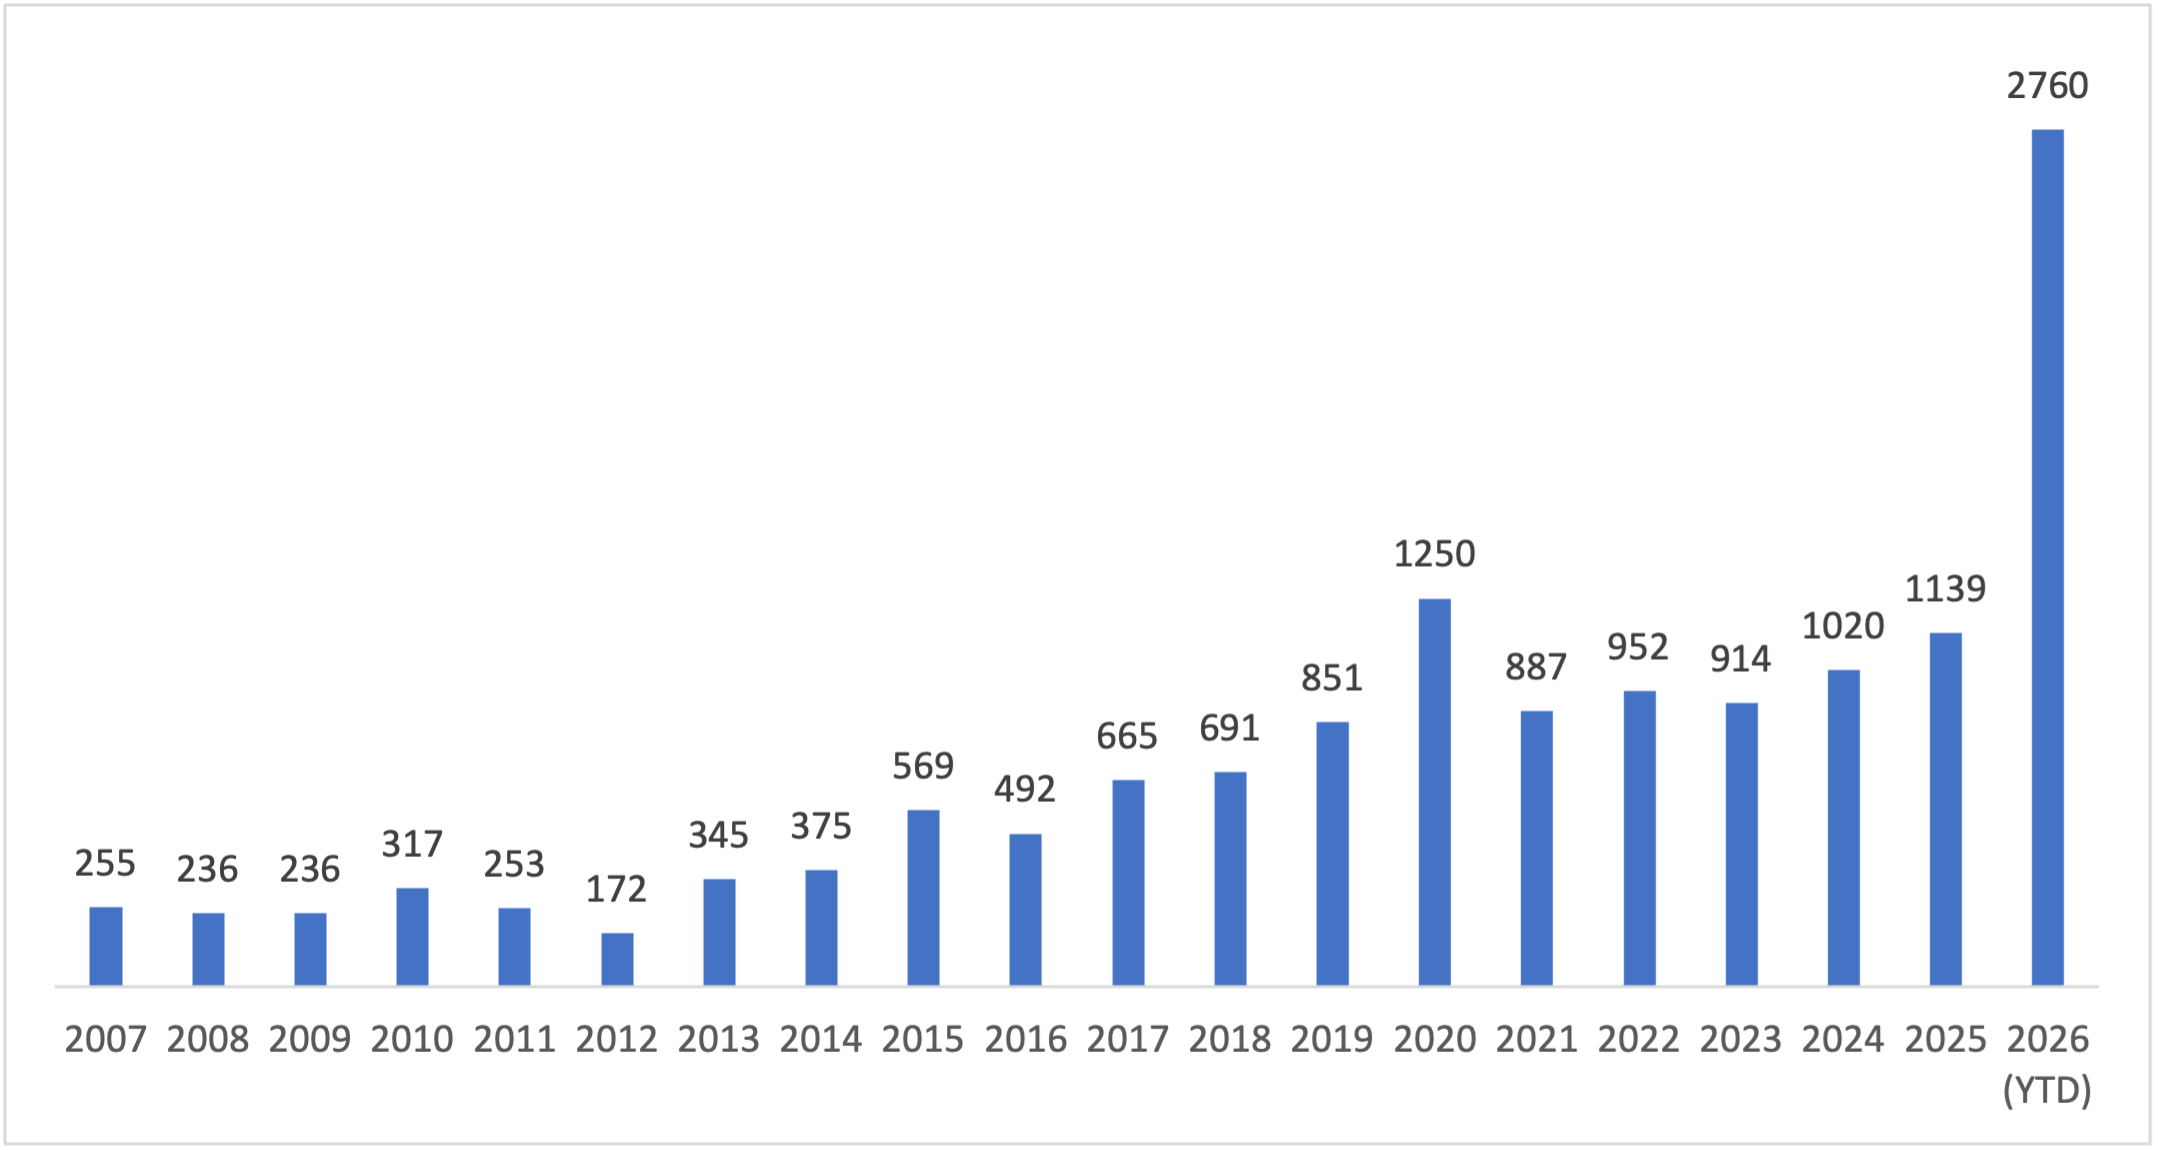
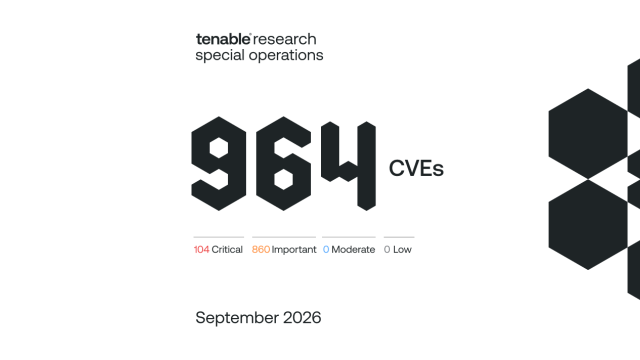
A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLa...
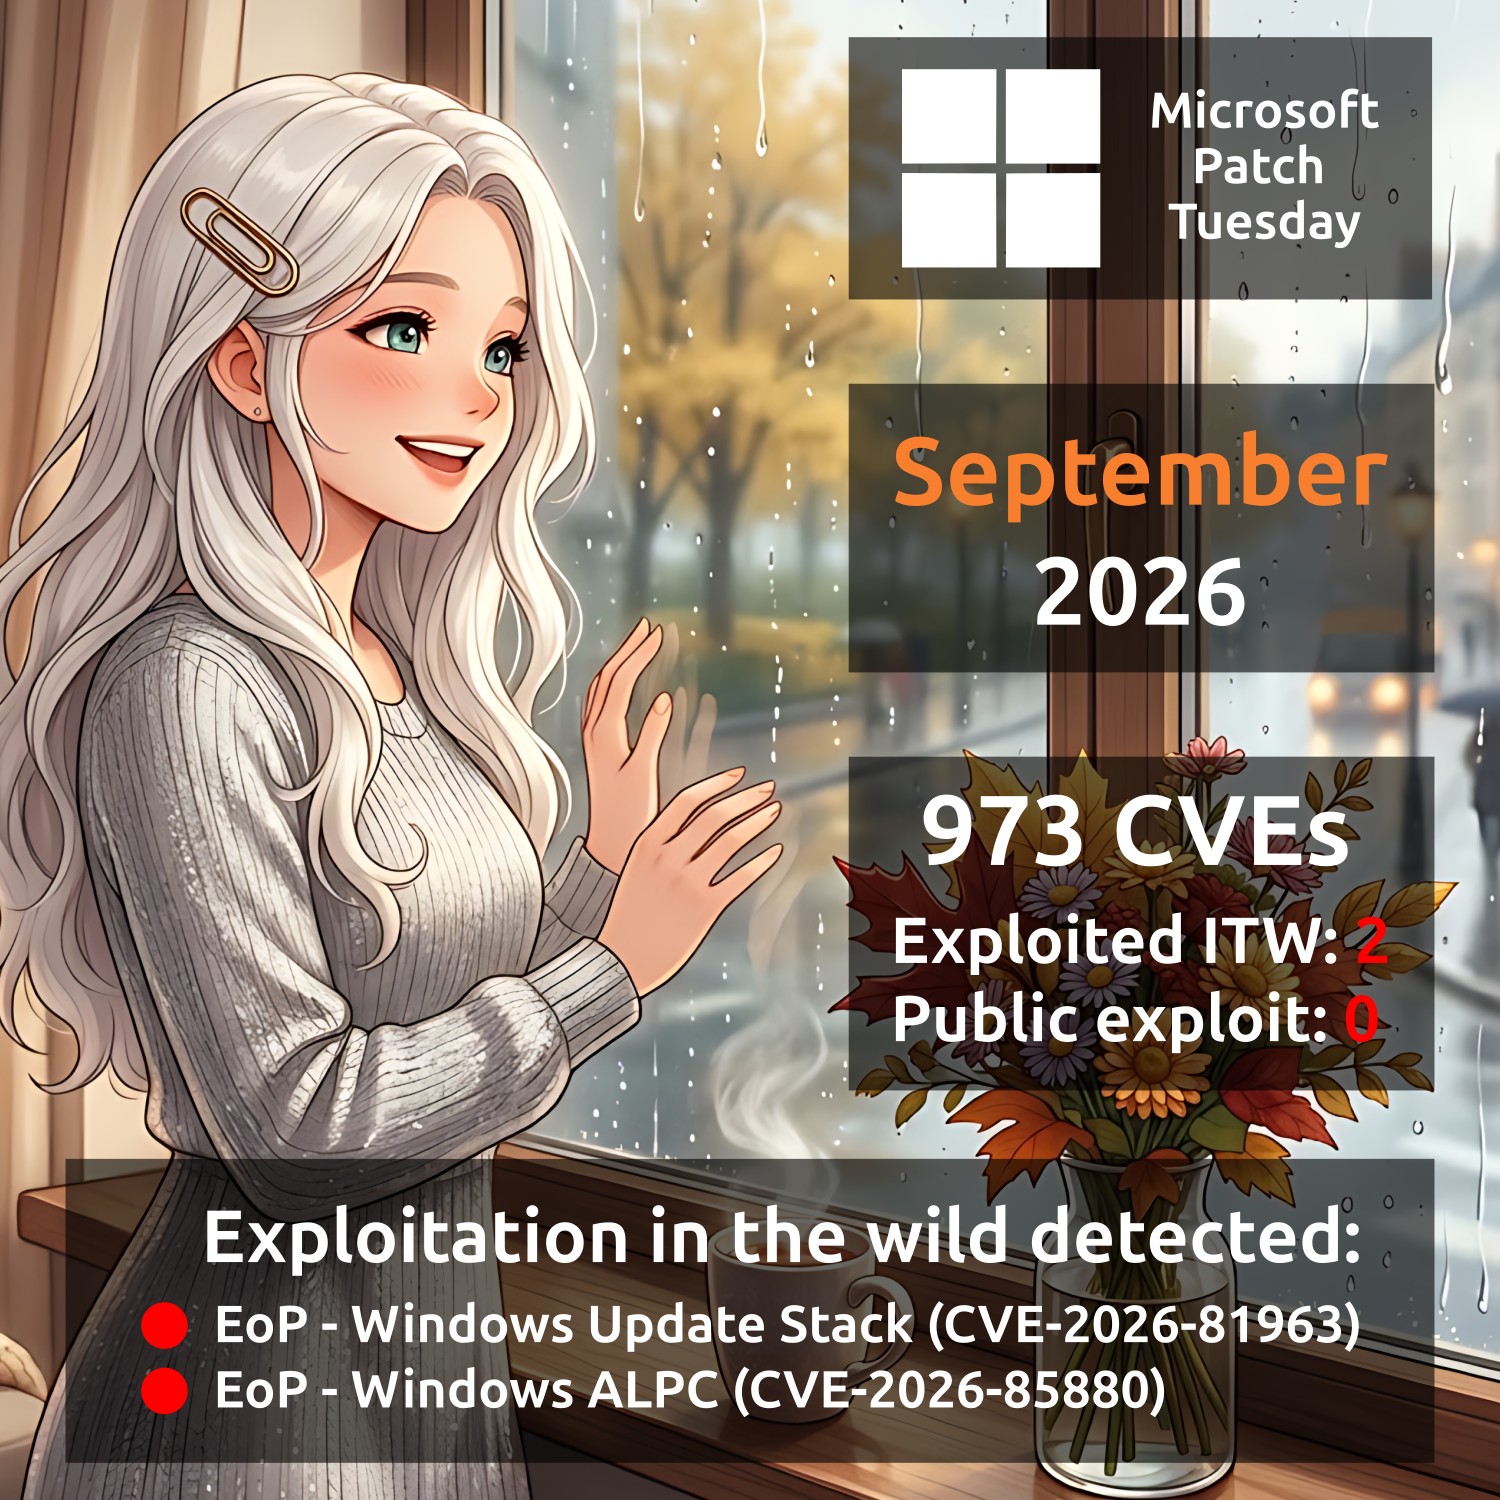
On September 8, 2026, Microsoft released a security update addressing critical vulnerabilities in its products, notably CVE-2026-85880 and CVE-2026-81963, both of which were confirmed to be actively exploited before the update was issued. The vulnerabilities involve privilege escalation in Windows A...
In September 2026, several critical vulnerabilities were disclosed, notably CVE-2026-81963 and CVE-2026-85880, both of which are actively exploited. CVE-2026-81963, affecting Windows Update Stack, allows local privilege escalation without user interaction. CVE-2026-85880, a heap-based buffer overflo...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added several vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in Microsoft Windows, Adobe, N-able, Cisco, Google Chromium, Fortinet, and Citrix. Notably, CVE-2026-75650, a critical Ado...