 Computerweekly
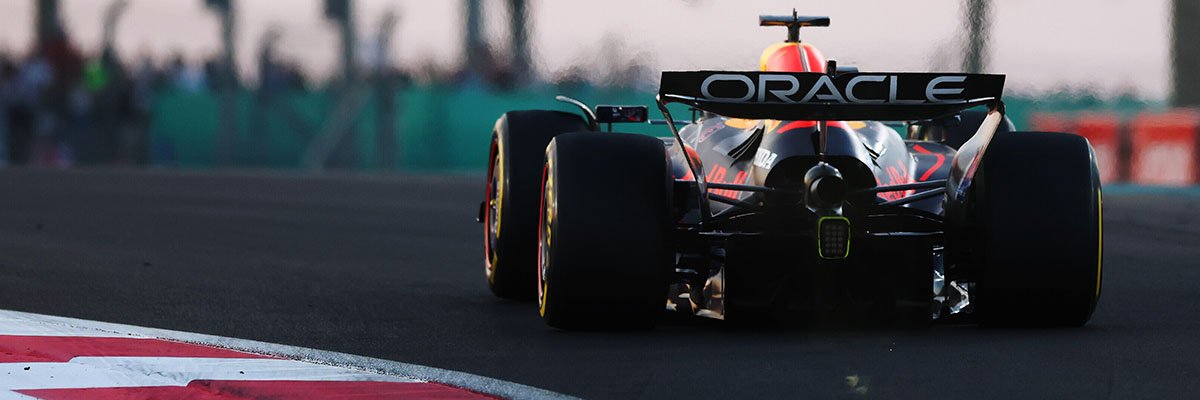
Oracle Red Bull Racing Enhances Security with IAM Tools Amid F1 Challenges
Article Content

- •Oracle Red Bull Racing reduced wind tunnel recovery time by 97% using 1Password IAM tools.
- •The team faces challenges from new F1 regulations requiring a complete car redesign.
- •Cybersecurity is critical for protecting sensitive data and ensuring operational continuity.
Oracle Red Bull Racing has implemented identity and access management (IAM) tools from 1Password to streamline operations and enhance security in the face of stringent Formula 1 regulations. The team has experienced significant improvements, notably reducing wind tunnel recovery time from one hour to just two minutes, a 97% decrease. This efficiency is crucial as the team navigates a challenging season with a complete redesign of their cars due to new regulations. The CIO, Matt Cadieux, emphasizes the importance of cybersecurity in protecting sensitive information and maintaining business continuity. The team manages a complex IT infrastructure with thousands of servers and service accounts, making security a top priority. Despite some initial implementation challenges, the automation provided by 1Password has led to faster processes that contribute to car development. The focus remains on minimizing downtime and maximizing productivity for engineers and technicians.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…