 Geo.Tv
Pakistan Launches Cybercrime Probe into Cambridge Exam Paper Leaks
Article Content

- •The NCCIA is investigating multiple alleged leaks of Cambridge exam papers in Pakistan.
- •Cambridge confirmed the leak of an AS-Level Mathematics paper and postponed another scheduled exam.
- •The investigation involves high-level officials and aims to enhance examination security.
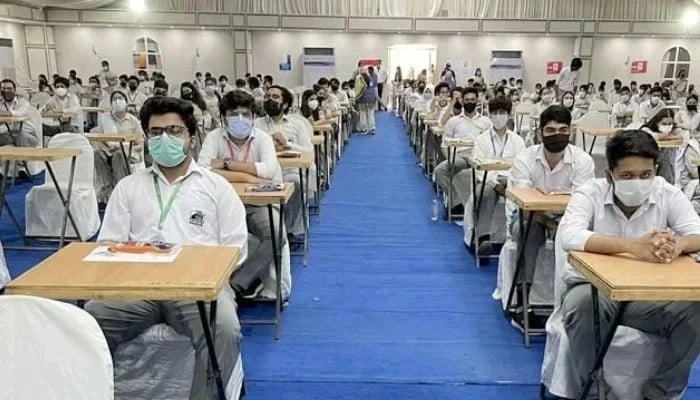
The Pakistani Interior Ministry has ordered the National Cyber Crime Investigation Agency (NCCIA) to investigate the alleged leakage of Cambridge examination papers, particularly concerning A-Level and O-Level Mathematics papers. This decision follows the confirmation by Cambridge International Education (CIE) of multiple leaks, including an AS-Level Mathematics paper that circulated online prior to the exam. The investigation aims to assess the extent of these breaches and improve security measures. A high-level meeting was convened with key officials from the education sector and representatives from CIE, where concerns were raised about the integrity of the examination process. The British deputy high commissioner indicated that the situation may involve theft rather than a straightforward leak. Cambridge has committed to strengthening its examination systems to prevent future incidents. The ongoing May-June examination session has been impacted, with the postponement of certain papers due to these leaks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (11)
Following this threat?
Track British Council in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Critical SQL Injection Zero-Day in Arista VeloCloud Orchestrator Exploited Arista Networks has patched a critical zero-day vulnerability (CVE-2026-114625) in its VeloCloud Orchestrator (VCO) that is actively being exploited. The flaw allows authenticated users, even those with basic privileges, to escalate their access to superuser status via a low-complexity SQL injection attack. This…