Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control...
On September 26, 2026, security firm watchTowr reported two unpatched zero-day vulnerabilities in Citrix NetScaler ADC and Gateway appliances, allowing remote code execution (RCE) and actively exploited in the wild. Citrix has confirmed the existence of these vulnerabilities, tracked as CVE-2026-887...
In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabi...
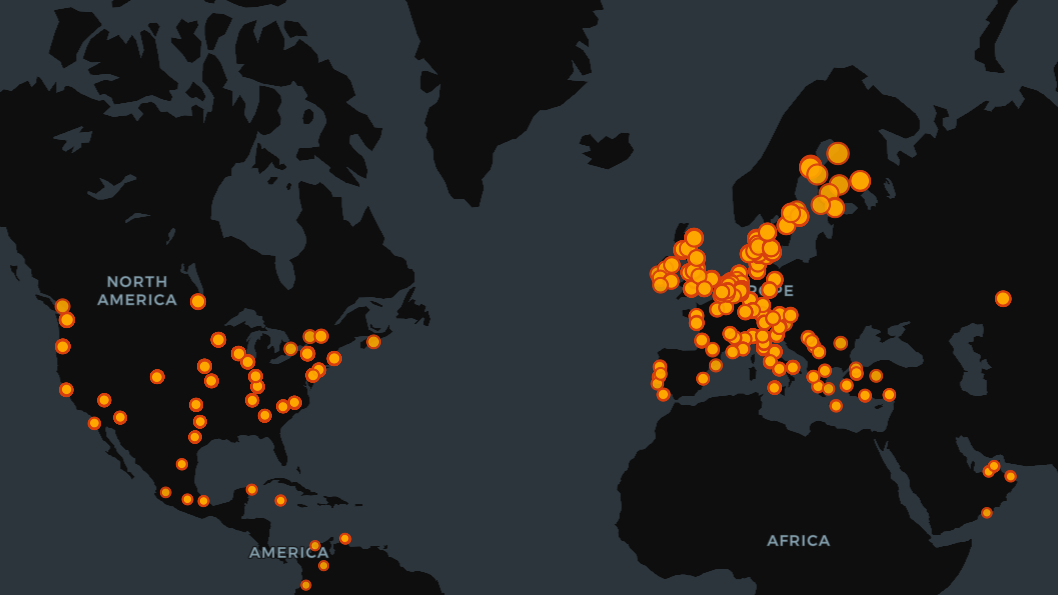
CVE-2025-5777, known as CitrixBleed-2, is a critical unauthenticated out-of-bounds read vulnerability in Citrix NetScaler ADC and Gateway products. Disclosed on June 17, 2025, it allows attackers to leak sensitive memory data, including session tokens, via a single crafted HTTP request. Affected ver...
Public Exploits
Related Clusters (6)