Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
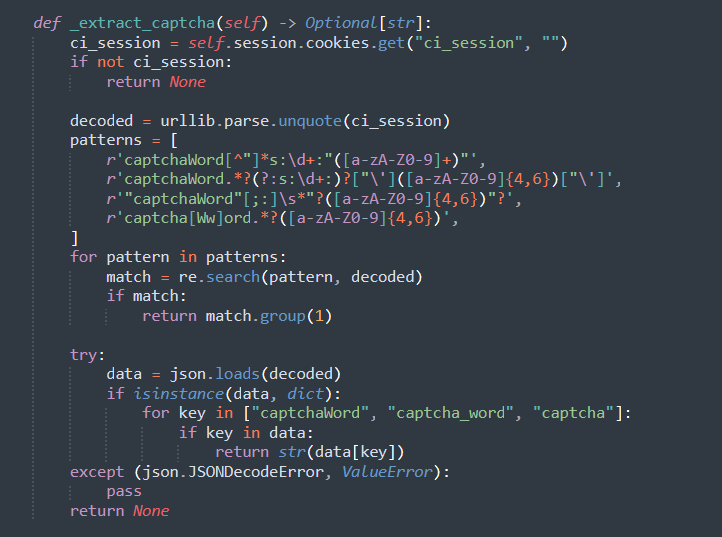
A sophisticated cyber campaign has exploited a critical cPanel vulnerability (CVE-2026-41940) to breach government and military servers in Southeast Asia, particularly targeting Indonesia. The attackers utilized a custom zero-day exploit chain to access sensitive information, exfiltrating over 4GB o...
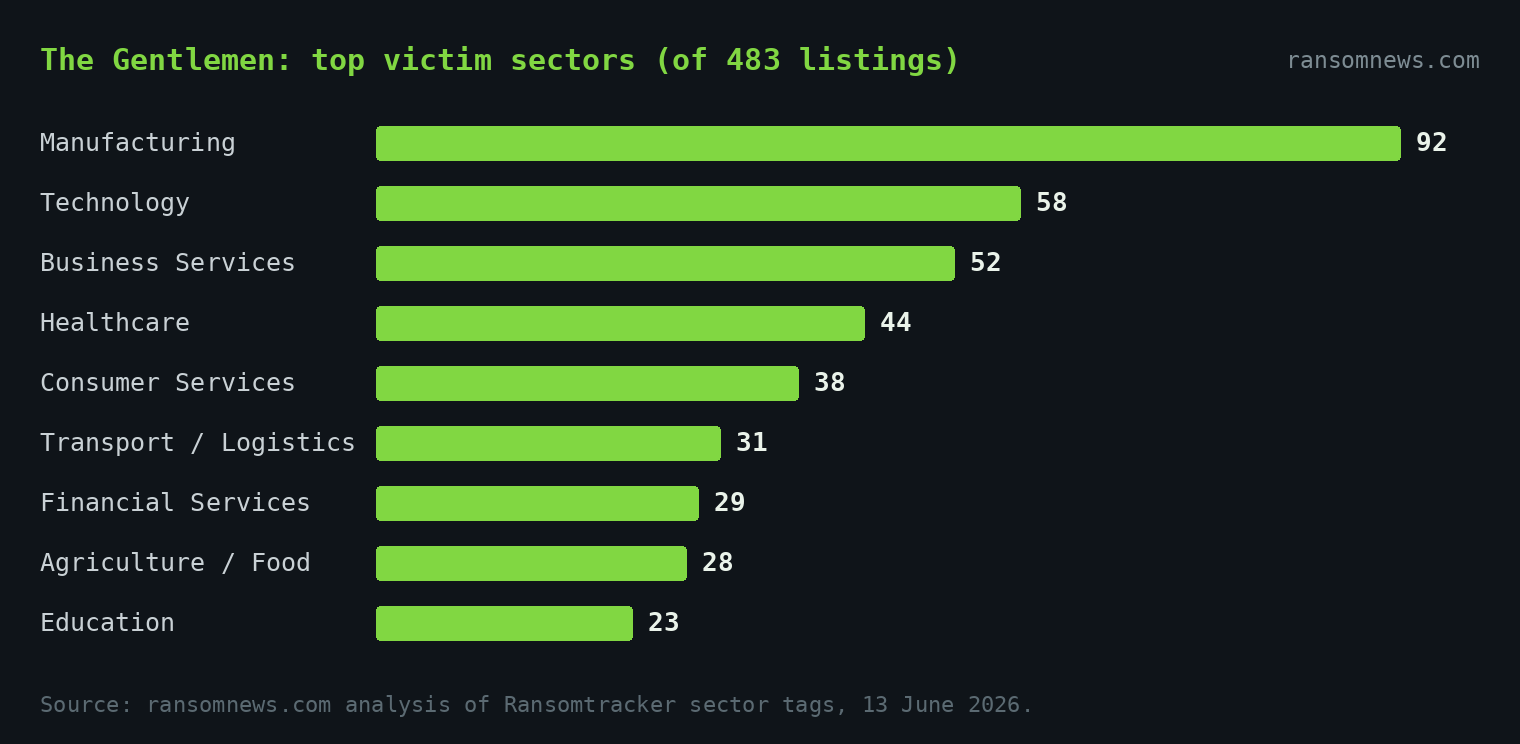
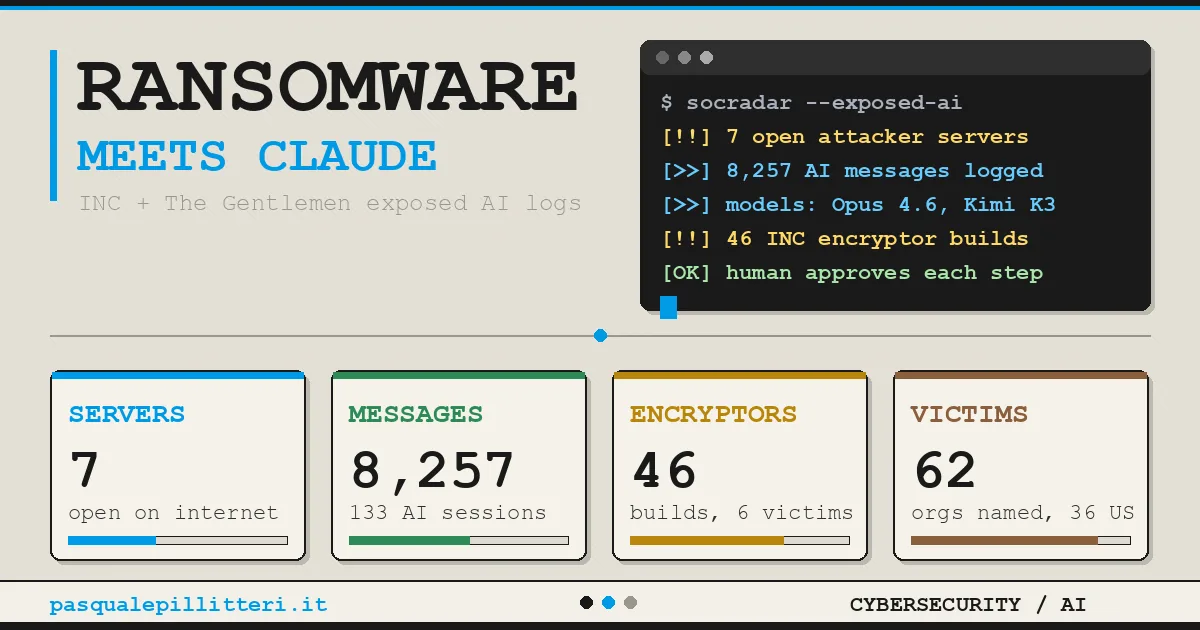
Cybersecurity researchers have uncovered an AI-assisted ransomware operation linked to the INC and The Gentlemen groups. The exposed infrastructure includes seven servers used for orchestrating attacks on 62 organizations, with over $23,920 spent on AI services. The operation employs an 'Autonomous...
Ransomware groups, including Qilin and INC, are exploiting a critical authentication bypass vulnerability (CVE-2026-0257) in Palo Alto Networks' PAN-OS GlobalProtect and Prisma Access. This flaw allows attackers to establish unauthorized VPN sessions, bypassing multifactor authentication controls. S...
Threat actors exploited CVE-2026-41940, a critical authentication bypass in cPanel and WHM, allowing remote, unauthenticated access to hosting servers. The vulnerability, with a CVSS score of 9.8, affects cPanel versions released after 11.40. Following the public disclosure on April 29, 2026, exploi...