Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
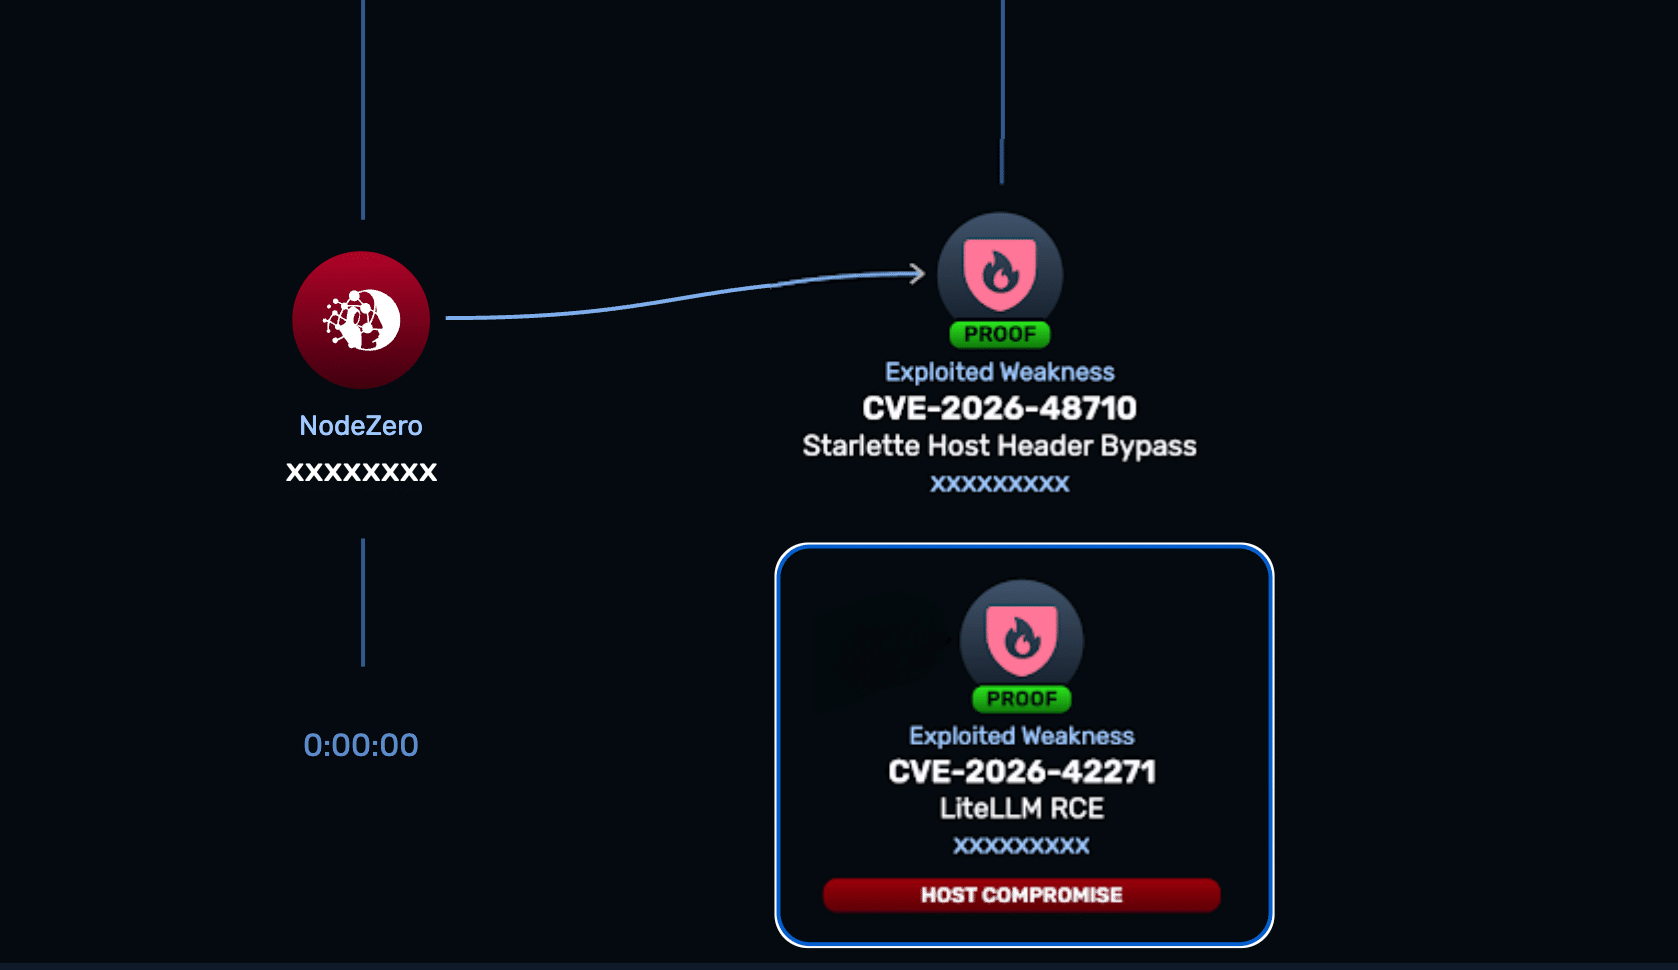
A critical command injection vulnerability, CVE-2026-42271, in LiteLLM, an open-source AI gateway, allows unauthenticated remote code execution (RCE) when chained with CVE-2026-48710, a Host header validation bypass in Starlette. This exploit affects LiteLLM versions 1.74.2 to 1.83.6, with the U.S....
SonicWall disclosed two critical vulnerabilities in its SMA1000 series appliances, CVE-2026-83548 and CVE-2026-83549, which are being actively exploited. CVE-2026-83548 is a pre-authentication server-side request forgery (SSRF) vulnerability rated 10.0 on the CVSS scale, allowing unauthenticated att...
CISA has added seven new vulnerabilities to its Known Exploited Vulnerabilities Catalog, including CVE-2026-9586, a SQL injection vulnerability in Sangoma Switchvox, and several others affecting SonicWall and JFrog products. These vulnerabilities pose significant risks due to active exploitation. Co...
A critical security vulnerability, CVE-2026-48710, has been identified in Python-Starlette, affecting Fedora 43 and 44. The flaw allows a security restriction bypass via a malformed HTTP Host header. Systems running these versions are at risk, as the vulnerability could enable unauthorized access. T...