 Bleepingcomputer
Veeam Backup & Replication Vulnerabilities Enable RCE Attacks
Article Content
Browse articles 
Veeam has issued security updates to address multiple vulnerabilities in its Backup & Replication software, including a critical remote code execution (RCE) flaw tracked as CVE-2025-59470. This vulnerability affects Veeam Backup & Replication version 13.0.1.180 and earlier, allowing Backup or Tape Operators to execute code remotely as the postgres user. A separate RCE vulnerability was also noted, allowing execution as root through a malicious backup configuration file.
Ask AI about this cluster
Answers cite the sources they use
Updated 226d ago How this analysis works
More articles in this cluster (7)
Following this threat?
Track Akira and CVE-2024-40711 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Attackers Exploit MFA Gaps in SonicWall VPN Access On August 4, 2026, an Akira ransomware affiliate successfully accessed a SonicWall SSL VPN by spraying passwords, exploiting the lack of multi-factor authentication (MFA). After gaining access, the attacker used RDP to reach the domain controller and enumerate Active Directory, although the ransomware deployment…
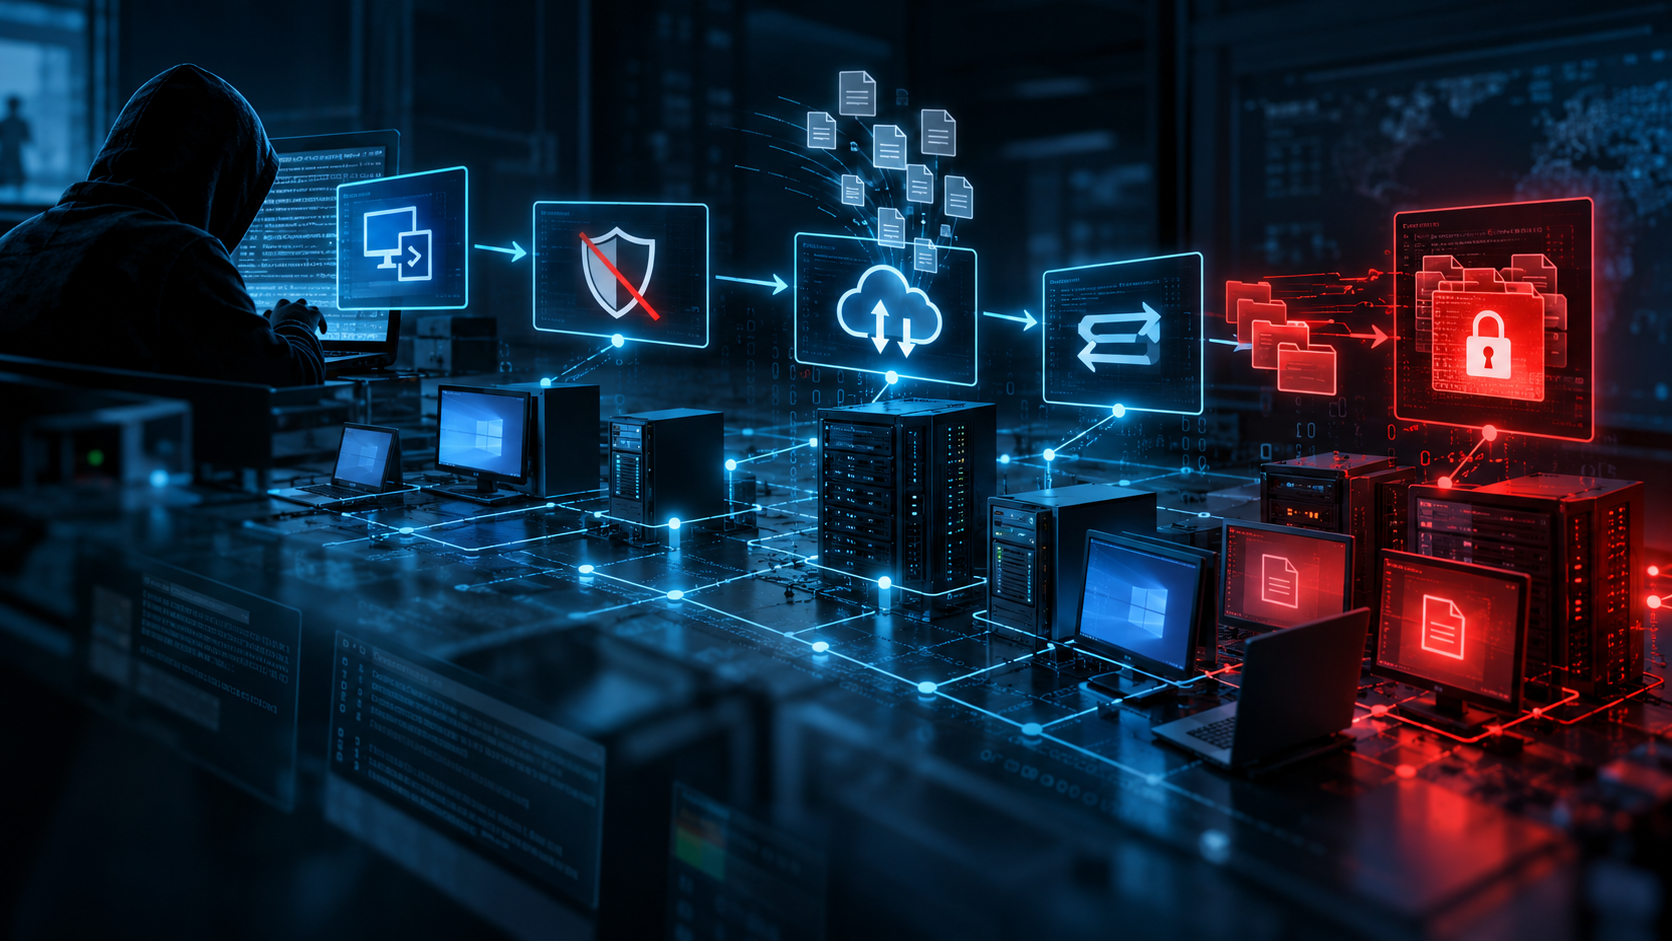 Huntress Analyzes Akira Ransomware Attack After EDR Failure In September 2026, Huntress deployed its agent at an organization already compromised by Akira ransomware. The post-compromise installation meant crucial EDR telemetry was missing, hindering initial access insights. Researchers reconstructed the attack using Windows Event Logs, Registry artifacts, and Akira log files.…