 Isc.Sans.Edu
CVE-2024-40766 Exploited by Ransomware Groups Targeting SonicWall Firewalls
Article Content

- •CVE-2024-40766 affects SonicWall firewalls, allowing unauthorized access and potential crashes.
- •Over 48,000 devices remain unpatched, making them prime targets for ransomware groups.
- •The MySonicWall breach has compromised configuration backups, increasing vulnerability.
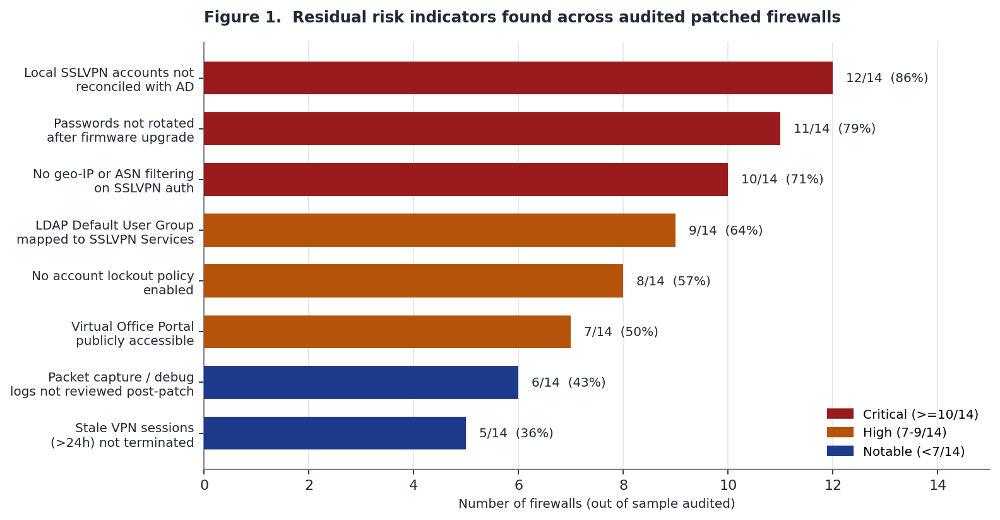
CVE-2024-40766 is an improper access control vulnerability in SonicWall SonicOS affecting Gen 5, Gen 6, and Gen 7 firewalls. The vulnerability, with a CVSS score of 9.3, allows unauthorized access and can crash the device. SonicWall serves approximately 500,000 businesses, many of which lack dedicated security teams. Ransomware groups Akira and Fog have exploited this vulnerability since September 2024, with significant compromises reported. By December 2024, nearly 49,000 devices were still publicly exposed and unpatched. Dwell times for attacks have been alarmingly short, with encryption occurring in under four hours in many cases. SonicWall's MySonicWall platform was also breached, exposing configuration backups and encrypted credentials. The exploitation has escalated in 2026, with ongoing attacks reported.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Akira, Sonicwall and CVE-2024-12802 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 SAP Exploits Surge: Days to Zero Report Highlights Critical Vulnerabilities A report from Onapsis Research Labs and Recorded Future reveals that the median time from the release of a SAP Security Note to the first public exploit has drastically decreased to 1-3 days, down from 489 days in 2021. The report analyzed over 1.2 million events and noted a 123% increase in underground discussions…
 Shift in Cyberattack Methods: Stolen Credentials Surpass Phishing Recent reports indicate a significant shift in cyberattack methods, with stolen credentials now accounting for 16% of intrusions, surpassing phishing at 14%. Mandiant's findings reveal that vulnerability exploits were the leading cause of intrusions at 33%. The decline in phishing, which previously accounted for…