
Ransomware Groups Medusa and DragonForce Exploit RMM Tools in 2025 Attacks
Article Content
Browse articles 
In 2025, ransomware groups Medusa and DragonForce targeted UK organizations by exploiting vulnerabilities in the SimpleHelp Remote Monitoring and Management platform. They leveraged three critical vulnerabilities (CVE-2024-57726, CVE-2024-57727, CVE-2024-57728) to gain unauthorized access through trusted third-party vendors and Managed Service Providers.
Ask AI about this cluster
Answers cite the sources they use
Updated 228d ago How this analysis works
More articles in this cluster (3)
Following this threat?
Track DragonForce and CVE-2024-57726 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Emerging EDR Killer Tool Targeting Ransomware Groups A new malicious tool, referred to as the EDR killer, is being actively used by at least eight ransomware groups, including Blacksuit and Medusa, to disable endpoint detection and response (EDR) solutions. This tool is believed to be an evolution of the EDRKillShifter developed by RansomHub, which allows ransomware…
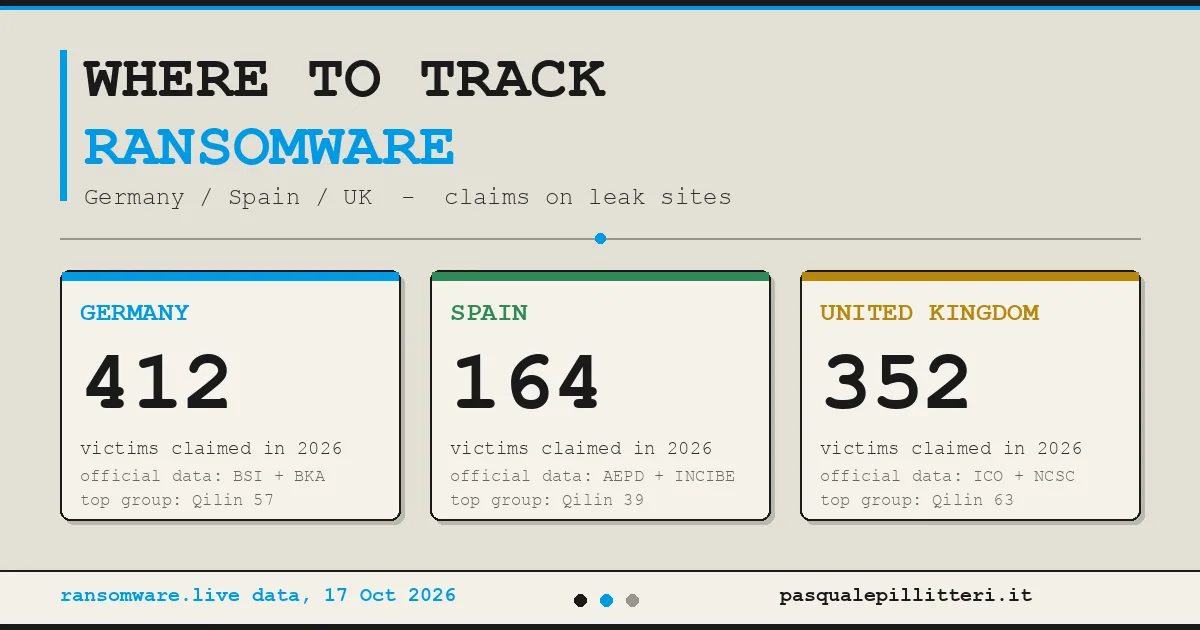 Ransomware Tracking and Data Breaches in France and Europe Cyberattaque.org, a French site, reports on multiple data leaks and cyberattacks affecting various sectors, including companies and political parties. The site, launched in March 2026, serves as an independent observatory but lacks verified sources and methods. It distinguishes between confirmed data leaks and claims…