 Techtimes
Russian GRU Hackers Use Fake CAPTCHAs to Compromise Ukrainian Users
Article Content

- •Sandworm hackers are using fake CAPTCHA prompts to trick users into executing malware.
- •Over ten Ukrainian websites have been compromised as part of this campaign since June 2026.
- •The command-and-control infrastructure is hidden within the Ethereum blockchain, complicating mitigation efforts.
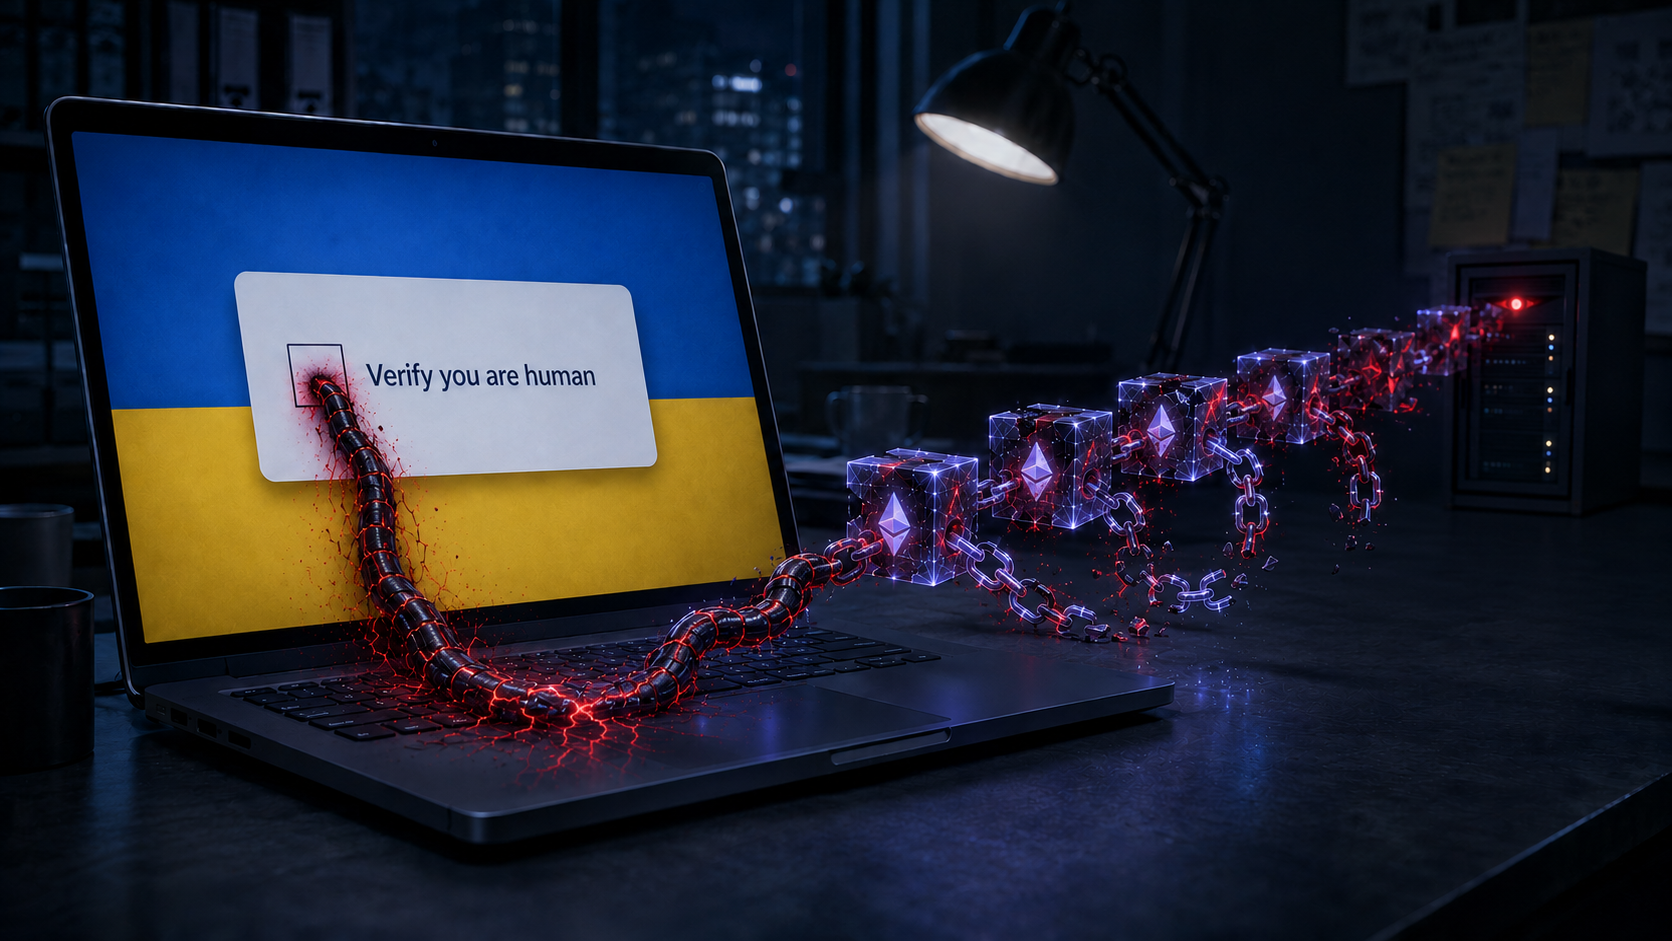
Ukraine's CERT-UA reported that the Russian GRU-linked hacking group Sandworm is employing fake CAPTCHA prompts to trick users into executing malicious PowerShell commands on their devices. This method, known as ClickFix, has surged in use, with over ten compromised Ukrainian websites identified since June 2026. The attackers, attributed to the UAC-0145 sub-cluster of Sandworm, exploit users' trust in technical prompts, leading them to unwittingly install malware. The malware includes a reconnaissance tool called ScoutCurl, which gathers sensitive information from infected systems. The campaign represents a significant shift in Sandworm's tactics, as they now hide their command-and-control infrastructure within the Ethereum blockchain, making it difficult to disrupt. The rise of ClickFix attacks has been alarming, with a reported 517% increase in such incidents during the first half of 2025. This trend poses a growing risk not only to Ukrainian users but also to computer users globally.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track Sandworm, ClickFix and Ethereum in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Russian Hackers Use Yggdrasil Network in Cyberattack on Ukrainian Grain Firm In July 2025, Russia-aligned hackers from UAC-0099 gained access to a Ukrainian grain logistics company via a phishing email. They deployed the MATCHWOK backdoor and later introduced a new backdoor, MythicRatatoskr, which communicated through the Yggdrasil decentralized network. This attack culminated in a data-wiping…
 UAC-0099 Enhances MATCHBOIL Malware Targeting Ukrainian Industries ESET Research has documented the evolution of MATCHBOIL, a C# downloader used by the Russia-aligned group UAC-0099, which has targeted Ukrainian transportation, manufacturing, and energy sectors. The malware, first noted by CERT-UA in August 2025, has been under development since at least April 2024. MATCHBOIL is…