Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
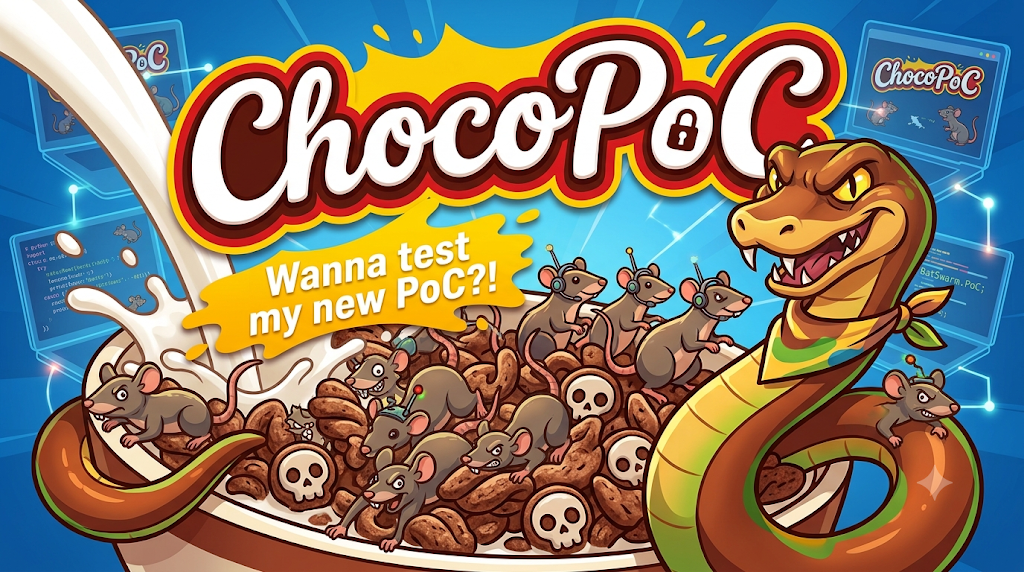
A coordinated supply chain attack has been identified, targeting vulnerability researchers and penetration testers through malicious proof-of-concept (PoC) repositories on GitHub. The malware, named ChocoPoC, is a Python-based remote access trojan (RAT) that stealthily exfiltrates sensitive data. At...
The MongoBleed vulnerability, tracked as CVE-2025-14847 with a CVSS score of 8.7, is currently under active exploitation. Over 87,000 potentially vulnerable MongoDB instances have been identified worldwide, posing a significant risk to affected systems. Cybersecurity researcher Joe Desimone has publ...
MongoDB has addressed a critical vulnerability, CVE-2025-14847, that allows unauthenticated remote attackers to execute arbitrary code on vulnerable servers. The flaw, with a CVSS score of 8.7, is linked to the server's zlib implementation. Organizations using affected MongoDB versions are advised t...
MongoDB has patched CVE-2025-14847, a vulnerability that affects multiple versions of MongoDB Server. The flaw allows unauthenticated attackers to remotely exploit the vulnerability with low complexity, potentially leading to the exfiltration of sensitive data and credentials. The vulnerability has...