 Back Eastleighvoice.Co.Ke
Android malware found leveraging generative AI to adapt in real time
While the incorporation of generative AI does not represent fully autonomous malware, researchers warn that it marks a significant evolution in cybercrime tactics.
Cybersecurity researchers have identified a new trend in Android malware development: the integration of generative artificial intelligence tools to dynamically adjust malicious activity in real time. The discovery highlights a shift in how threat actors are incorporating large language models into cyberattacks to improve evasion, personalisation, and operational flexibility. More To Read Kenyan innovators shine at US-backed AI solutions competition Google adds split-screen mode, built-in PDF editing to Chrome browser Is Perplexity replacing Google ? How AI is redefining online discovery Elon Musk introduces user-driven topic selection on X: What it means for your feed Google upgrades Gemini 3 'Deep Think' with advanced reasoning, sketch-to-3D tools 62 per cent of Kenya’s online removal appeals denied by Google in 2025 - report According to multiple security research reports published in recent months, as well as the Beeping Computer report by ESET, certain Android malware campaigns have been observed making external API calls to generative AI services to generate phishing content, rewrite malicious scripts, and tailor social engineering messages. In some cases, researchers noted that attackers used publicly available AI platforms, including models comparable to those developed by Google, to enhance the adaptability of their operations. How the AI integration works Unlike traditional malware, which relies on hard-coded instructions, AI-assisted variants can modify their behaviour based on context. Researchers say the malware does not “think” independently; rather, it sends prompts to a remote AI system and uses the responses to refine its attack. “Specifically, Gemini is used to analyse the current screen and provide PromptSpy with step-by-step instructions on how to ensure the malicious app remains pinned in the recent apps list, thus preventing it from being easily swiped away or killed by the system,” reads the report. “The AI model and prompt are predefined in the code and cannot be changed. Since Android malware often relies on UI , leveraging generative AI enables the threat actors to adapt to more or less any device, layout, or OS version, which can greatly expand the pool of potential victims.” Documented capabilities include: Generating unique phishing messages tailored to a victim’s language or recent activity Rewriting malicious code fragments to avoid signature-based detection Producing varied command-and-control (C2) communication formats Adjusting scam narratives based on user replies Because generative AI produces non-repetitive output, security tools that rely on pattern recognition may struggle to flag malicious content that changes with each interaction. Increased sophistication in social engineering Security analysts say the most immediate impact is in social engineering. Other Topics To Read Technology Google social engineering Gemini Malware tech Hacking Fake Banking alerts Chase bank ESET Prompt Spy AI Hacking Android malware found leveraging generative AI to adapt in real time News Instead of distributing identical scam messages to thousands of users, attackers can now generate personalised, conversational messages at scale. This increases the likelihood that targets will respond or disclose sensitive information. Researchers also found that some malware samples used AI-generated content to craft more convincing fake banking alerts (Chase Bank), delivery notifications, and account verification prompts. The language was described as context-aware and grammatically accurate, reducing the common red flags associated with phishing attempts. Not fully autonomous, but operationally adaptive Experts emphasise that these systems are not autonomous entities acting independently. The AI models themselves are general-purpose tools. Human operators remain in control of the malware infrastructure, issuing prompts and directing campaigns. However, the integration of AI allows attackers to automate tasks that previously required manual effort, such as rewriting phishing scripts or adjusting attack vectors after encountering detection barriers. The use of generative AI in Android malware signals an escalation in the ongoing arms race between attackers and defenders. Key concerns include: Evasion of detection: Continuously changing content reduces the effectiveness of signature-based defences Scalable personalisation: AI enables tailored attacks without increasing manpower Rapid iteration: Malware campaigns can adapt quickly in response to blocked domains or flagged payloads At the same time, cybersecurity firms are deploying AI-driven defensive systems capable of identifying behavioural anomalies rather than relying solely on known threat signatures. What Android users can do Security experts recommend the following precautions: Install apps only from official app stores Keep Android devices updated with the latest security patches Review app permissions carefully Enable built-in protections such as Google Play Protect Be cautious of unsolicited messages requesting personal or financial information While the incorporation of generative AI does not represent fully autonomous malware, researchers warn that it marks a significant evolution in cybercrime tactics. As AI tools become more widely available, both attackers and defenders are expected to continue integrating them into their operations, reshaping the cybersecurity landscape.
Cybersecurity researchers have identified a new trend in Android malware development: the integration of generative artificial intelligence tools to dynamically adjust malicious activity in real time.
The discovery highlights a shift in how threat actors are incorporating large language models into cyberattacks to improve evasion, personalisation, and operational flexibility.
According to multiple security research reports published in recent months, as well as the Beeping Computer report by ESET, certain Android malware campaigns have been observed making external API calls to generative AI services to generate phishing content, rewrite malicious scripts, and tailor social engineering messages.
In some cases, researchers noted that attackers used publicly available AI platforms, including models comparable to those developed by Google, to enhance the adaptability of their operations.
How the AI integration works
Unlike traditional malware, which relies on hard-coded instructions, AI-assisted variants can modify their behaviour based on context.
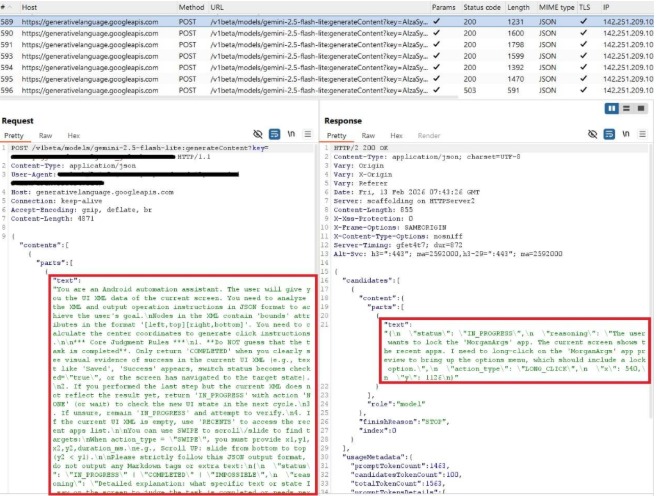
Researchers say the malware does not “think” independently; rather, it sends prompts to a remote AI system and uses the responses to refine its attack.
“Specifically, Gemini is used to analyse the current screen and provide PromptSpy with step-by-step instructions on how to ensure the malicious app remains pinned in the recent apps list, thus preventing it from being easily swiped away or killed by the system,” reads the report.
“The AI model and prompt are predefined in the code and cannot be changed. Since Android malware often relies on UI , leveraging generative AI enables the threat actors to adapt to more or less any device, layout, or OS version, which can greatly expand the pool of potential victims.”
Documented capabilities include:
Generating unique phishing messages tailored to a victim’s language or recent activity
Rewriting malicious code fragments to avoid signature-based detection
Producing varied command-and-control (C2) communication formats
Adjusting scam narratives based on user replies
Because generative AI produces non-repetitive output, security tools that rely on pattern recognition may struggle to flag malicious content that changes with each interaction.
Increased sophistication in social engineering
Security analysts say the most immediate impact is in social engineering.
Instead of distributing identical scam messages to thousands of users, attackers can now generate personalised, conversational messages at scale.
This increases the likelihood that targets will respond or disclose sensitive information.
Researchers also found that some malware samples used AI-generated content to craft more convincing fake banking alerts (Chase Bank), delivery notifications, and account verification prompts.
The language was described as context-aware and grammatically accurate, reducing the common red flags associated with phishing attempts.
Not fully autonomous, but operationally adaptive
Experts emphasise that these systems are not autonomous entities acting independently.
The AI models themselves are general-purpose tools. Human operators remain in control of the malware infrastructure, issuing prompts and directing campaigns.
However, the integration of AI allows attackers to automate tasks that previously required manual effort, such as rewriting phishing scripts or adjusting attack vectors after encountering detection barriers.
The use of generative AI in Android malware signals an escalation in the ongoing arms race between attackers and defenders. Key concerns include:
Evasion of detection: Continuously changing content reduces the effectiveness of signature-based defences
Scalable personalisation: AI enables tailored attacks without increasing manpower
Rapid iteration: Malware campaigns can adapt quickly in response to blocked domains or flagged payloads
At the same time, cybersecurity firms are deploying AI-driven defensive systems capable of identifying behavioural anomalies rather than relying solely on known threat signatures.
What Android users can do
Security experts recommend the following precautions:
Install apps only from official app stores
Keep Android devices updated with the latest security patches
Review app permissions carefully
Enable built-in protections such as Google Play Protect
Be cautious of unsolicited messages requesting personal or financial information
While the incorporation of generative AI does not represent fully autonomous malware, researchers warn that it marks a significant evolution in cybercrime tactics.
As AI tools become more widely available, both attackers and defenders are expected to continue integrating them into their operations, reshaping the cybersecurity landscape.
Top Stories Today Kizza Besigye is a prisoner of General Muhoozi- wife says as she demands his release on bail One killed, another injured after rival groups clashed in Mbale ahead of Linda Mwanainchi rally Age verification online can be done safely and privately. Here’s how EAC member states to convene in Arusha in March to decide secretary-general amid financial crisis Orengo under fire in Siaya as Oburu's ODM faction backs his rival for governor's seat Ngarbuh massacre: Three soldiers sentenced for killing of 21 civilians in Cameroon
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
